 Do Son
CVE-2026-44477 in CloudNativePG allows low-privilege users to gain root-level RCE via metrics exporters. Update to version 1.29.1 or 1.28.3 now!
cloud-native

A critical 9.6 CVSS flaw in Argo CD (CVE-2026-42880) allows read-only users to extract plaintext Kubernetes secrets via Server-Side Diffs. Patch to v3.3.9 now!

Kyverno (CVE-2026-4789) faces an unpatched SSRF flaw in its CEL HTTP functions, allowing attackers to bypass K8s namespaces. Secure your cluster now!
Google unveils AAOS SDV: a "headless" Android OS for Software-Defined Vehicles. Discover how it will power everything from climate control to digital twins.
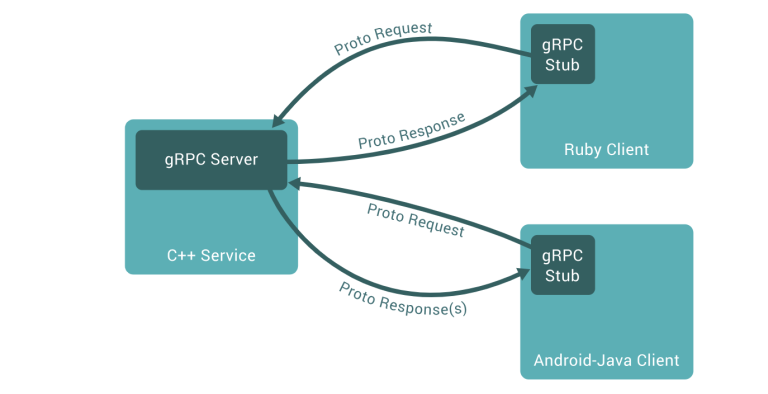
A critical 9.1 CVSS flaw in gRPC-Go (CVE-2026-33186) allows attackers to bypass authorization by omitting a leading slash. Upgrade to v1.79.3 immediately.

A high-severity 8.8 CVSS flaw (CVE-2026-4342) in ingress-nginx allows attackers to inject malicious code and steal Kubernetes Secrets. Patch immediately.
Vitess patches critical flaws (CVE-2026-27969 & 27965) where poisoned backup manifests lead to path traversal and RCE during restoration. Update to v23.0.3 now.

Critical Ingress-Nginx flaws (CVE-2026-1580) allow RCE and secret theft via config injection. Upgrade to v1.13.7 or v1.14.3 immediately to secure K8s.
Critical Kyverno flaw CVE-2026-22039 (CVSS 10) allows policy creators to gain cluster admin rights. Update to v1.16.3 to fix privilege escalation & DoS.

Trend Research warns that ransomware is shifting to AWS S3, exploiting misconfigured IAM and SSE-C keys in five attack variants to cause irreversible data loss and cloud-native extortion.

A critical flaw (CVE-2025-41240, CVSS 10.0) in Bitnami Helm charts exposes Kubernetes secrets via publicly accessible paths, allowing unauthenticated remote access. Update immediately!

HPE officially completed its $14B acquisition of Juniper Networks, doubling its networking business to bolster AI-native and cloud-native solutions in hybrid cloud infrastructure.

Apache CloudStack LTS updates patch five security flaws, including two critical vulnerabilities in Kubernetes and admin access, risking full system compromise.

A DoS flaw in CoreDNS (CVE-2025-47950) allows unauthenticated attackers to crash servers using DNS-over-QUIC. Update to 1.12.2 immediately or disable QUIC.

Kaspersky warns organizations are overestimating container isolation. New analysis reveals hidden attack surfaces and crucial detection blind spots.

Red Hat's new llm-d project, with industry leaders, aims to revolutionize large-scale generative AI inference for enterprises using Kubernetes and vLLM.

Discover the dangers of Sobolan Malware targeting Jupyter Notebooks and compromising cloud-native infrastructure.