 Do Son
A new StopRansomware advisory warns SafePay ransomware has hit 600+ victims via VPN logins and edge flaws. See its tactics and key defenses.
Critical Infrastructure
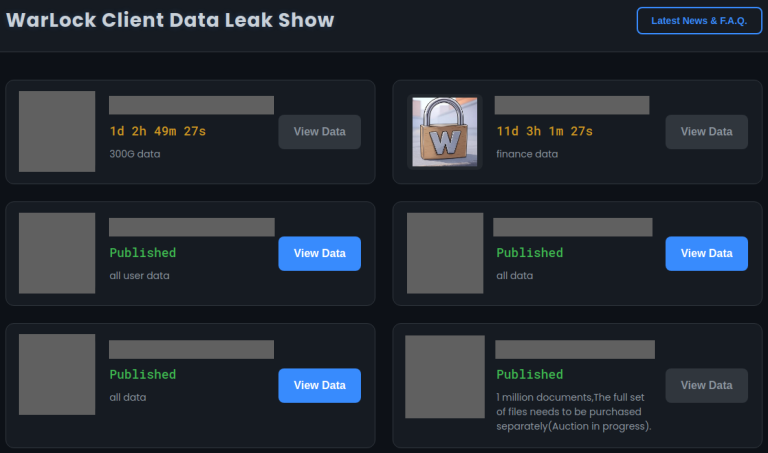
The Warlock ransomware group still exploits SharePoint vulnerabilities, hitting a water utility, a telecom firm, and more. Here is how to defend.
The DOJ and FBI seized QScan and QTRouter, platforms run by China state-sponsored hackers to hide attacks on U.S. critical infrastructure.

CISA and the NSA warn of an active Siemens PLC cyber threat using AI-generated exploit scripts disguised as monitoring tools. Protect your OT now.
The White House launched the GOLD EAGLE initiative for faster vulnerability coordination across U.S. critical infrastructure, using AI to patch flaws.
A 20-nation alert warns that Russia's FSB Center 16 is hacking vulnerable routers. The group targets critical infrastructure through weak SNMP settings.

Velvet Ant ran Operation Highland for nearly a decade, backdooring PAM and OpenSSH to hide inside an isolated critical infrastructure network.

Carlson VASCO-B GNSS receivers face a critical 9.4 CVSS flaw with zero authentication. Stop remote attackers from drifting your location data. Update to v1.4.0.

Critical 9.8 CVSS flaw (CVE-2026-6074) in Intrado 911 Gateway allows unauthenticated access to management tools. Protect emergency services and patch today.

Cato Networks reveals 235,500+ Modbus probes on PLCs across 70 countries. Learn how attackers fingerprint and hijack industrial control systems. Patch now.

Kaspersky uncovers Lotus Wiper, a destructive malware targeting Venezuela's energy sector. Designed for pure sabotage, it leaves systems unrecoverable.

Darktrace uncovers ZionSiphon, a malware strain targeting water treatment via Modbus logic. Discover the new frontier of Israel-focused industrial sabotage.

AVEVA alerts on a 9.3 critical flaw in Pipeline Simulation. Unauthenticated users can hijack admin roles and alter data. Upgrade to version 2025 SP1 P01 now.

FBI and CISA warn of Iranian APTs hijacking internet-facing PLCs to disrupt U.S. energy and water systems. Learn the 2026 TTPs and how to defend your OT.

Rockwell Automation issues an urgent warning: disconnect industrial controllers from the internet immediately to protect against active threat actors.

Iranian APT Seedworm intensifies cyberespionage against US and Israeli networks using a new stealth backdoor called Dindoor. Read the full threat report.
A critical 9.4 CVSS flaw (CVE-2026-1775) in Labkotec LID-3300IP ice detectors allows hackers to hijack wind turbines and airports. Hardware upgrade needed.
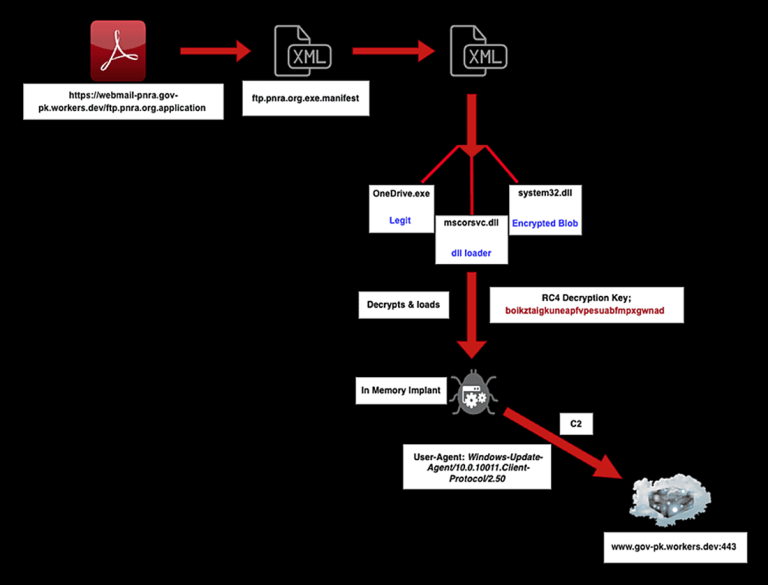
Arctic Wolf details a year-long cyber espionage campaign by Sloppy Lemming, deploying the custom BurrowShell malware against Pakistan and Bangladesh.

CISA issues an urgent ICS advisory (ICSA-26-057-04) for the EV2GO charging platform. Critical 9.4 severity flaws allow for session hijacking and station impersonation.

Recorded Future’s Insikt Group warns of a two-year escalation in Russian hybrid warfare. From cyber sabotage to airspace incursions, NATO faces a new doctrine.

Cisco Talos warns of CVE-2026-20127, a CVSS 10 flaw in Catalyst SD-WAN exploited since 2023. UAT-8616 bypassed authentication to hijack global network fabrics.

CISA warns of critical Airleader Master vulnerability CVE-2026-1358. Unauthenticated attackers can upload files and gain RCE. Update to 6.386 now.