 Do Son
Oracle fixed 98 MySQL vulnerabilities in October 2026, including CVSS 9.8 bugs CVE-2025-15467 in OpenSSL and CVE-2026-9547 in curl.
Critical Patch Update
A CVSS 10.0 E-Business Suite vulnerability, CVE-2026-101809, lets unauthenticated attackers take over Workflow. Oracle fixed 194 EBS flaws.
Oracle Fusion Middleware vulnerabilities include four CVSS 10.0 bugs such as CVE-2026-87337 in Access Manager and SOA Suite takeover flaws.
Oracle Critical Patch Update for October 2026 fixes 1,209 CVEs, including six CVSS 10.0 bugs such as CVE-2026-101809 in E-Business Suite.

Oracle patches CVE-2026-21962 (CVSS 10) in Fusion Middleware. This critical flaw allows unauthenticated server takeover. Update immediately.

SAP released its Patch Day update fixing 18 flaws, including two Critical (CVSS 10.0) vulnerabilities: RMI-P4 RCE and Hard-Coded Credentials in SQL Anywhere Monitor, risking unauthenticated takeover.

Oracle's October CPU fixes 374 flaws, including two Critical RCE bugs (CVSS 9.8) in EBS Marketing. The vulnerabilities allow unauthenticated takeover of the application.
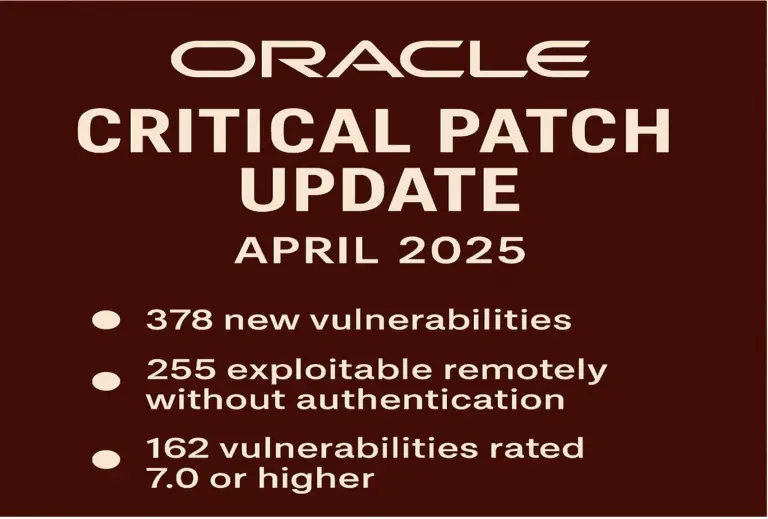
Oracle's April 2025 CPU delivers 378 security patches across its product suite. Learn about critical vulnerabilities and the urgent call to update.
Oracle released the patches for Oracle Database Server Risk Matrix, Oracle Communications Applications Risk Matrix, Oracle Construction...