 Do Son
The OpenSSL 4.1.0 release introduces initial Elbrus e2k architecture support, DTLS 1.3 protocol capabilities, and post-quantum performance upgrades.
cryptography
Security enthusiasts minted 106,000 eMudhra rogue certificates for Google domains after researchers uncovered trivial private keys in intermediate CAs.
Vals AI used the newly released Claude Fable 5.1 model to successfully decrypt Thomas Urquhart's 370-year-old Cyphral Distich.

A massive configuration error at DENIC paralyzed millions of .de domains. Discover how a routine DNSSEC key rotation caused a nationwide internet blackout.

GnuTLS v3.8.13 fixes critical heap overwrites, identity truncation, and OCSP bypasses. Secure your Linux comms and upgrade to the latest version now.

wolfSSL (CVE-2026-5194) faces a critical 9.3 CVSS flaw in ECDSA certificate validation. Attackers can bypass security and spoof trusted hosts. Audit today!

Apache OpenMeetings 9.0.0 fixes critical flaws including hard-coded "remember-me" keys and REST login credential exposure. Secure your video suite today!

Researchers discovered three major flaws in Amazon’s AWS-LC cryptographic library, allowing hackers to bypass digital signature validation. Update now.
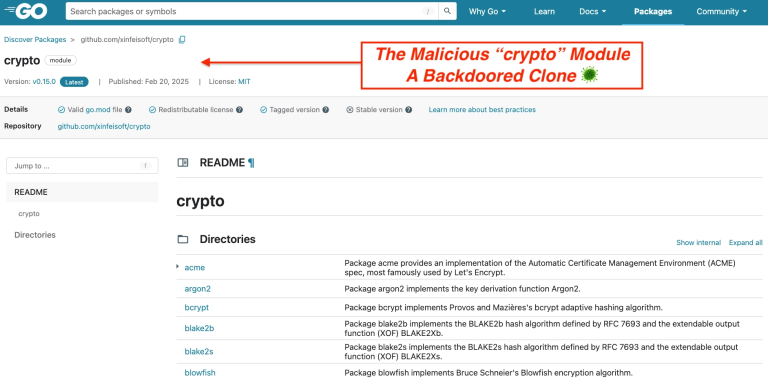
Socket uncovers a malicious Go module mimicking golang.org/x/crypto. It steals passwords via ReadPassword and deploys the Rekoobe backdoor on Linux systems.

IBM warns of critical flaw CVE-2025-13375 (CVSS 9.8) in CCA software. Unauthenticated attackers can hijack HSMs. Update to v7.5.53/v8.4.84 now.

OpenSSL patches 12 flaws, including high-severity CVE-2025-15467 allowing pre-auth RCE via CMS. Update to 3.6.1/3.0.19 immediately to secure systems.

CVE-2025-13151: A one-byte overflow in GNU libtasn1 risks memory corruption during cert parsing. Patch now to secure your cryptographic applications.

Deno, CVE-2026-22863, CVE-2026-22864, JavaScript Security, Cryptography, Command Injection, Windows Security, Node.js Compatibility, Patch Alert

A Critical flaw (CVE-2025-12816) in node-forge allows attackers to bypass signature verification by manipulating ASN.1 structures. The vulnerability affects 21M+ weekly downloads. Update to v1.3.2.

A Babuk successor, Midnight ransomware, contains a critical flaw in its RSA key handling. Gen researchers created a free decryptor that bypasses the encryption, allowing victims to recover files.
OpenSSL patches three flaws, including CVE-2025-9230 (RCE/DoS risk) and a SM2 timing side-channel (CVE-2025-9231) that could allow private key recovery on ARM64.
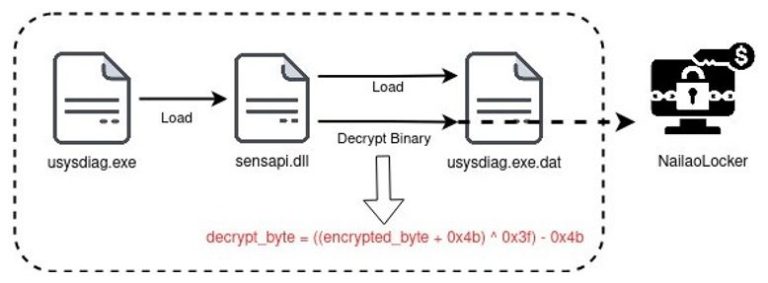
FortiGuard Labs unveils NailaoLocker, a new ransomware using Chinese SM2 encryption and a built-in, non-functional decryptor, suggesting a prototype or decoy.

wolfSSL 5.8.2 patches four vulnerabilities, including a critical Apple trust store bypass (CVE-2025-7395) and predictable randomness after fork(), impacting secure communications.

Two critical flaws (CVE-2025-6545, CVE-2025-6547, CVSS 9.1) in pbkdf2 npm package allow silent compromise of cryptographic keys. Update to 3.1.3+ immediately!

A critical cryptographic flaw in Meshtastic (CVE-2025-52464) allows message decryption and node hijacking due to duplicated/low-entropy keys.

A TPM 2.0 flaw (CVE-2025-2884) allows local attackers to access sensitive memory or cause DoS. Update TPM firmware to protect trusted computing.

A critical vulnerability (CVE-2025-27840) in ESP32 microcontrollers threatens billions of IoT devices and the security of Bitcoin wallets. Exploits range from private key theft to forged transactions.