 Do Son
A Skynet LLMjacking agent hijacks exposed AI models to scan, hack servers and mine crypto for 100,000 steps, while victims pay the bill.
Cryptojacking
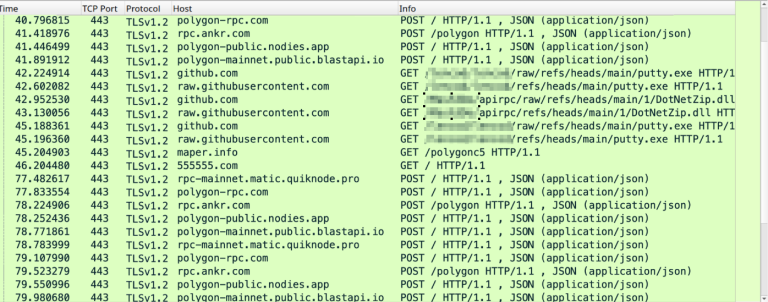
The Aeternum blockchain botnet hides C2 commands inside Polygon smart contracts, evading takedowns while dropping XWorm and XMRig payloads.
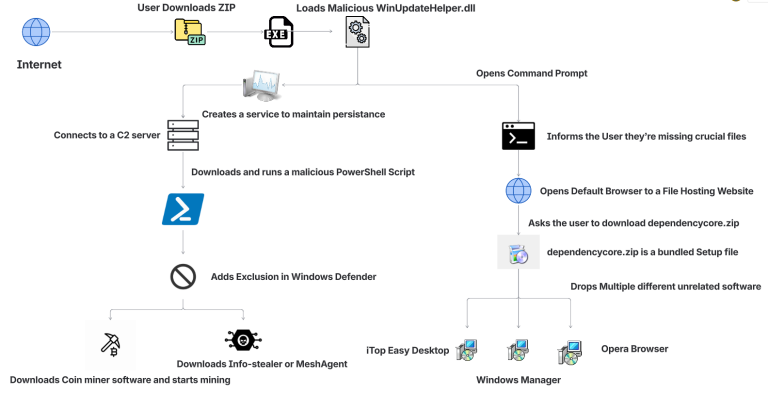
McAfee researchers found a massive malware campaign using LLMs to "vibe code" 1,700+ fake downloads. From Roblox mods to AI tools, your PC is the target.
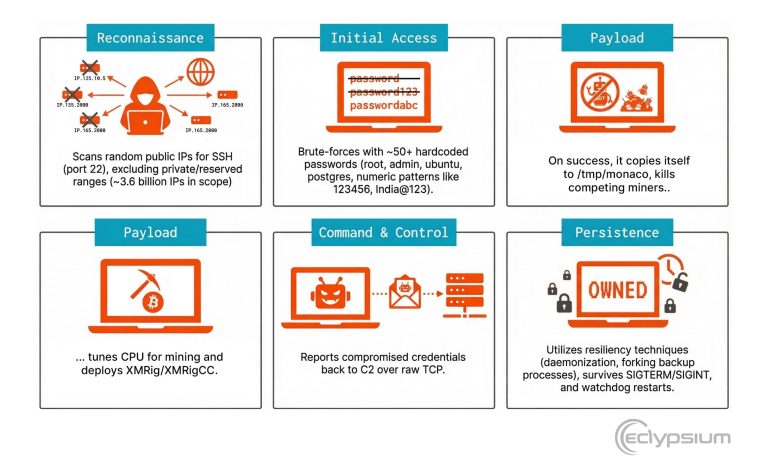
Eclypsium uncovers two new Linux malware strains: a CondiBot DDoS variant and the Monaco SSH cryptominer targeting servers and IoT. Secure your network.

Hackers are weaponizing AWS termination protection to lock defenders out while they mine crypto on hijacked ECS/EC2 resources using a malicious Docker image.

GhostGrab is a hybrid Android malware that steals banking credentials and OTPs via phishing WebView overlays while secretly running a Monero miner in the background to monetize the victim's device.
Cisco Talos exposed Famous Chollima using fake job offers and a trojanized Node.js app (Chessfi) to infect developers. The OtterCookie RAT steals crypto wallets, credentials, and source code.
McAfee uncovered the Astaroth banking Trojan using GitHub for C2 backup, hiding encrypted configuration data via steganography in images to target Brazilian financial and crypto users.

McAfee uncovers a new Android malware campaign targeting Indian users. The malware impersonates major banks to steal financial data and silently mines Monero in the background.

Aqua Security's Nautilus team discovered Koske, an advanced Linux cryptojacker likely crafted by AI, hiding in panda images and using rootkits for stealthy operations.

Wiz Research uncovers Soco404, an evolving cryptojacking operation exploiting cloud misconfigurations and PostgreSQL to stealthily mine cryptocurrency across Linux and Windows.

The Mimo threat actor has broadened its scope to Magento, employing advanced persistence, fileless execution, cryptojacking, and proxyjacking in a sophisticated new campaign.
Splunk exposes a campaign weaponizing Inno Setup installers to deploy RedLine Stealer, using obfuscated Pascal scripts and HijackLoader to steal browser/crypto data.

XMRig cryptojacking is surging, leveraging LOLBAS techniques, PowerShell, and Scheduled Tasks to mine Monero undetected, with a 45% rally in XMR price driving the attacks.

Wiz Research Team uncovers rapid exploitation of exposed JDWP interfaces, deploying XMRig cryptominers in TeamCity and other Java environments within hours of exposure.

Trend Micro uncovers a new attack method using misconfigured Docker Remote APIs and the Tor network to stealthily deploy cryptominers and establish persistent access.

Librarian Ghouls APT launches a new cyber-espionage and cryptojacking campaign targeting Russia and CIS, using legitimate tools for stealth.

Blitz malware infects gamers via backdoored Standoff 2 cheats, stealing data and cryptojacking. It uses Hugging Face for C2 and targets Windows users globally.

Wiz uncovers JINX-0132, a cryptojacking campaign exploiting misconfigured Nomad, Consul, Docker, and Gitea in DevOps environments to mine Monero.

RedisRaider malware exploits misconfigured Redis servers to deploy cryptominers via cron jobs, evading detection with obfuscation and anti-forensics.

Learn about the ISP Infostealer Campaign and its severe impacts on ISP infrastructure through brute force and data exfiltration.

Exploitation of CVE-2024-50603 is already occurring in the wild. Wiz Research observed attackers deploying cryptocurrency miners (XMRig) and backdoors