
 Do Son
Read our latest weekly threat intelligence briefing. This active vulnerability update reveals critical Microsoft Exchange and Oracle flaws for July 2026.
cybersecurity news

Read our weekly threat intelligence briefing. This vulnerability management report covers active exploits in Cisco, Ivanti, and Chrome for June 2026.
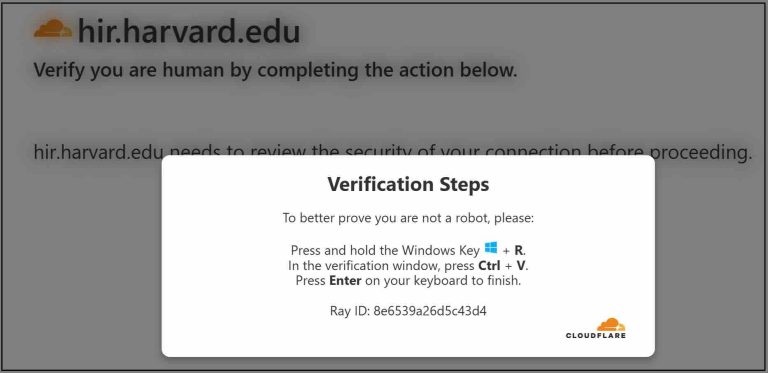
XLab uncovers a massive Ghost CMS poisoning campaign utilizing CVE-2026-26980 to launch FakeCaptcha attacks. Learn how to secure your site.

CVE-2026-48095 (CVSS 8.8) is a heap buffer overflow in 7-Zip that a crafted archive can trigger. Update to the patched version now.

Read our weekly threat intelligence briefing. Discover active exploits, critical CVEs, and the latest CISA KEV additions for May 18–24, 2026.

Cloudflare cuts 1,100+ jobs despite beating Q1 earnings. CEO Matthew Prince cites a 600% surge in AI agent use as the catalyst for this "AI-first" metamorphosis.
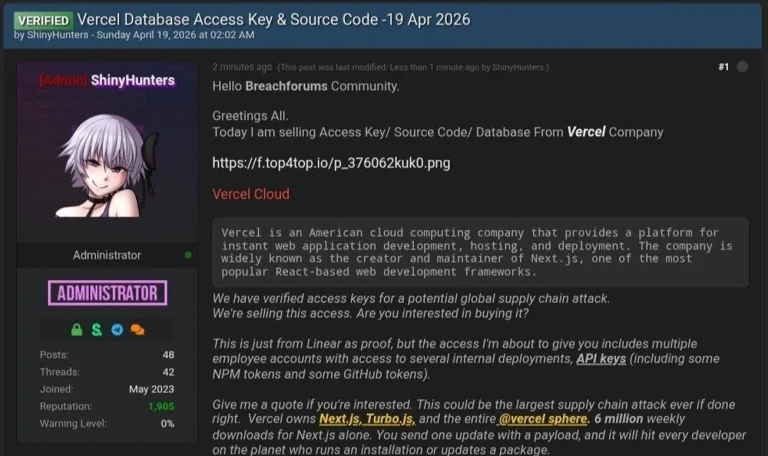
Vercel investigates a major breach by ShinyHunters. With Next.js source code and tokens at risk, developers must rotate secrets immediately. Stay updated.

A high-severity flaw in OpenClaw (formerly Clawdbot) allows 1-click Remote Code Execution. Update to v2026.1.29 immediately to prevent total account takeover.
CISA warns of active exploitation of OpenPLC ScadaBR (CVE-2021-26829). This critical Stored XSS flaw puts SCADA systems at risk. Update now.

The new Sturnus Android banking trojan bypasses end-to-end encryption on WhatsApp & Signal and enables full device takeover for hidden financial fraud.

Week of April 7-13 saw critical Ivanti, WordPress, & Windows vulnerabilities exploited, plus major data breaches impacting millions.