 Do Son
Two critical Portainer vulnerabilities enable a bind mount bypass and Docker host takeover by standard users. Upgrade to Portainer 2.45.2 now.
docker
Patch CVE-2026-110005 (CVSS 9.9), a critical Komodo Periphery vulnerability allowing authenticated users to run arbitrary OS commands as root on the host.
Docker released an update for critical Docker Sandboxes vulnerabilities (CVE-2026-77179, CVE-2026-79994). Patch these Docker Sandboxes vulnerabilities today.
Plex urges an urgent security update to Media Server 1.43.3 and Desktop 1.115.0. NAS and Docker users may need to patch manually.
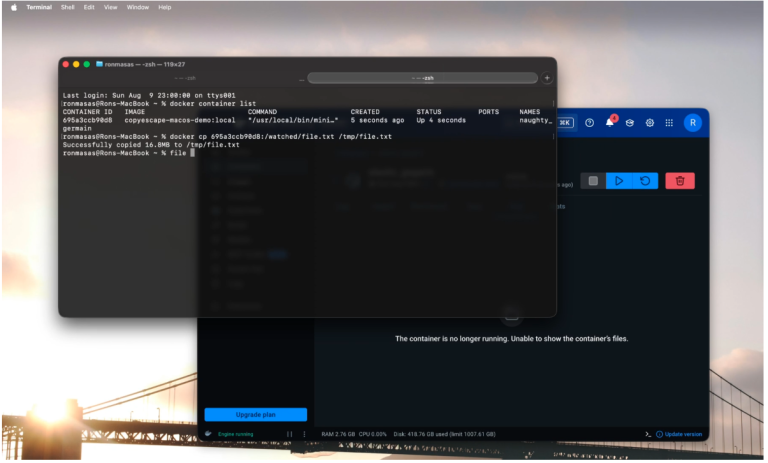
CVE-2026-17106 (CVSS 7.1) is the Docker CopyEscape vulnerability, letting malicious containers overwrite host files and trigger code execution.
Kimai vulnerability CVE-2026-52824 (CVSS 9.1) lets attackers forge cookies for account takeover via a default Docker APP_SECRET. Update to 2.58.0 now.
Unauthenticated attackers can hijack mailcow admin sessions via a critical CVSS 9.3 Stored XSS in Autodiscover logs. Patch to version 2026-03b immediately.
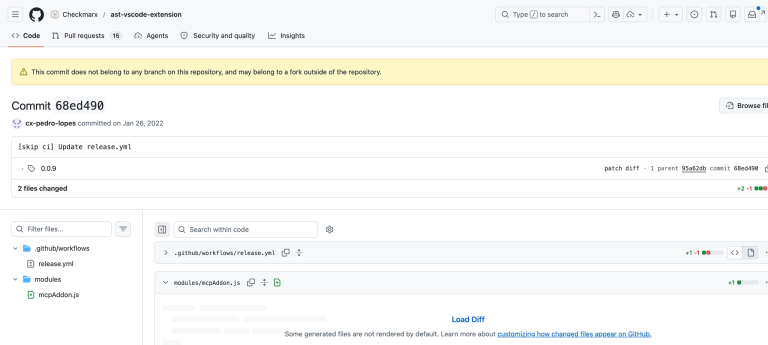
Checkmarx Docker images and VS Code extensions hijacked by TeamPCP to siphon cloud secrets and spread via npm. Audit your "Dune" repositories today.
CERT/CC warns of critical flaws in CrewAI. Insecure fallbacks and prompt injection enable RCE and SSRF. No full patch yet—learn how to secure your agents.

A developer's Mac home directory was wiped after Claude AI executed an unconstrained rm -rf ~/ command. Experts urge using Docker to contain AI coding tools for safety.

OCI patched three critical runc flaws allowing container escape and host DoS/RCE. Attackers exploit mount race conditions in maskedPaths and /dev/console bind-mounts. Update to v1.2.8+.

A critical flaw (CVE-2025-59951) in the Termix Docker image's reverse proxy logic allows unauthenticated attackers to steal sensitive SSH host credentials. Update to v1.7.0 now.

A new DDoS-as-a-service botnet, ShadowV2, uses GitHub CodeSpaces and Docker to mimic legitimate cloud apps, bypassing traditional defenses and enabling powerful attacks.

A critical vulnerability (CVSS 9.3) in Docker Desktop could allow malicious containers to gain full control of the host system. Update now to version 4.44.3.

With macOS Sequoia, Apple introduces a native containerization system, enabling security professionals to run Kali Linux directly on Apple Silicon for penetration testing without needing Docker.

Trend Micro uncovers a new attack method using misconfigured Docker Remote APIs and the Tor network to stealthily deploy cryptominers and establish persistent access.

Kaspersky warns organizations are overestimating container isolation. New analysis reveals hidden attack surfaces and crucial detection blind spots.
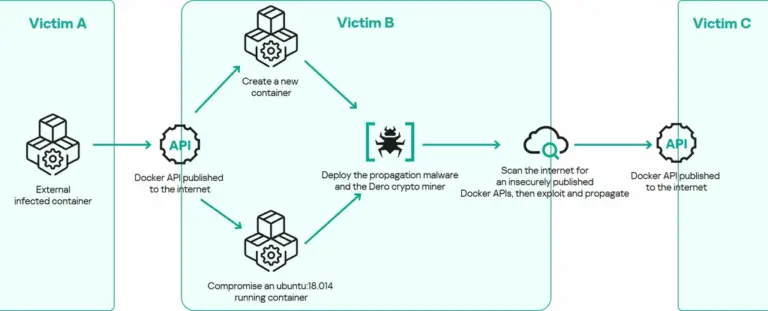
A new self-replicating Dero cryptominer is infecting exposed Docker containers, spreading as a worm without needing a C2 server.

A critical containerd flaw (CVE-2025-47290) allows malicious container images to hijack the host filesystem. Update to version 2.1.1 now.

CVE-2024-0132: This report details how an incomplete NVIDIA Container Toolkit patch allows container escape and denial-of-service (DoS) attacks, affecting AI systems and Docker on Linux

A vulnerability in Jenkins Docker images (CVE-2025-32754, CVE-2025-32755) allows SSH host key reuse, enabling attackers to intercept and modify build processes. Update to jenkins/ssh-agent 6.11.2 to mitigate.

Discover how cybercriminals use gRPC over h2c to deploy SRBMiner on Docker servers and mine XRP cryptocurrency.