 Do Son
A Rust supply chain attack poisoned arrayref and two other crates to run malware at build time. Wiz ties the infrastructure to DPRK campaigns.
DPRK
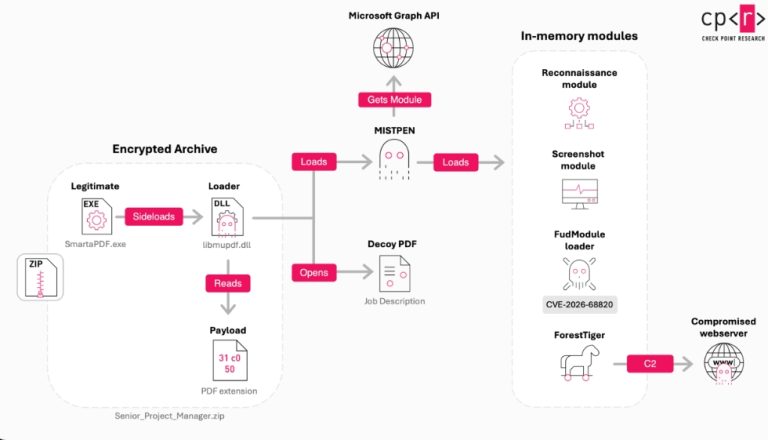
Lazarus exploited a Windows zero-day (CVE-2026-68820) in Operation Dream Job to hit defense firms with fake job offers and a new backdoor.
Amazon ties North Korean hackers to open-source supply chain attacks on the axios, debug, and chalk NPM packages. Here's how the campaign worked.
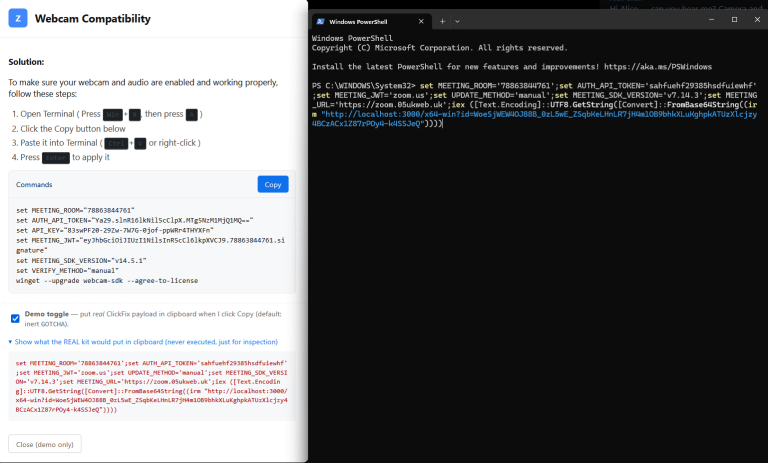
JUMPSEC analyzed the BlueNoroff phishing kit's source code. The DPRK ClickFix attack fakes Zoom and Teams calls to profile and drain crypto wallets.

Elastic found a Contagious Interview campaign using fake coding interviews and SVG steganography to steal developer credentials and crypto wallets.

DOJ sentences U.S. enablers for running North Korean "laptop farms." Learn how the DPRK breached 70 companies and funded weapons via stolen identities.
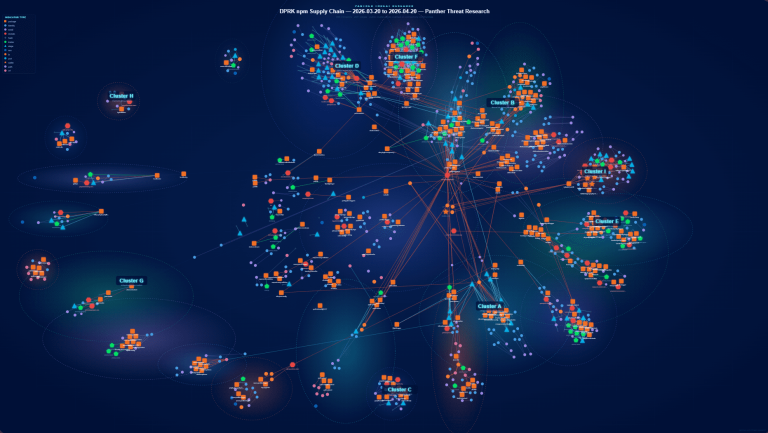
Panther Research exposes a massive 2026 DPRK npm campaign using blockchain dead-drops to steal crypto keys and AI secrets. Secure your CI/CD pipelines now.
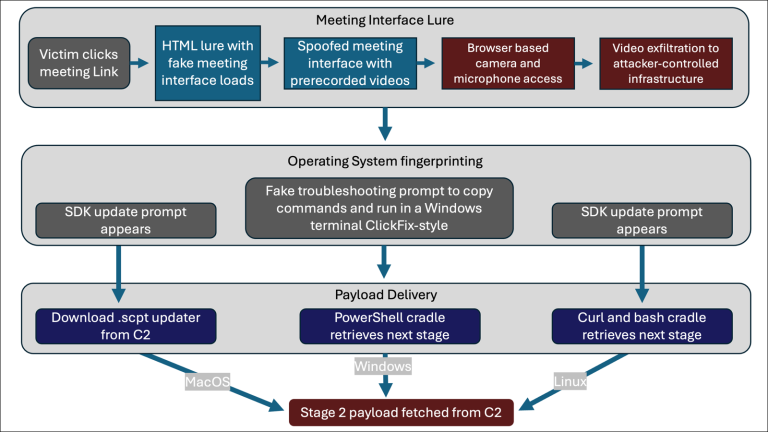
BlueNoroff uses a "self-reinforcing" deepfake pipeline to target crypto CEOs. Fake Zoom meetings and stolen footage lead to a 5-minute system compromise.
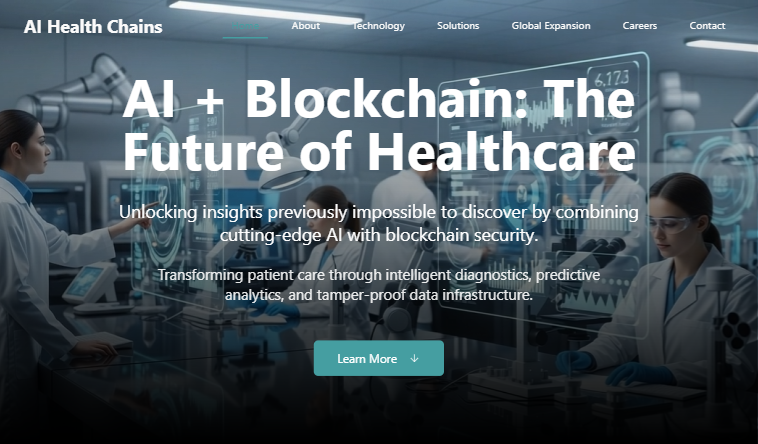
North Korean group HexagonalRodent stole millions in Q1 2026 using AI-generated lures and backdoored VS Code tasks. Protect your Web3 wallet now.
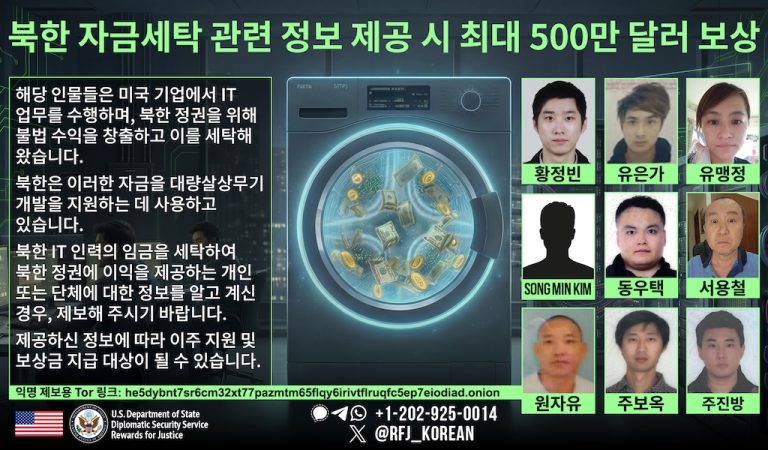
Two NJ residents sentenced for running a "laptop farm" allowing North Korean workers to infiltrate 100+ U.S. companies and steal $5M in revenue.
PolinRider targets 1,900+ GitHub repos using "history-falsification" to hide malware. DPRK's Lazarus Group uses fake job tests to breach developers.

Panther uncovers "OtterCookie," a North Korean npm campaign hiding malware in benign wrappers. It steals crypto wallets and installs SSH backdoors. Audit now!
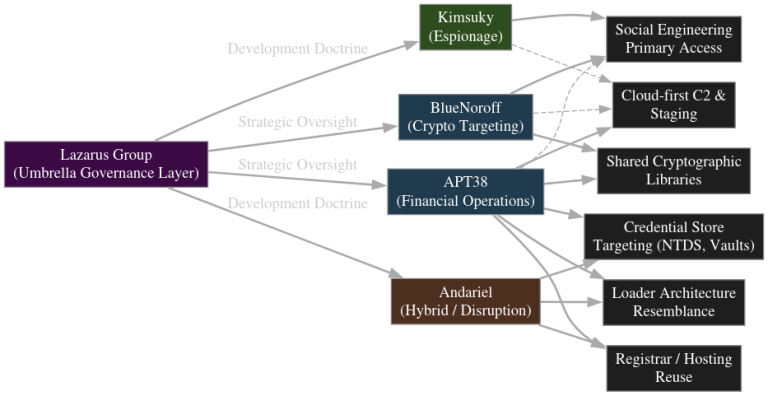
DomainTools exposes North Korea’s "mature portfolio model": a compartmentalized cyber strategy designed for mission specialization and attribution resistance.
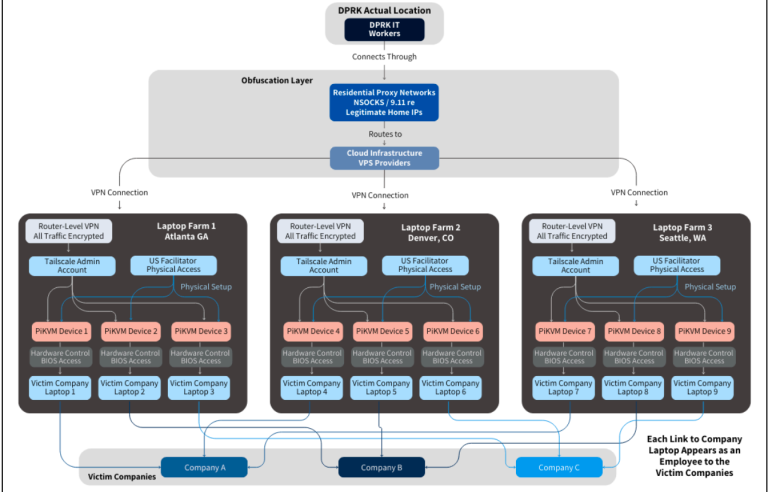
Nisos exposes a North Korean IT worker scheme involving a Florida-based laptop farm, AI-generated resumes, and PiKVM devices. Don't fall for the ruse.
Okta exposes North Korean IT workers using AI photos & stolen LinkedIn profiles to land remote jobs. Learn how "JJ" bypassed checks.

DPRK spies weaponize Visual Studio Code tunnels to bypass security. Darktrace reveals a campaign targeting South Korea with government decoys.

"Contagious Interview" evolves: DPRK hackers now abuse VS Code tasks & npm install to breach developer systems. Jamf warns of new infection vectors.

A joint Hunt.io and Acronis report exposes the shared infrastructure behind Lazarus and Kimsuky, revealing the unified web of North Korean hacking.

Kimsuky is deploying a new DOCSWAP RAT via QR codes and smishing. The DPRK-linked malware turns phones into surveillance tools for data theft.
NVISO exposed the Contagious Interview APT using JSON Keeper and npoint.io as covert C2 channels. The North Korean group uses fake job lures on GitLab to deploy BeaverTail to steal Web3 credentials.

OFAC sanctioned Song Kum Hyok (Andariel) and others for orchestrating North Korea's remote IT worker scheme, which used stolen identities to fund DPRK weapons programs.

The DOJ dismantled a North Korean scheme exploiting remote IT jobs at 100+ U.S. firms, using stolen identities and laundering millions to fund DPRK weapons programs.