 Do Son
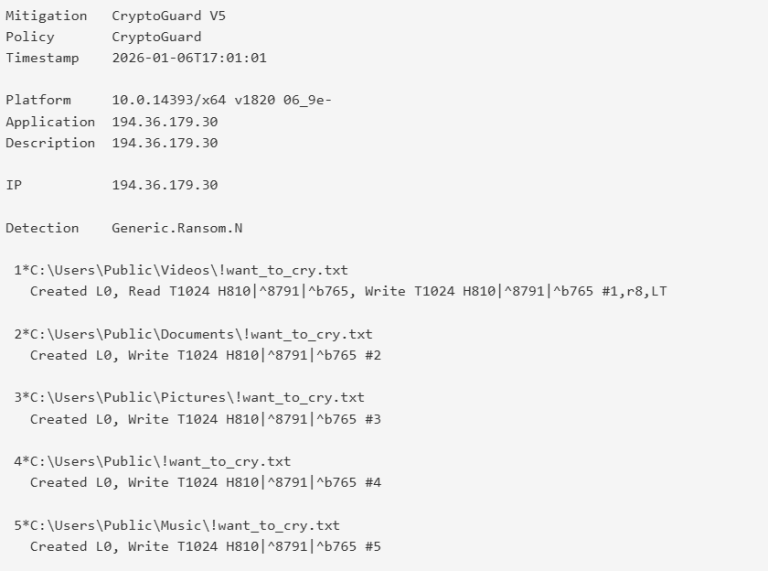
Sophos exposes WantToCry, a remote ransomware campaign that avoids EDR by using brute-forced SMB shares to read, encrypt, and rewrite files from afar.
EDR evasion

ReliaQuest warns Initial Access Broker "KongTuke" is abusing external Microsoft Teams chats to deploy the highly resilient ModeloRAT. Audit tenants now!

A new technique, "EDR-Freeze," uses a built-in Windows feature to suspend antivirus and EDR processes, giving attackers a critical window to operate undetected.

Sophos uncovers GOLD SALEM, a new ransomware group exploiting SharePoint flaws. The group uses EDR evasion and legitimate tools to attack global targets.

Matanbuchus 3.0, a new sophisticated malware loader, is using social engineering via Microsoft Teams to infiltrate enterprise systems with advanced evasion tactics.

Discover Waiting Thread Hijacking, a novel process injection technique that bypasses EDR systems. Learn how it stealthily executes code in remote processes.

Find out how an attacker used an EDR evasion tool to bypass security defenses and the important discovery that followed.

The notorious threat group GhostEmperor has resurfaced with an updated version of its sophisticated Demodex rootkit