 Do Son
The Windows 11 KB5127648 update breaks enterprise Windows 11 Wi-Fi authentication on 802.1X networks. Discover the root cause and registry workaround.
Enterprise Security
A critical Collibra Platform Agent flaw chains with a Zip Slip vulnerability during extraction routines to grant unauthenticated remote code execution.
LevelBlue SpiderLabs reveals how traditional malware now integrates crypto drainers and uses blockchain for C2. A major shift in enterprise risk.

Cisco warns of active exploitation for CVE-2026-20133 in Catalyst SD-WAN Manager. Unauthenticated attackers can leak OS data. Patch by April 24, 2026.
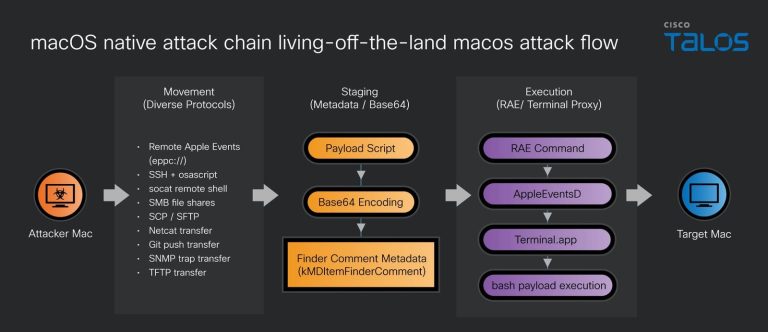
Cisco Talos reveals how attackers use native macOS features like Spotlight and SNMP to hijack enterprise workstations. Secure your DevOps environment today.

SAP’s April 2026 updates fix a critical 9.9 CVSS SQL injection in Business Warehouse and 19 other security flaws. Audit your S/4HANA and BPC systems today.

Gmail brings "One-Touch" end-to-end encryption to Android and iOS. Learn how Workspace Enterprise users can now secure sensitive emails natively on mobile.

Weaver E-cology 10.0 faces a critical 9.3 CVSS RCE (CVE-2026-22679). Unauthenticated attackers can hijack servers via a debug endpoint. Patch immediately!

Fortinet warns CVE-2026-35616 (CVSS 9.1) in FortiClient EMS is being exploited in the wild. Unauthenticated RCE risk—apply emergency hotfixes immediately!

SAP's latest security update addresses 15 flaws, including critical RCE (CVE-2019-17571) and deserialization (CVE-2026-27685) vulnerabilities. Patch now.

HPE warns of a critical CVSS 10.0 vulnerability (CVE-2026-23600) in AutoPass License Server. Remote attackers can bypass authentication. Patch to 9.19 now!
Akamai SIRT reveals Zerobotv9, a new Mirai-based botnet targeting enterprise n8n workflow platforms and Tenda routers via critical vulnerabilities.

Hackers abuse Atlassian Jira notifications to bypass spam filters. Trend Micro warns of scams targeting enterprise users via trusted alerts.

Apache Karaf Decanter flaw CVE-2026-24656 allows unauthenticated attackers to crash the log collector via deserialization. Update to v2.12.0 immediately.
CISA adds VMware vCenter flaw CVE-2024-37079 (CVSS 9.8) to KEV catalog. Hackers are actively exploiting this RCE bug. Patch immediately.

Oracle patches CVE-2026-21962 (CVSS 10) in Fusion Middleware. This critical flaw allows unauthenticated server takeover. Update immediately.

Urgent: Zoom Node vulnerability CVE-2026-22844 (CVSS 9.9) allows command injection. Update MMR modules to v5.2.1716.0 now to prevent remote attacks.
Socket discovers 5 malicious Chrome extensions posing as productivity tools. They steal session tokens & block security teams. 2,300+ enterprise users at risk.

Microsoft confirms KB5073455 causes Windows 11 23H2 Enterprise PCs to restart instead of shutting down. Use the shutdown /s /t 0 workaround now.

Microsoft’s Build 26220.7535 introduces a targeted Group Policy to uninstall Copilot on managed enterprise devices after 28 days of inactivity.

Public PoC released for Trend Micro Apex Central RCE (CVE-2025-69258). Unauthenticated attackers can gain SYSTEM access. Update to Build 7190 now.

CVE-2025-14026: Attackers can reconstruct a crippled Python runtime in Forcepoint DLP to execute arbitrary code. Update now to remove the vulnerability.