 Do Son
The DOJ and FBI raided DPRK IT worker laptop farms in Texas, seizing 187 devices and charging 14 suspects in a $3M fraud scheme hitting 70+ US firms.
Famous Chollima

North Korea's ClickFake Interview campaign targets crypto pros with fake skill tests, dropping the PylangGhost RAT on Windows and GolangGhost on macOS.
Socket links the PolinRider supply chain attack to North Korean hackers. The campaign hid loaders in 108 open-source packages across four ecosystems.
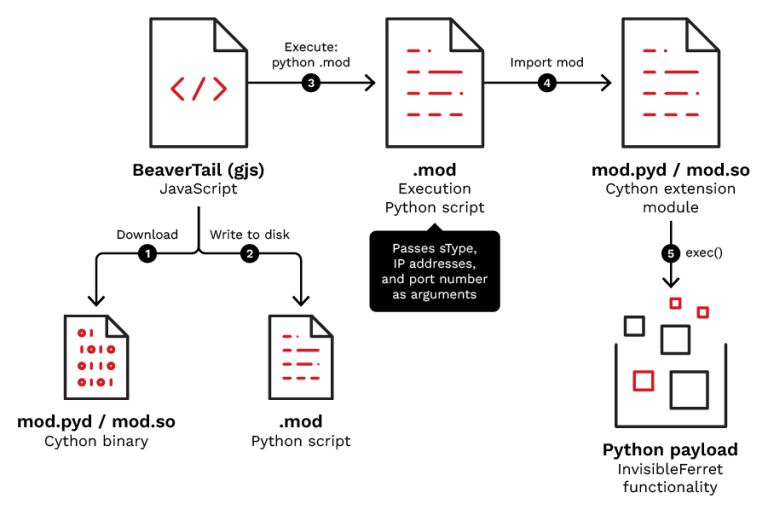
TrendAI Research exposes the new Void Dokkaebi Cython malware campaign. Learn how InvisibleFerret uses binary compilation to evade security teams.

ReversingLabs uncovers PromptMink: A DPRK campaign using LLM-generated npm packages to trick AI coding agents into installing crypto-stealing malware.
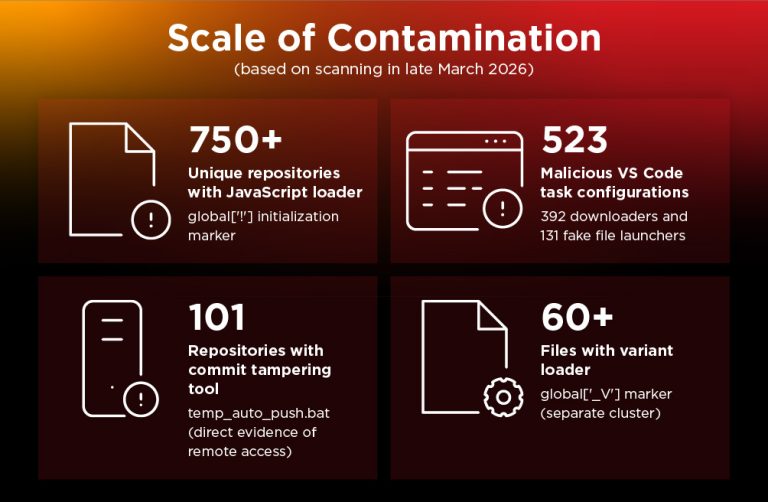
Void Dokkaebi turns developers into vectors. With 750+ infected repos and malicious VS Code tasks, this supply chain worm is hunting your CI/CD and crypto.

Panther uncovers "OtterCookie," a North Korean npm campaign hiding malware in benign wrappers. It steals crypto wallets and installs SSH backdoors. Audit now!

Socket uncovers "StegaBin," a North Korean malware campaign hiding C2 URLs in Pastebin essays to steal developer secrets via 26 typosquatted npm packages.
Cisco Talos exposed Famous Chollima using fake job offers and a trojanized Node.js app (Chessfi) to infect developers. The OtterCookie RAT steals crypto wallets, credentials, and source code.

GitLab Threat Intelligence reveals a new North Korean malware campaign using "ClickFix" social engineering to target new industries like crypto and retail.

North Korean APT Famous Chollima (Wagemole) is using a new Python-based RAT, PylangGhost, in fake job interviews to target crypto professionals and steal credentials.