
 Do Son
Understand the implications of CVE-2025-0475 & CVE-2025-0555. GitLab warns of severe vulnerabilities requiring immediate action.
gitlab

GitLab security update: Addressing multiple vulnerabilities, including the high severity cross-site scripting flaw (CVE-2025-0314). Stay protected!

Stay informed about the latest GitLab security update. Learn about the patch addressing vulnerabilities and the key changes to import functionality.

Stay protected with the latest GitLab security update. Learn about the vulnerabilities it addresses, including CVE-2024-11274 and CVE-2024-8233.
Protect your GitLab installations from critical vulnerabilities. Upgrade to the latest version to mitigate the risks of CVE-2024-8114 and other security issues.

Learn about the critical security update from GitLab addressing a high-severity vulnerability in Kubernetes clusters (CVE-2024-9693).

Sysdig TRT uncovers EMERALDWHALE: a large-scale cyber operation stealing cloud credentials by exploiting exposed Git configuration files.

Stay secure with GitLab's latest security updates. Learn about crucial patches that address flaws, including the critical CVE-2024-9164.

Understand the impact of the CVE-2024-45409 vulnerability that allows bypassing SAML authentication and gaining unauthorized access.

Stay informed about the urgent GitLab vulnerability update. Learn how to address the critical CVE-2024-45409 flaw that exposes instances to potential security breaches.

Don't miss the latest security advisory from GitLab. Learn about the critical flaws, including CVE-2024-6678, and secure your GitLab instance

GitLab, the widely-used code collaboration platform, released a security update today that addresses a half-dozen vulnerabilities

GitLab is in discussions with investment bankers regarding a potential sale, attracting interest from industry peers like Datadog

CVE-2024-6385 enables attackers to impersonate other users and run arbitrary pipeline jobs, posing a significant risk
CVE-2024-5655 allows attackers to trigger pipelines as another user under specific conditions, posing a significant security risk
The most severe vulnerability, CVE-2024-4835 (CVSS 8.0), involves a cross-site scripting (XSS) flaw in the code editor on gitlab.com

CVE-2024-4024: an attacker with stolen Bitbucket credentials could potentially take over a GitLab account linked to another user's Bitbucket account
CVE-2023-6371: "High" Severity XSS in Wiki Pages: This vulnerability could allow an attacker to inject malicious code into Wiki pages
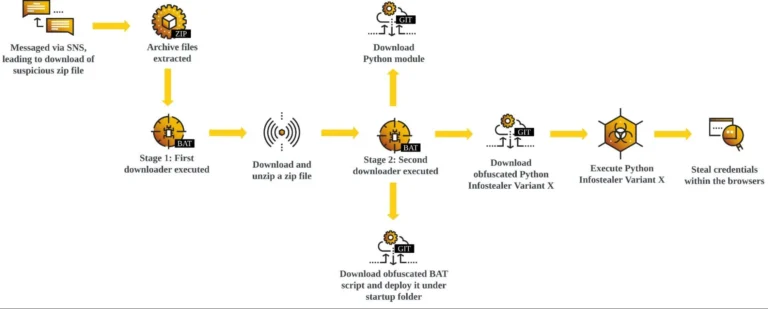
Attackers are becoming increasingly adept at weaponizing trusted resources and services, as seen in a recent Python-based infostealer campaign
The bug (tracked as CVE-2024-0402, CVSS 9.9) affects both GitLab Community Edition (CE) and Enterprise Edition (EE).

GitLab has taken decisive steps to fortify its defenses against two critical flaws - CVE-2023-7028 (CVSS 10) & CVE-2023-5356 (CVSS 9.6)

Vitellozzo, a security expert from the cybersecurity firm Occamsec, has released a PoC detailing how the CVE-2023-2825 flaw can be exploited