 Do Son
Group-IB exposes CyberDakait Android malware. The Indian CyberDakait Android malware campaign uses 7 trojans to infect 17,960 phones and steal 7.6M SMS.
Group-IB
Group-IB analyzes over 280 samples of SiriusQT RAT. Discover how the Windows SiriusQT RAT uses HVNC, six persistence methods, and 100+ stealer targets.
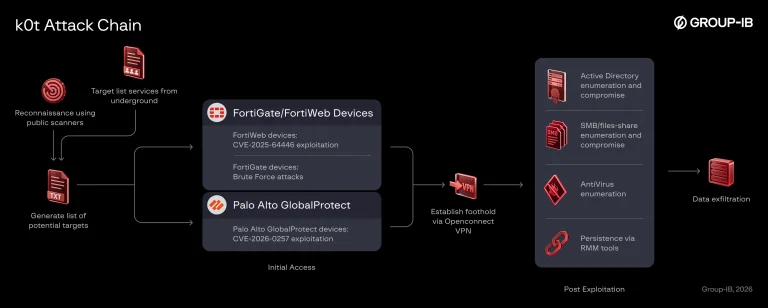
A suspected initial access broker behind FortiGate GlobalProtect attacks exposed 70,000+ credentials. See how k0t operates and how to defend.
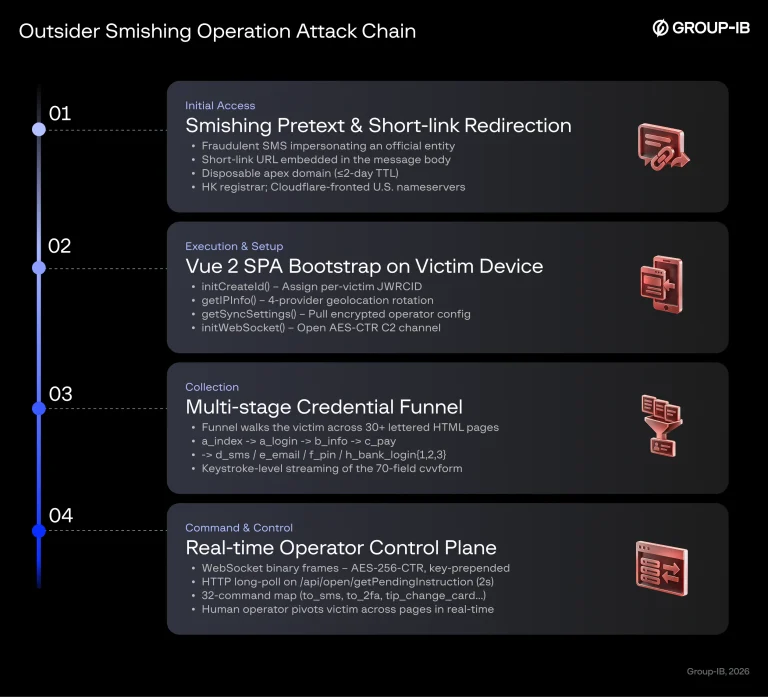
Group-IB exposed a new Smishing Triad phishing kit used by Outsider. Learn how this Smishing Triad phishing kit steals financial data worldwide.
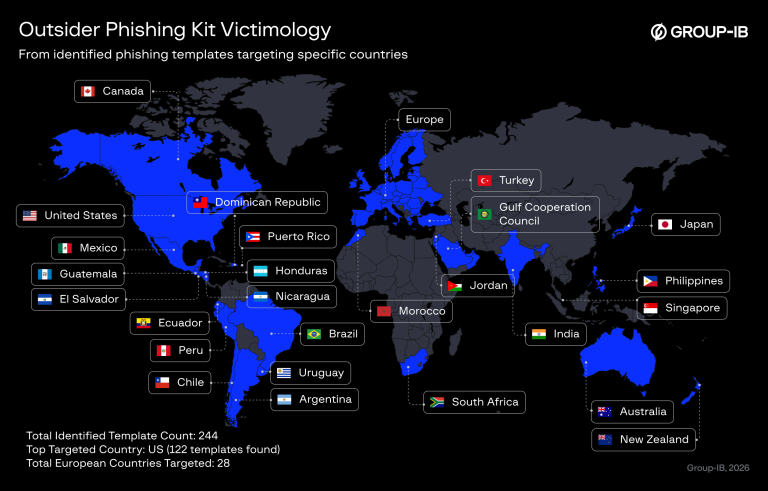
The Outsider Phishing Kit persists despite the Operation Ghost Hook takedown. Discover how the ChenLun Outsider PhaaS kit bypasses MFA via AiTM attacks.
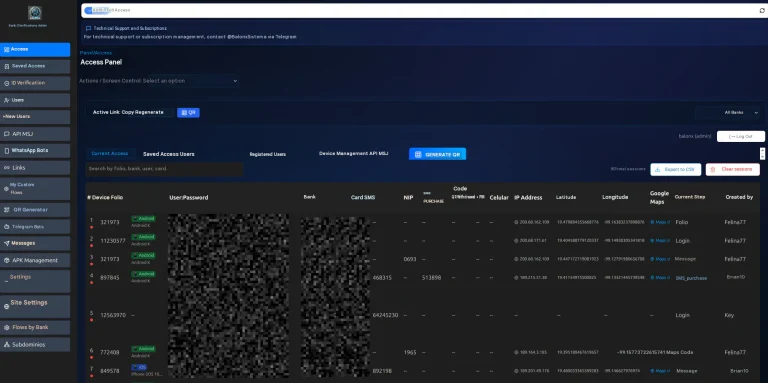
Group-IB exposed Balonx Sistema, a Mexican PhaaS platform bundling real-time phishing, an Android RAT, and AI-driven vishing against 20+ banks.

Group-IB uncovered XMRig Linux PAM abuse that lets a fileless Monero miner regenerate across user accounts and vanish from disk forensics.
Group-IB found an exposed server that revealed JadeProx, a China-nexus cluster running TriBack Loader against targets in Vietnam, Malaysia and Hong Kong.

ClickLock Stealer is macOS malware that freezes your Mac until you type your password. Group-IB found 100+ victims across 33 countries.
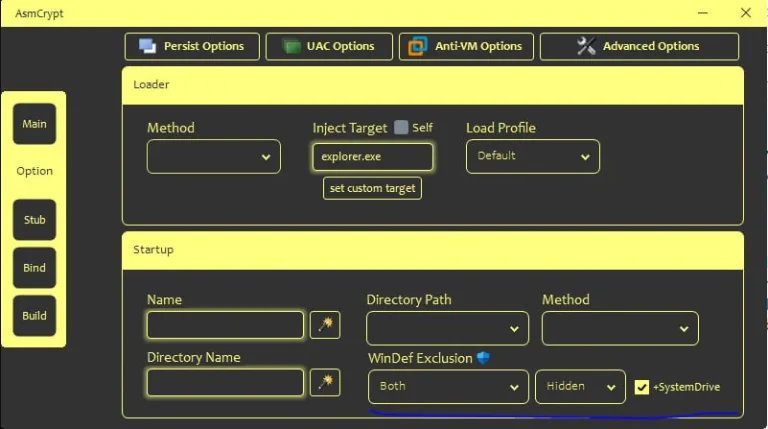
SilabRAT malware, aka SnappyClient, is a $5K/month MaaS RAT flagged as HijackLoader. It uses HVNC and cracks crypto wallets, per Group-IB.

Read the Group-IB phishing report detailing the massive Smishing Error524 campaign targeting millions across 72 countries with advanced evasion tactics.

Group-IB unmasks the Phoenix System: a PhaaS platform using rogue cell towers and live-dashboards to bypass MFA across 2,500+ domains. Read the full report.
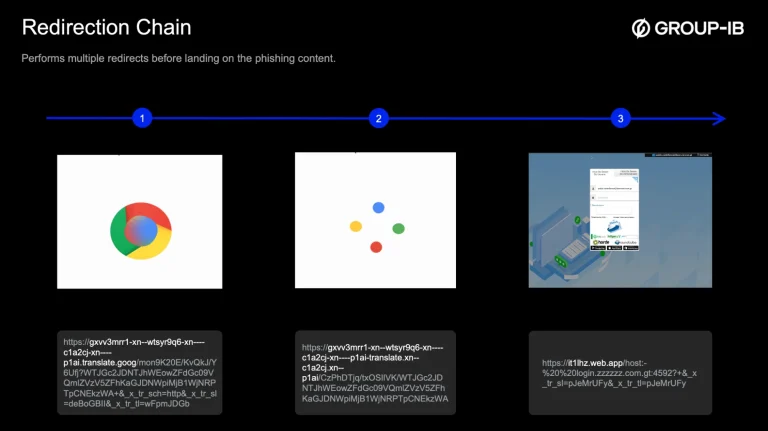
Group-IB uncovers "GTFire," a massive credential-harvesting operation abusing Google Firebase and Translate to bypass security filters in 100+ countries.

Group-IB exposes Operation Olalampo: MuddyWater's new MENA campaign using AI-assisted Rust malware (CHAR) and Telegram bots for stealthy C2 communication.

Group-IB exposes an industrialized mobile banking fraud campaign in Indonesia. GoldFactory hackers use fake Coretax apps and Gigabud.RAT to drain accounts.
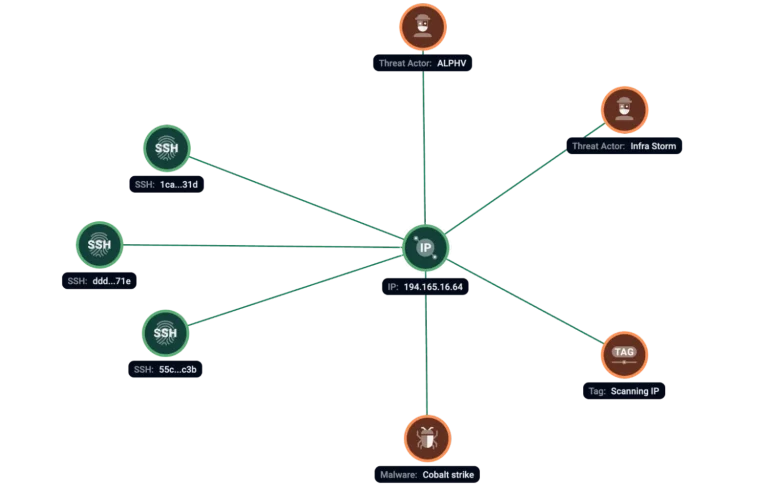
Group-IB reveals ShadowSyndicate is evolving. The cybercrime cluster now rotates SSH keys to hide its infrastructure. Is it a BPH or IAB?

Group-IB reveals a sophisticated loan phishing campaign in Peru. Scammers use the Luhn algorithm to validate stolen credit cards via fake ads.

Group-IB uncovers DeadLock ransomware using Polygon smart contracts for resilient C2. This "EtherHiding" tactic signals a new era of blockchain abuse.

New "Ghost Tap" malware lets hackers relay NFC signals from your Android phone to steal funds remotely. Learn how this sophisticated Group-IB discovery works.

Group-IB uncovers "Wonderland," a bidirectional Android SMS stealer in Uzbekistan that uses Telegram droppers to drain bank accounts and hijack sessions.
Group-IB reports on MuddyWater, an Iranian APT, shifting tactics from RMM tools to custom malware and spearphishing, using new backdoors like Phoenix.
A new Group-IB report reveals ShadowSilk, a hybrid Chinese and Russian-speaking threat cluster that uses Telegram bots for cyber espionage against Central Asian governments.