
 Do Son
Hackers target Rockstar Games via Snowflake. While Rockstar calls the data "non-substantial," could internal budgets and future launch dates be at risk?
Hacking

A new technique, "EDR-Freeze," uses a built-in Windows feature to suspend antivirus and EDR processes, giving attackers a critical window to operate undetected.

The DOJ has charged Thalha Jubair, a UK national, for his role in the notorious Scattered Spider group's $115M cybercrime and extortion campaign.

Microsoft’s DCU has seized 338 websites to disrupt RaccoonO365, a growing phishing service used to steal Microsoft 365 credentials from 94 countries.

A new report reveals Chinese threat actor TA415 is targeting U.S. policy organizations with sophisticated spearphishing campaigns to gather intelligence.
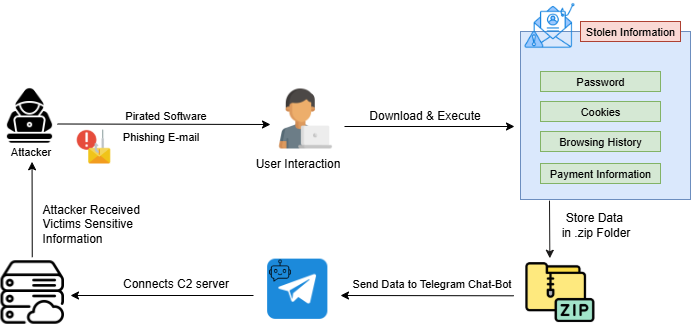
A new malware called Raven Stealer is emerging, targeting individuals and businesses by stealing credentials and data, and exfiltrating it via Telegram.

The founder of BreachForums, Conor Fitzpatrick, has been resentenced to three years in prison after his initial lenient sentence was overturned by a U.S. appeals court.

Researchers expose BaoLoader, a malware operation that has systematically used at least 26 code-signing certificates over seven years to appear legitimate and bypass security.

Trend Micro reveals a new global malware campaign, EvilAI, that impersonates productivity and AI tools to infiltrate organizations and steal data.

A superseding indictment unsealed by the DOJ reveals a Ukrainian national's role as an administrator in three major ransomware operations.

Plex has confirmed a data breach that exposed user data, including hashed passwords. All users are being urged to reset their passwords as a security precaution.

A new report reveals the AMOS infostealer is targeting macOS. The malware is spread via fake apps and malicious Terminal commands that bypass Gatekeeper.

A new report from Sekoia.io reveals how the global commercial spyware industry is thriving despite sanctions, selling sophisticated zero-click surveillance tools to governments.

A new RAT, disguised as an AI assistant, is using social engineering to infiltrate a role-playing community. The malware provides attackers with full remote control over infected PCs.
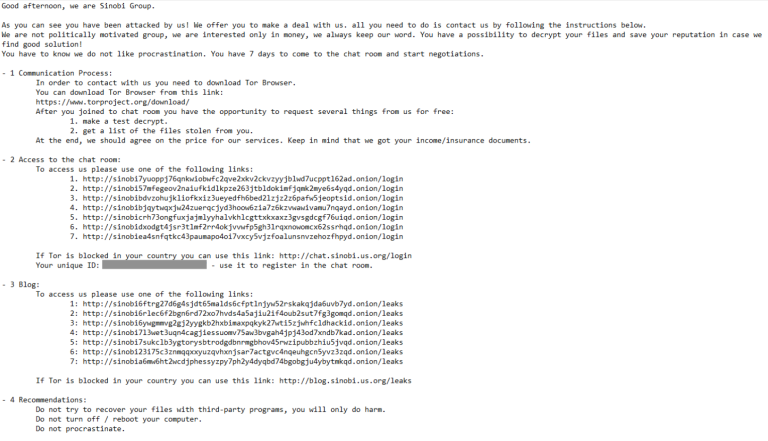
A new report links Sinobi Group ransomware to Lynx, a potential rebrand. The group is using strong encryption and targeting compromised SonicWall VPN credentials to gain access.
A new Anthropic report reveals how criminals are weaponizing AI systems to automate attacks, create AI-generated ransomware, and secure fraudulent employment.

A new Microsoft report reveals that the Storm-0501 threat actor is pivoting to cloud-native ransomware, using cloud tools to exfiltrate and destroy data without malware.

A new campaign is using fake AI-themed content to trick users into downloading a malicious ScreenConnect installer that secretly delivers the XWorm Remote Access Trojan.

A new report from AhnLab reveals the Underground ransomware gang is back with a global campaign that uses sophisticated multi-layered encryption and customized malware.

GreyNoise reports a massive, coordinated scanning campaign targeting Microsoft RDP services. Attackers are probing tens of thousands of IPs to prepare for future attacks.

A critical zero-day vulnerability (CVE-2025-5419) in Chrome's V8 engine is being actively exploited. Users must update their browser immediately to prevent attacks.

Following a breach tied to an insider, Coinbase is restricting remote work and requiring U.S. citizenship for key roles to combat infiltration by North Korean hackers.