
 Do Son
Elastic Security Labs found TELEPUZ malware spreading via a ClickFix attack chain. The modular MaaS uses WebSockets and blockchain C2 fallback.
Infostealer

ClickLock Stealer is macOS malware that freezes your Mac until you type your password. Group-IB found 100+ victims across 33 countries.

CrashStealer is a native C++ macOS infostealer posing as Apple's crash reporter. Jamf details its notarized dropper, AES-GCM theft, and persistence.
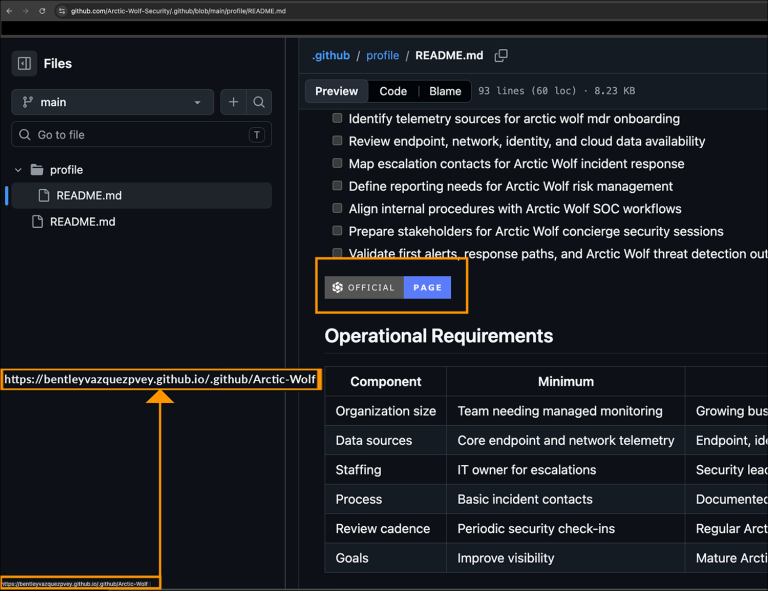
Arctic Wolf found 292 fake GitHub repositories impersonating software vendors to deliver a BoryptGrab-lineage infostealer via DLL side-loading.
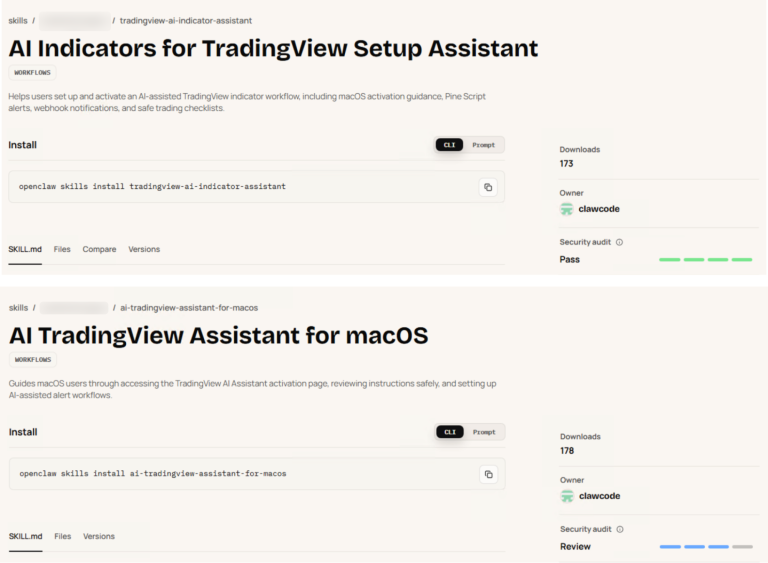
Unit 42 found five malicious OpenClaw skills on ClawHub that bypassed scanners. The AI supply chain attack delivered infostealers and crypto fraud.

The OXLOADER malware loader spreads via malicious Google Ads, dropping the CASTLESTEALER infostealer with heavy obfuscation and anti-VM checks.
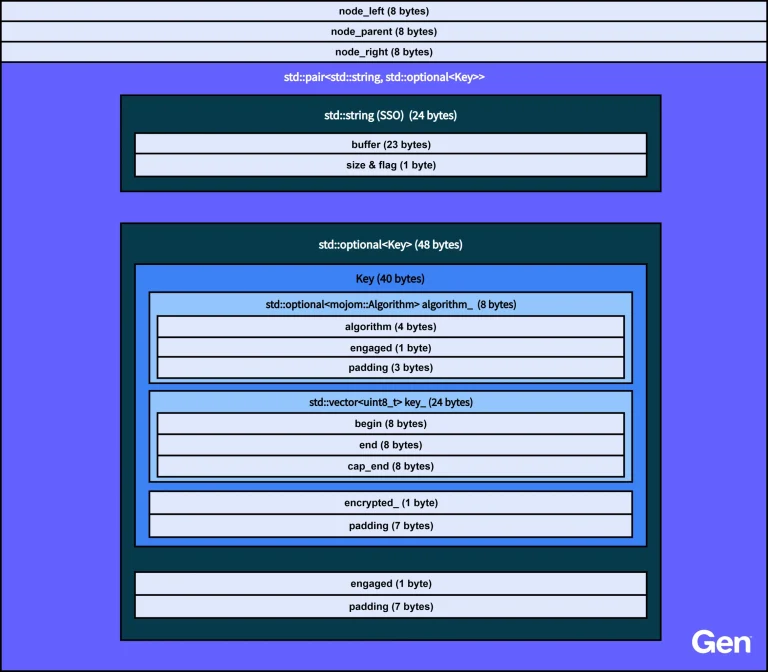
Gen Digital uncovered a new Vidar ABE bypass technique. The Vidar infostealer malware now uses memory scanning and APC injections to extract browser keys.
Trend Micro tracked a ClickFix malvertising campaign that abused claude.ai shared chat to deliver the MacSync infostealer to Mac developers.

GoFlateLoader malware, a Golang loader, uses a giant PE overlay to evade scanners and deliver infostealers like Lumma, Vidar, and StealC.
A Mastra supply chain attack compromised 140+ npm packages, using the typosquatted easy-day-js dependency to drop a crypto-stealing infostealer.
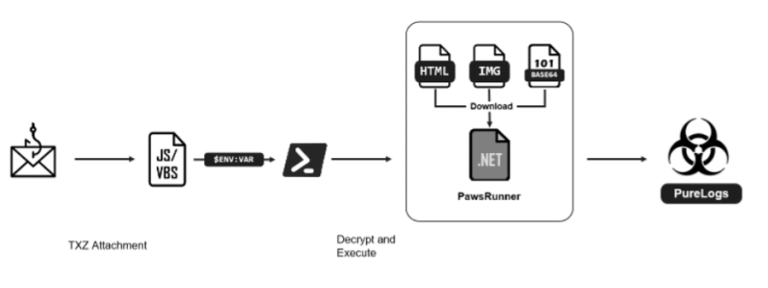
FortiGuard Labs warns of PawsRunner, a new .NET steganography loader hiding PureLogs infostealer payloads inside cat images to bypass corporate EDR.
Unit 42 exposes the new Gremlin stealer. It uses memory-resident techniques to hijack active browser session tokens and completely bypass MFA.
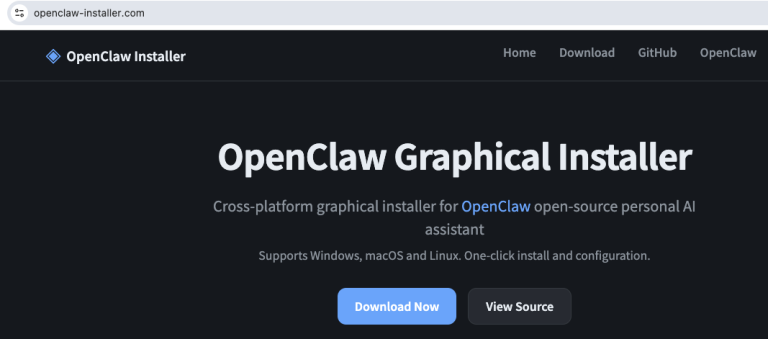
Netskope exposes Hologram: a red-team-grade malware framework targeting OpenClaw AI users with CLR injection and WinLogon hijacking to steal crypto wallets.
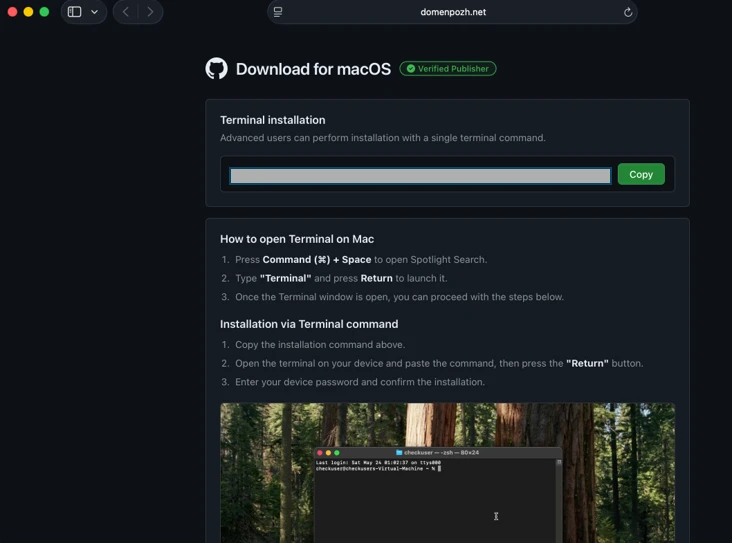
Microsoft reveals a macOS ClickFix campaign using fake "fixes" to trick users into running Terminal commands that bypass Gatekeeper and steal crypto wallets.
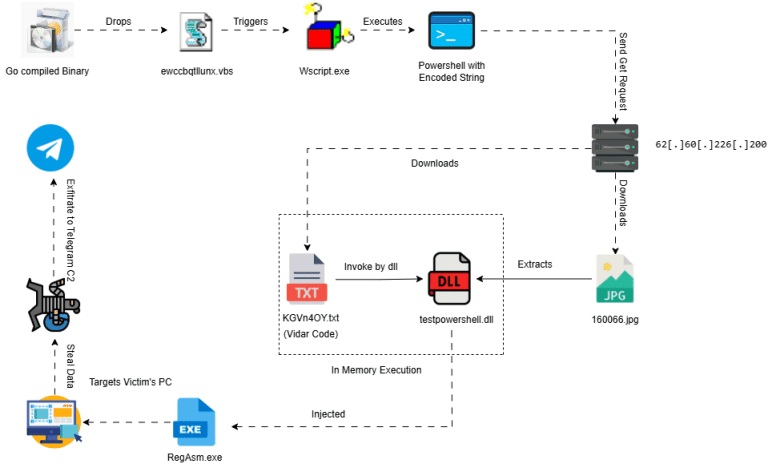
Vidar infostealer evolves into a fileless 2026 threat. From fake CAPTCHAs to "Claude Code" leaks, see how it steals crypto and passwords via Telegram C2.
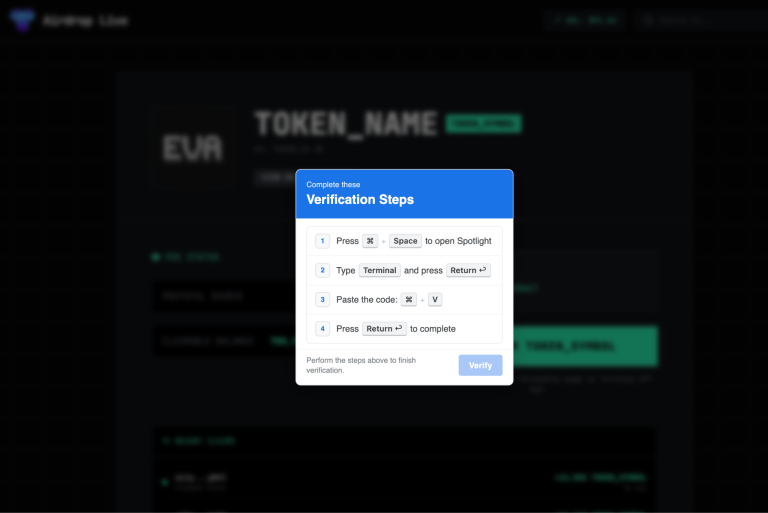
Netskope uncovers a ClickFix macOS campaign that holds the UI hostage to steal system passwords, Keychains, and 200+ browser extensions.
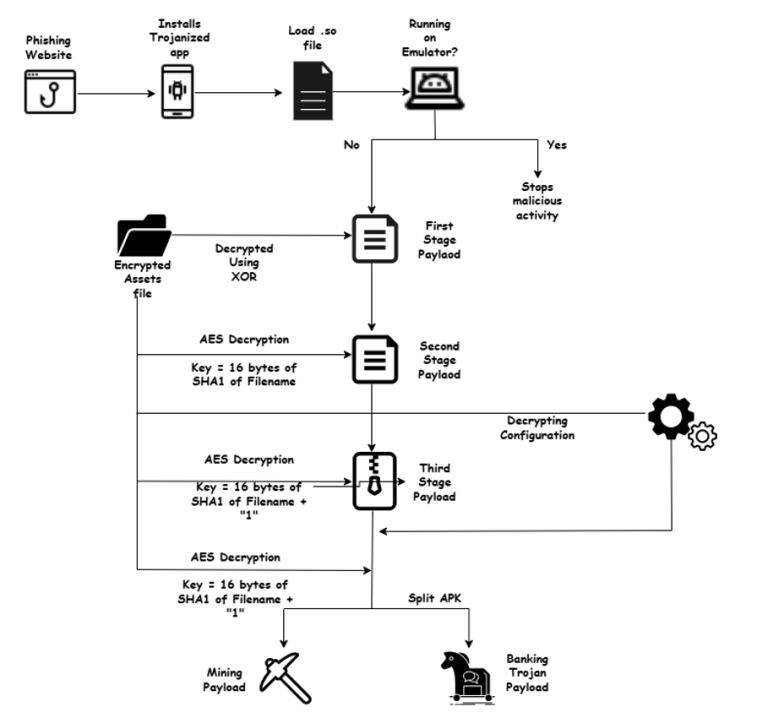
Cyble reveals MiningDropper, a modular Android threat delivering RATs and infostealers via multi-stage payloads. Protect your mobile devices now.

Panther uncovers "OtterCookie," a North Korean npm campaign hiding malware in benign wrappers. It steals crypto wallets and installs SSH backdoors. Audit now!

Jamf identifies a macOS ClickFix pivot: attackers now use the Script Editor to bypass Terminal scans and deliver Atomic Stealer. Learn how to stay protected.
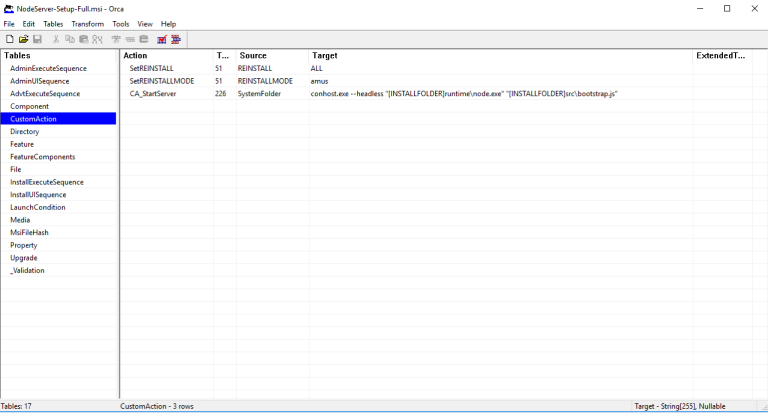
Netskope uncovers a Node.js-based ClickFix campaign using gRPC over Tor for stealthy crypto theft. A leaked file exposed their entire MaaS backend.
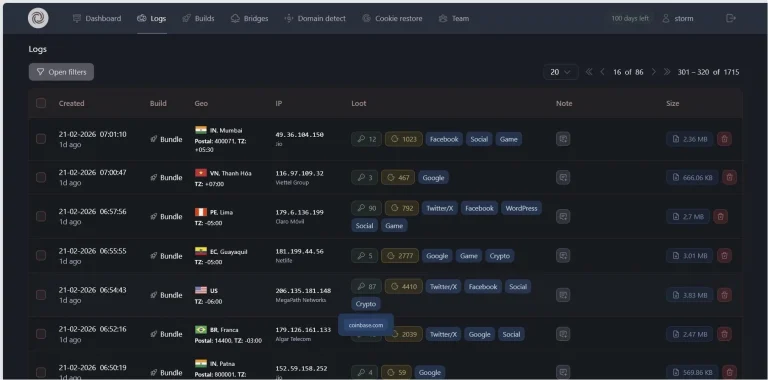
Storm malware bypasses Chrome security by shipping encrypted files for server-side decryption. Learn how it steals session cookies to defeat MFA in 2026.
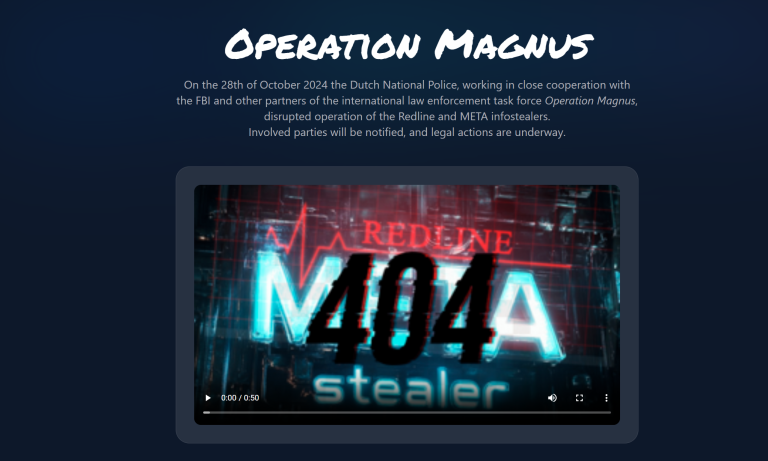
RedLine architect Hambardzum Minasyan is extradited to the U.S. to face 50 years in prison for his role in the global malware empire and Operation Magnus.