
 Do Son
Gen Threat Labs uncovers VoidStealer, the first malware using a debugger-based bypass to extract Chrome and Edge encryption keys via hardware breakpoints.
Infostealer

Beware of "MacSync Stealer": A new macOS malware campaign using SEO poisoning and terminal commands to hijack crypto wallets and system keys.
Bitdefender uncovers a malicious Windsurf IDE extension using the Solana blockchain as an unblockable C2 to steal developer credentials and source code.

Acronis uncovers a massive campaign targeting gamers with fake cheats to deliver Vidar Stealer 2.0, a highly evasive malware stealing crypto and passwords.

Rapid7 exposes a global ClickFix campaign hijacking WordPress sites with fake Cloudflare CAPTCHAs to deliver stealthy infostealers and drain digital wallets.

Trend Micro reveals the BoryptGrab info stealer campaign using SEO-optimized fake GitHub repos to deploy the TunnesshClient reverse SSH backdoor.

Following the Lumma takedown, the sophisticated AuraStealer malware is rapidly gaining ground, using TikTok scams and stealth to harvest data.

G DATA reveals how pirated gaming site PiviGames distributes ACRStealer via "spaghetti code" HijackLoader and DLL sideloading, causing total account takeovers.
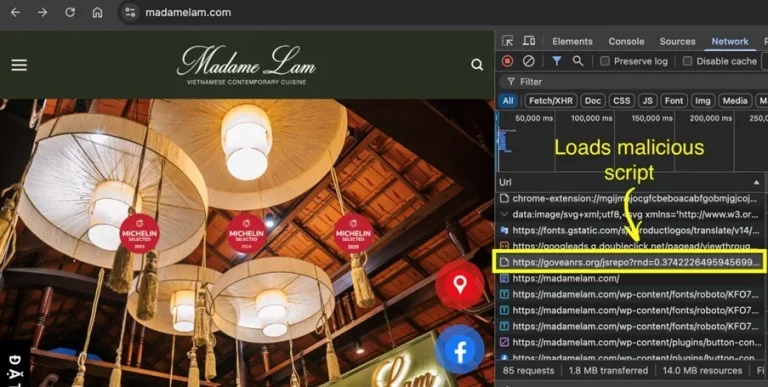
LevelBlue warns of StealC malware using "ClickFix" fake CAPTCHAs. Users are tricked into running fileless malware via PowerShell. Stay alert.

LummaStealer is back, evading takedowns with "ClickFix" tactics. Bitdefender reveals how fake CAPTCHAs trick users into running malware. Stay alert.

New LTX Stealer malware abuses Node.js & Inno Setup to bypass antivirus. This $10 tool steals browser passwords & crypto wallets. Stay alert.
Microsoft warns: Infostealers now target macOS & use WhatsApp worms. "Eternidade" & "Crystal PDF" steal credentials via cross-platform attacks.

GlassWorm malware found in Open VSX extensions. Hackers stole AWS & SSH keys from macOS devs using Solana C2. 22k+ downloads affected. Check your tools.
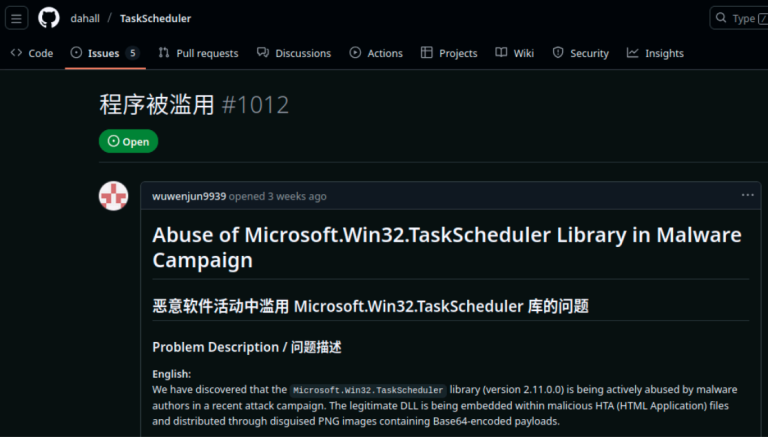
New "PhantomVAI" malware recycles old Hackforums "RunPE" code to bypass modern EDR. Campaigns use task scheduler masquerading to deliver infostealers.
Malicious npm package "ansi-universal-ui" drops "G_Wagon" infostealer to steal cloud keys and wallets. Check for .gwagon_status and rotate creds now.

New macOS malware "MacSync" uses fake cloud installers & "ClickFix" terminal commands to steal crypto. It bypasses Gatekeeper to trojanize wallet apps.

New PURELOGS campaign uses Archive.org images to hide malware. For just $150, this MaaS steals crypto & passwords via fileless attacks. Spot the signs.
Trend Micro reveals Evelyn Stealer, a malware campaign weaponizing Visual Studio Code extensions. It uses DLL injection to steal developer secrets & crypto.

CYFIRMA reveals SolyxImmortal, a Python info-stealer using Discord webhooks for C2. It logs keys and steals files while evading detection.

Sophos reveals "TamperedChef" malvertising. Fake "AppSuite PDF Editor" uses valid EV certs to deploy infostealers globally. Check your systems now.

New macOS malware "MonetaStealer" disguises itself as a Windows .exe to steal crypto & Keychain data. It currently has zero VirusTotal detection.

New malware campaign impersonates Malwarebytes installers. Hackers use DLL sideloading to deploy infostealers targeting crypto & MFA. Verify downloads now.