 Do Son
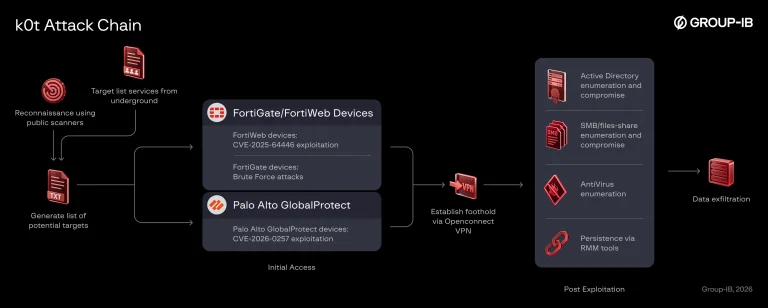
A suspected initial access broker behind FortiGate GlobalProtect attacks exposed 70,000+ credentials. See how k0t operates and how to defend.
initial access broker

A new GoGRPC backdoor spreads through Microsoft Teams vishing and Quick Assist. Zscaler links the campaign to a likely ransomware access broker.

Edgecution malware abuses a malicious Edge extension and native messaging to backdoor hosts. Zscaler links it to a Payouts King access broker.

The active DriveSurge threat cluster is compromising thousands of websites. Discover how its customized Traffic Distribution System redirects victims.

A Romanian hacker sentenced to prison following an identity theft conviction and selling access to a US government network infrastructure.

ReliaQuest warns Initial Access Broker "KongTuke" is abusing external Microsoft Teams chats to deploy the highly resilient ModeloRAT. Audit tenants now!
BlueVoyant unmasks "Lorem Ipsum": a well-funded campaign using SEO poisoning and signed MS Teams installers to deploy stealthy backdoors via image files.
Russian national Aleksei Volkov was sentenced to 81 months in prison and ordered to pay $9.1M for his role as an access broker in major U.S. ransomware attacks.

New campaign targets Ivanti EPMM with dormant in-memory backdoors. Attackers use CVE-2026-1281 to plant "sleeper" agents. Restart servers immediately.
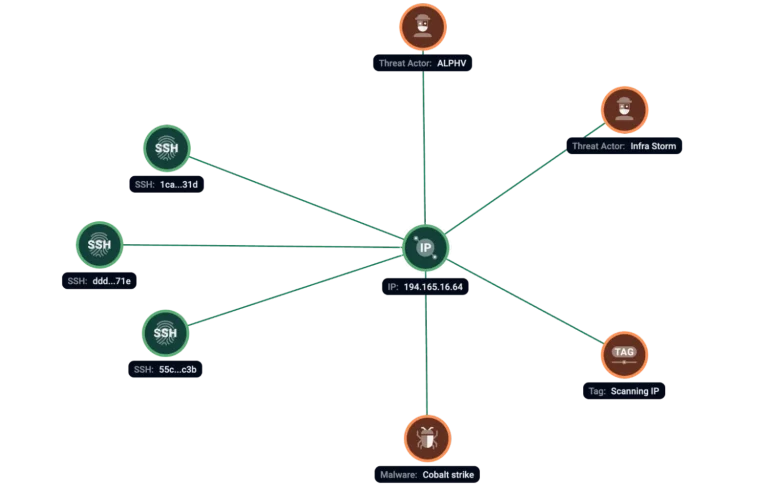
Group-IB reveals ShadowSyndicate is evolving. The cybercrime cluster now rotates SSH keys to hide its infrastructure. Is it a BPH or IAB?

TA584 triples activity with new "Tsundere Bot" malware. Attackers use invisible Registry keys to hide persistence. Read the Proofpoint analysis.

GreyNoise reveals a massive Japan-based holiday campaign: 2.5 million attacks targeting 767 CVEs to harvest access for ransomware gangs.

Storm-0249 IAB abuses the SentinelOne EDR process via DLL sideloading to evade detection. The group uses LoLBin tools for fileless execution and sells access to ransomware groups like LockBit.

Broadcom exposed a group deploying multiple RMM tools (ScreenConnect, LogMeIn, Naverisk) weeks apart to achieve redundant persistence. The likely Initial Access Broker (IAB) prepares systems for resale.

Silent Push exposes SocGholish as a MaaS platform for Initial Access Brokers. The malware, disguised as fake updates, fuels top-tier Russian ransomware groups like Evil Corp.

Unit 42 reveals "Gold Melody" uses leaked ASP.NET Machine Keys to achieve in-memory RCE via View State deserialization and privilege escalation via GodPotato, compromising web servers.

ANSSI exposes "Houken," a China-linked APT exploiting Ivanti CSA zero-days (CVE-2024-8190, CVE-2024-8963, CVE-2024-9380) and deploying Linux rootkits for cyber-espionage against strategic sectors.

Palo Alto Networks exposes CL-CRI-1014, an IAB targeting African financial institutions. They use open-source tools like PoshC2 and Classroom Spy, disguised with forged signatures for covert network access.

A trojanized KeePass installer is spreading malware! Learn how this sophisticated attack steals credentials and deploys Cobalt Strike.

Cisco Talos warns of a Brazil-focused spam campaign abusing legitimate remote access tools (N-able, PDQ) to gain full system control. Stay vigilant!

Cisco Talos uncovers ToyMaker's IAB activity, paving the way for Cactus ransomware. Learn how LAGTOY backdoor & credential theft led to a major breach.