
 Do Son
Learn about CVE-2025-2945, a critical vulnerability in pgAdmin 4 that can lead to remote code execution in your database environment.
javascript

Explore the dangers of SectopRAT malware, a sophisticated Remote Access Trojan known for its stealthy data exfiltration techniques.

Discover how CVE-2025-1914 impacts Google Chrome and the urgent security patches included in the latest Chrome 134 update.

Uncover the GitVenom campaign targeting GitHub users with malicious repositories designed to steal credentials and cryptocurrency.

Learn about browser fingerprinting and its dangers. Understand how attackers use this technique to evade security measures.

A report from Google Threat Intelligence Group has revealed a coordinated effort by multiple Russia-aligned threat actors to compromise Signal Messenger accounts

Discover the critical vulnerability in Subaru STARLINK connected vehicle service that allows remote tracking and control of vehicles.

Discover the new security measures implemented by Google for its search engine. Find out why enabling JavaScript is crucial for accessing Google Search.

Discover the Sneaky 2FA phishing kit, a sophisticated tool that bypasses MFA to exploit Microsoft 365 accounts. Stay informed about the latest threats.

Find out how the NodeStealer infostealer malware has evolved, expanding its capabilities and targeting Facebook Ads Manager accounts.

Uncover the FLUX#CONSOLE campaign and its stealthy backdoor. Learn how attackers are using tax-themed phishing emails to deploy a sophisticated phishing campaign.
Unveiling a new threat in the VSCode Marketplace: a malicious campaign targeting cryptocurrency users and impersonating popular applications like Zoom.
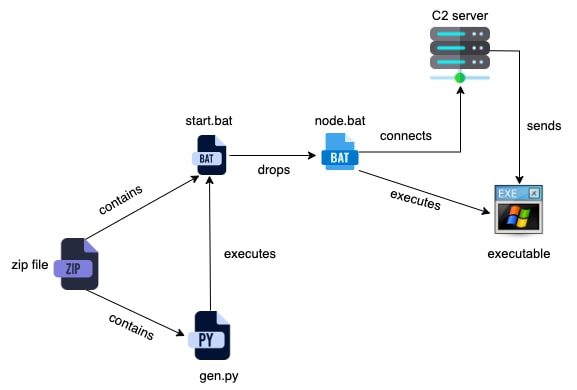
Unveiling the inner workings of Celestial Stealer: a powerful infostealer disguised as legitimate applications, targeting developers, gamers, and cryptocurrency users.
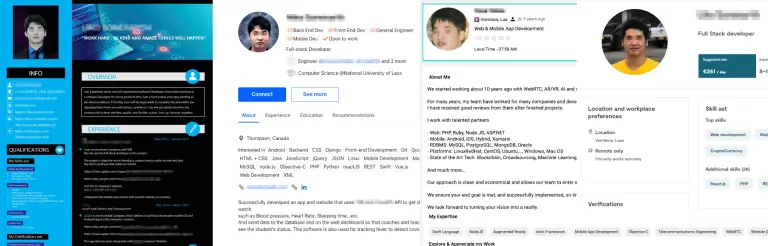
Explore the complex phishing campaign led by North Korean IT workers CL-STA-0237. Learn how they targeted job seekers with malware-infected video conference apps.

Introducing CSP Bypass, the open-source tool for ethical hackers and security researchers to identify and bypass Content Security Policies (CSPs) and exploit XSS vulnerabilities.
Learn about the use-after-free flaw (CVE-2024-28888) in Foxit Reader. Find out how attackers can exploit this flaw to execute arbitrary code.

An analysis detailing the advanced evasion techniques employed by GootLoader, a pervasive malware known for its role in delivering ransomware

BitRAT is a powerful remote access tool that grants attackers extensive control over infected systems, enabling them to steal sensitive data

The vulnerability, designated CVE-2024-34710, poses a serious risk due to its potential for stored cross-site scripting (XSS) attacks

CVE-2024-34346 (CVSS 8.5) presents a significant risk as it allows for permission escalation through the mishandling of privileged files

The subsequent investigation unveiled a sophisticated RAT deployment masquerading as a standard Microsoft update process.
Sean Larkin, a Microsoft Technology Project Manager (TPM), revealed on Twitter that Office 365 is being rewritten with JavaScript. Office 365 is...