 Do Son
Body-parser vulnerability CVE-2026-111181 (CVSS 7.5) enables Express denial of service with one request. Upgrade to body-parser 2.4.0 or 1.20.9.
javascript
Storybook dev server vulnerability CVE-2026-114125 (CVSS 9.4) enables code injection from malicious websites. Upgrade to 10.6.2, 9.1.21 or 8.6.19.
Two Handlebars.js vulnerability disclosures (CVE-2026-106445, CVE-2026-106446) enable RCE. Details and PoC are public. Update to 4.7.10 now.
Five high-severity Electron vulnerabilities, including CVE-2026-102676, CVE-2026-102673 and CVE-2026-102674, weaken sandbox isolation. Update Electron now.

A Vitest vulnerability rated CVSS 9.4 lets Browser Mode commands bypass the file-access gate. The npm package sees 65M weekly downloads.

Protect your app from CVE-2026-23870. Learn how this high-severity React Server Components DoS flaw crashes servers and how to patch your React 19 build today.

Angular patches a critical 8.7 SSRF flaw in @angular/platform-server. Attackers can hijack SSR origins via URL normalization. Patch v19, v20, or v21 now!

A critical CVSS 10 flaw in Axios (CVE-2026-40175) allows attackers to bypass AWS IMDSv2 and achieve RCE via header injection. Upgrade to v1.15.0 now!
Vite patches critical flaws (CVE-2026-39364 & CVE-2026-39363) allowing arbitrary file reads and .env leaks via WebSockets and query params. Upgrade to 8.0.5!
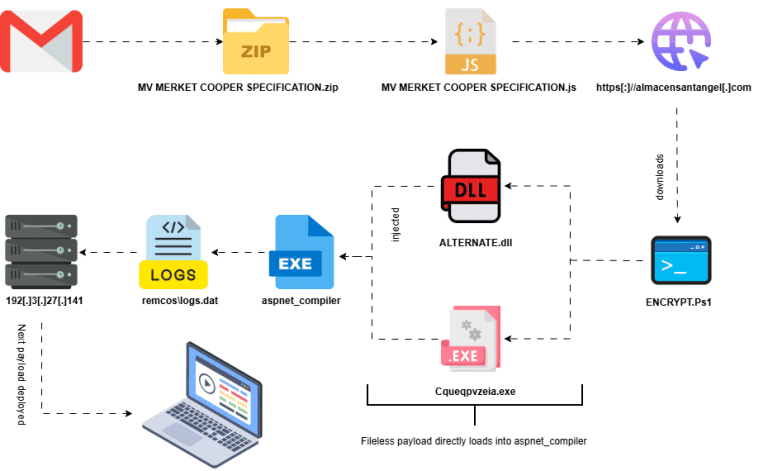
Researchers unmask a fileless Remcos RAT campaign using obfuscated JS and LOLBins to hijack systems in-memory. See the technical breakdown from Lat61.

Lodash (CVE-2026-4800) faces an 8.1 CVSS code injection flaw in the _.template function. Attackers can bypass validation via imports. Update to 4.18.0 now!
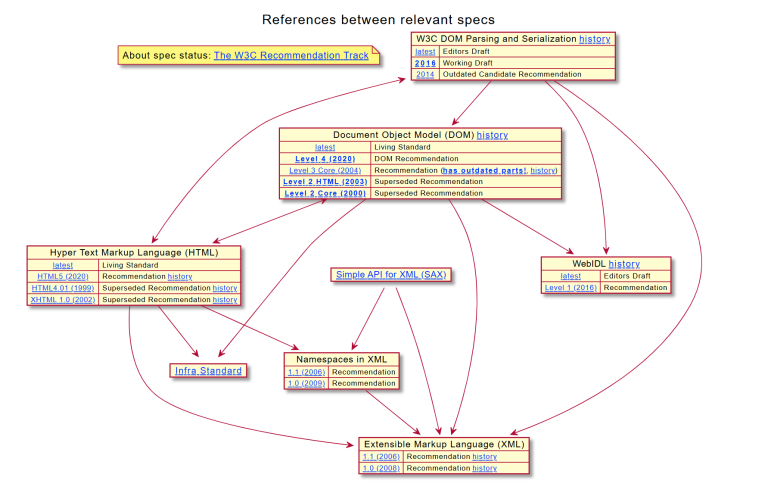
Fix CVE-2026-34601 in @xmldom/xmldom (CVSS 7.5). A CDATA injection flaw allows attackers to bypass "safe zones" and manipulate business logic. Update now!

Axios versions 1.14.1 & 0.30.4 have been poisoned. A hijacked maintainer account is dropping a RAT via postinstall scripts. Revert to safe versions now!
Node-convict (CVE-2026-33864) faces a 9.4 CVSS Prototype Pollution flaw. Bypass filters and hijack Node.js apps. Update to version 6.2.5 now to stay secure.
Lazarus Group targets crypto developers with fake job offers in new "Graphalgo" campaign. Malicious npm packages deliver multi-stage malware. Stay alert.

Urgent: Node.js patches CVE-2025-55131 (High Severity). "Dirty" memory flaw exposes secrets. Update to v20.20.0/v22.22.0 now to stop data leaks.
Angular CVE-2026-22610 (CVSS 8.5) allows XSS via SVG script attributes. Update to v21.0.7 or v20.3.16 immediately to secure your apps.

A normalization flaw in Better Auth's router allows attackers to bypass access controls and rate limits using simple double-slash URLs.

Google released an urgent Chrome update to patch High-severity flaws in WebGPU and V8. Fixes include a Use-After-Free and Memory Corruption. Update to v143.0.7499.146+ now.

CVE-2025-66035: Angular protocol-relative URLs leak XSRF tokens, bypassing CSRF protection. Update to v19.2.16, v20.3.14, or v21.0.1 now.

A new malicious npm package, "fezbox," hides a credential-stealing payload within a QR code, which it uses to exfiltrate web cookies and credentials.

A key npm maintainer's account was compromised, leading to a supply chain attack. Malicious code in popular packages is stealing crypto during transactions.