
 Do Son
A critical flaw in the widely used sha.js library (CVE-2025-9288) can lead to hash collisions and private key extraction, threatening web applications.
javascript

Google has released an urgent update for Chrome, patching a high-severity, out-of-bounds write vulnerability in the V8 JavaScript engine. Update your browser now.

Unit 42 uncovers DarkCloud Stealer's new evasion tactics, including heavily obfuscated JavaScript/WSF loaders and a final VB6 payload that injects into RegAsm.exe to bypass detection.

A critical flaw (CVE-2025-54782, CVSS 9.4) in NestJS's devtools-integration package allows attackers to execute code on a developer's machine via a malicious website.

A phishing attack compromised the 'is' npm library maintainer, leading to malicious versions being published with backdoors for remote code execution. Update immediately!

Socket discovered 10 malicious npm packages from Toptal's GitHub, exfiltrating GitHub tokens and wiping systems. The compromise vector is under investigation.

A critical flaw (CVE-2025-54371, CVSS 7.5) in the form-data package, used by Axios 1.10.0, allows attackers to predict multipart boundaries, risking HTTP parameter pollution and injection. Update to 1.11.0 now!

A critical vulnerability (CVE-2025-7783, CVSS 9.4) in the Form-Data JavaScript library allows multipart injection and potential RCE due to predictable boundary values.

Socket researchers uncovered widespread "protestware" in 28+ npm packages, silently disabling mouse interactions and playing the Ukrainian anthem for Russian-language users.

Google's Advanced Protection Program now offers device-level security for Android, bringing HTTPS-Only Mode, full Site Isolation, and disabled JS optimizers to Chrome for high-risk users.

Two critical flaws (CVE-2025-6545, CVE-2025-6547, CVSS 9.1) in pbkdf2 npm package allow silent compromise of cryptographic keys. Update to 3.1.3+ immediately!

Socket discovers 4 malicious npm packages designed to drain crypto wallets on BSC & Ethereum, downloaded over 2,100 times.

Malicious npm packages have been silently destroying files and corrupting data in React, Vue.js, and Vite projects for over two years.

A reflected XSS flaw in GlobalProtect (CVE-2025-0133) allows malicious JavaScript execution. PoC exploit code is available. Update your PAN-OS.

A technical analysis of the More_Eggs malware, detailing its use of ieuinit.exe abuse, DLL side-loading, and polymorphic JavaScript.

Aikido discovers a Remote Access Trojan (RAT) hidden in rand-user-agent, a popular npm package with 45,000 weekly downloads.

Critical security vulnerability (CVE-2025-4318) in AWS Amplify Studio allows arbitrary code execution. Upgrade to version 2.20.3 immediately!

CVE-2025-47154 (CVSS 9.0) is a use-after-free flaw in the Ladybird browser engine that attackers can exploit. Update to the fixed build now.

Phishing attacks are evolving! Cybercriminals now embed HTML in SVG files to bypass detection. Learn how SVG phishing works and how to stay safe.

Yarix uncovers a sophisticated Magecart attack using obfuscated JavaScript to steal credit card data from an e-commerce site, highlighting evolving web skimming tactics.
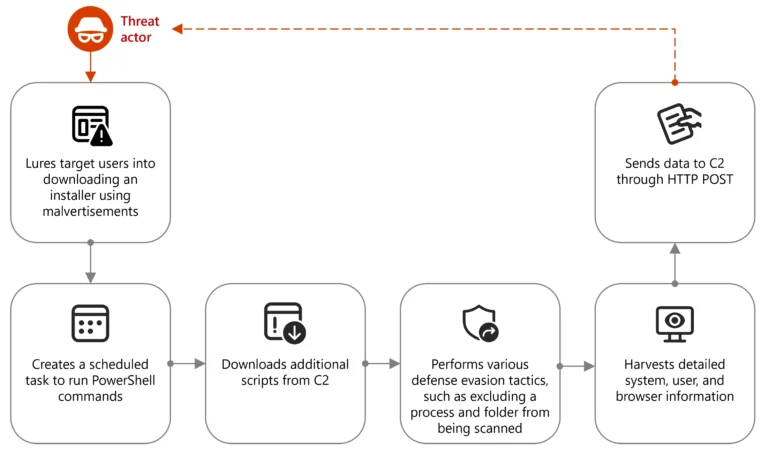
Threat actors abuse Node.js in malvertising campaigns to steal data and deliver malware via fake crypto installers and stealthy PowerShell scripts.

FortiGuard Labs discovers malicious NPM packages targeting PayPal users. Attackers use deceptive tactics to steal usernames, paths, and hostnames