 Do Son
Patch CVE-2026-110720 now. This 9.9 CVSS consul-k8s vulnerability enables a cross-namespace authorization bypass in ACL binding rules.
Kubernetes
Six Apache DolphinScheduler vulnerabilities, including CVE-2026-71896 and Kubernetes credential leak CVE-2026-71895, are fixed in 3.4.3.
Four critical Argo CD vulnerabilities, including AppProject bypass CVE-2026-77459, threaten the repo-server and clusters. Upgrade to v3.5.4 now.
Dell Container Storage Modules vulnerabilities CVE-2026-63688 and CVE-2026-63692 (CVSS 10) allow admin takeover. Upgrade to 1.18.0.
A critical Hawtio Operator vulnerability, tracked as CVE-2026-78234, allows in-cluster service impersonation. Discover the impact and mitigation steps.
CVE-2026-67567 (CVSS 9.9) leads three Red Hat privilege escalation flaws in ACM and FreeIPA. Two FreeIPA bugs can reach full domain compromise.
A critical Red Hat vulnerability, CVE-2026-66780 (CVSS 9.9), enables a MITM attack across a cluster mesh. Two more critical flaws disclosed.
Red Hat ACM privilege escalation flaws (CVE-2026-70496, CVSS 9.9) let attackers seize full cluster control. See the three Kubernetes bugs.
A Vault Secrets Operator vulnerability, CVE-2026-8715, lets tenants read pod files and gain privilege escalation. Patch to 1.5.0 now.
CVE-2026-66792 (CVSS 9.9) and two more Red Hat ACM flaws allow full compromise of the managed cluster via privilege escalation.
Red Hat fixes RHACM remote code execution flaws, including CVE-2026-72526 and CVE-2026-73268, both CVSS 9.9. See patch and mitigation steps.
CVE-2026-44945 lets a default Rancher user gain full admin control via cross-cluster impersonation. Privilege escalation rated CVSS 9.1.
CVE-2026-10090 lets an edit-scoped user gain cluster-admin in Red Hat ACM for Kubernetes. Privilege escalation rated CVSS 9.9.
Kyverno vulnerability CVE-2026-54523 (CVSS 9.6) is public with PoC exploit code. It lets a tenant gain admin in any namespace. Update to v1.18.2.
CVE-2026-15378 is a blind SSRF in Red Hat OpenShift AI. The guardrails-detectors flaw exposes cloud credentials and Kubernetes secrets.

A critical 9.6 CVSS flaw in Argo CD (CVE-2026-42880) allows read-only users to extract plaintext Kubernetes secrets via Server-Side Diffs. Patch to v3.3.9 now!
SAP developers are under attack. A surgical credential stealer hijacks CI/CD runners and cloud tokens via npm preinstall hooks. Rotate all secrets immediately.
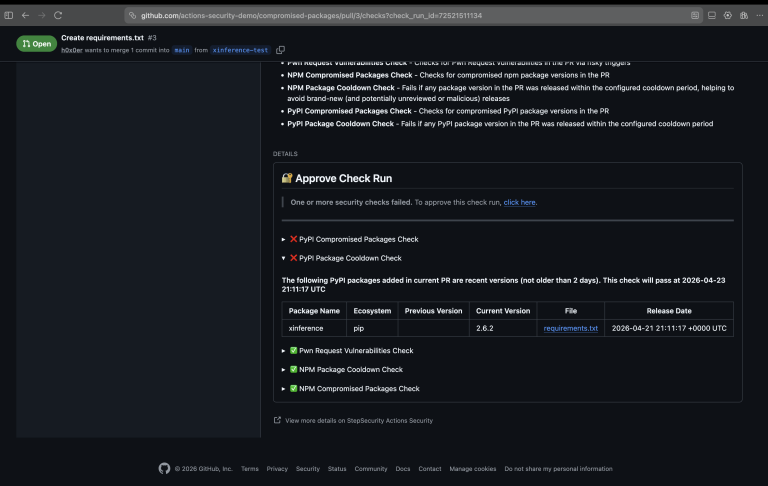
Critical supply chain attack hits Xinference (v2.6.0-2.6.2). TeamPCP’s malware siphons cloud credentials and MLOps secrets. Audit your MLOps pipeline today.
Juju hits a perfect 10.0 CVSS score (CVE-2026-4370). A TLS flaw on port 17666 lets attackers hijack clusters. Update to 3.6.20 or 4.0.5 now!

Kyverno (CVE-2026-4789) faces an unpatched SSRF flaw in its CEL HTTP functions, allowing attackers to bypass K8s namespaces. Secure your cluster now!
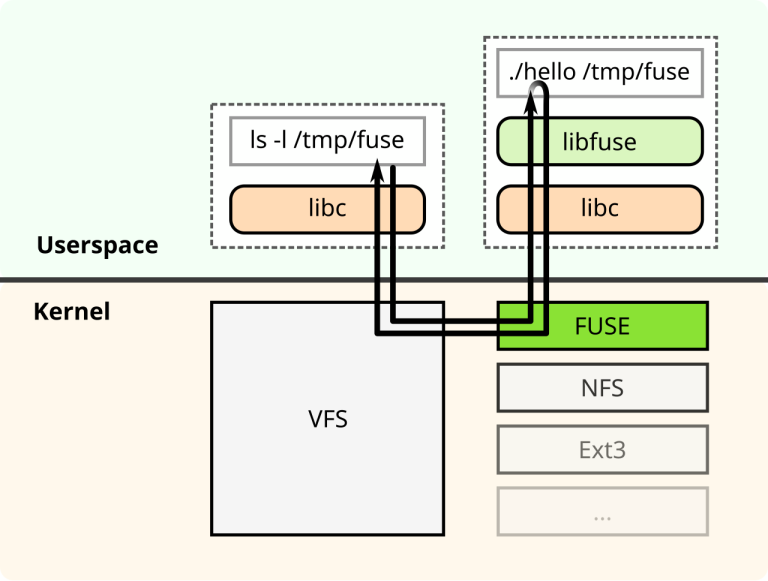
Researchers uncover two flaws in libfuse's io_uring transport (CVE-2026-33150 & 33179). Impacting Kubernetes CSI drivers, these bugs allow RCE and DoS. Patch now!
GoHarbor's Harbor faces a critical 9.4 CVSS flaw (CVE-2026-4404). Default admin passwords allow total registry compromise and image poisoning. Update now.