 Do Son
In the complex world of cloud-native applications, Kubernetes and Amazon Elastic Kubernetes Service (EKS) have become the...
Kubernetes

The Apache CloudStack project has released new Long-Term Support (LTS) versions—4.19.3.0 and 4.20.1.0—to address five security vulnerabilities,...

As containers become the backbone of modern software deployment, many organizations still misjudge their isolation guarantees —...

Red Hat has recently unveiled an open-source initiative named llm-d, designed to address the most critical demand...

Argo CD, the widely adopted GitOps continuous delivery tool for Kubernetes, has issued a high-severity security advisory...

The containerd project has issued an urgent security advisory for a critical vulnerability in its container runtime,...

A critical security vulnerability has been identified in the Bitnami Pgpool-II Docker image and the bitnami/postgres-ha Kubernetes...
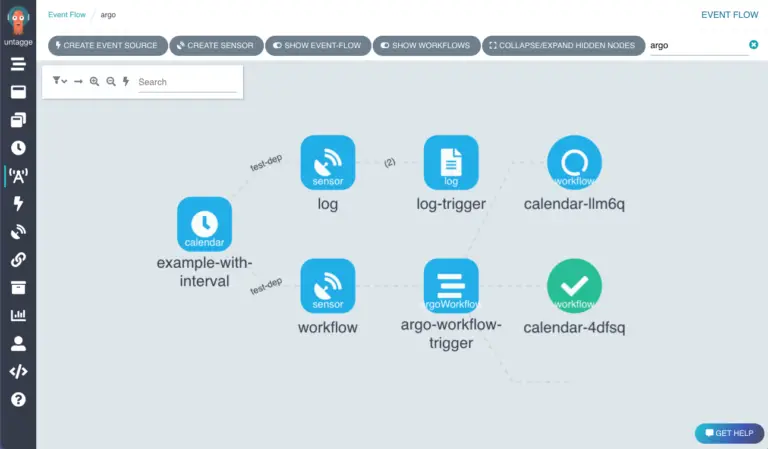
A critical security vulnerability has been discovered in Argo Events, an event-driven workflow automation framework for Kubernetes....

A new vulnerability in JumpServer (CVE-2025-27095) has been disclosed, exposing Kubernetes clusters to potential compromise through token...

A series of critical security vulnerabilities has been discovered in the Ingress-NGINX Controller for Kubernetes, posing a...

A new cybersecurity threat has been identified by Wiz Research, dubbed “IngressNightmare,” which exposes critical vulnerabilities in...
A high-severity vulnerability has been identified in the kcp project, a Kubernetes-like control plane designed for multi-tenant...

A recent report from Aqua Security has uncovered significant security risks in Kubernetes policy enforcement, particularly in...

A severe vulnerability (CVE-2024-52281) has been discovered in Rancher, an open-source container management platform widely used for...

Argo Workflows, a widely-used open-source tool for orchestrating workflows in Kubernetes, has become a valuable asset for...

OpenAI experienced a significant service disruption on December 11, 2024, impacting all its services, including ChatGPT, the...
A high-severity vulnerability has been discovered in Kubernetes, potentially allowing attackers to execute arbitrary commands outside of...

GitLab has released a critical security update addressing a high-severity vulnerability that could grant unauthorized access to...

The Kubernetes Security Response Committee has disclosed two security vulnerabilities (CVE-2024-9486 and CVE-2024-9594) in the Kubernetes Image...

Datadog Security Research has uncovered a new and widespread malware campaign targeting Docker and Kubernetes environments, where...

A newly discovered security vulnerability, CVE-2024-7646, has been identified in the widely used ingress-nginx controller for Kubernetes,...

Akamai researcher Tomer Peled has uncovered a concerning design flaw within Kubernetes’ git-sync project. This flaw could...