 Do Son
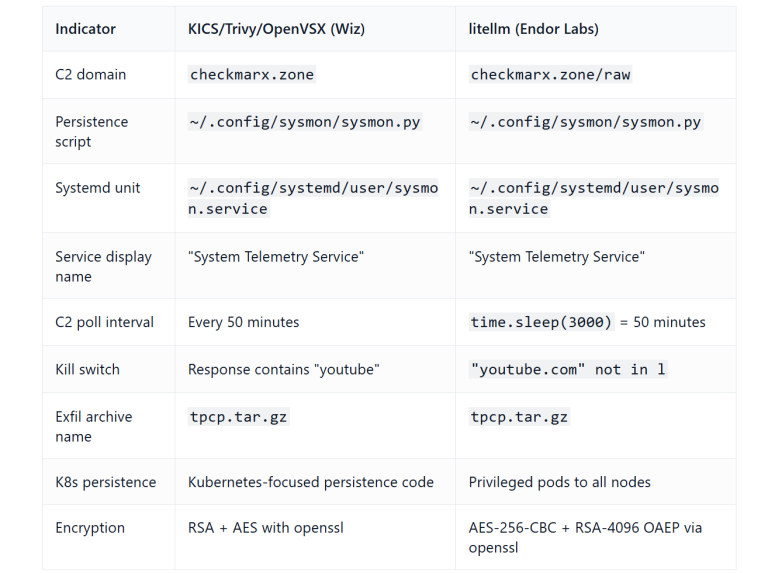
95M-download LiteLLM library hijacked on PyPI. TeamPCP's backdoor steals cloud tokens and hijacks Kubernetes clusters. Check for version 1.82.8 now.
Kubernetes
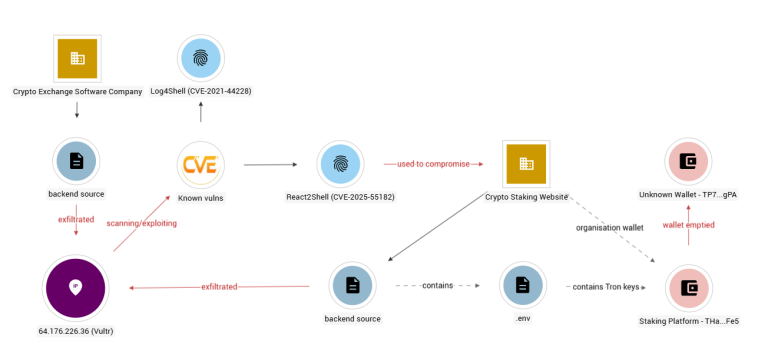
Ctrl-Alt-Intel exposes a suspected DPRK campaign using an 'Amazon Kill Chain' and React2Shell to systematically breach crypto exchanges and steal code.

CVSS 10.0 Alert: Kubernetes Local Path Provisioner flaw (CVE-2025-62878) allows host file overwrites. Upgrade to v0.0.34 immediately.

High-severity Rancher CLI flaw (CVE-2025-67601) exposes credentials via MitM attacks when using --skip-verify. Update or use -cacert immediately.

Critical Ingress-Nginx flaws (CVE-2026-1580) allow RCE and secret theft via config injection. Upgrade to v1.13.7 or v1.14.3 immediately to secure K8s.

CVE-2025-62877: A 9.8 critical flaw in Harvester HCI allows attackers to hijack servers using default credentials during install. Update to v1.7.0!

A Headlamp flaw allows unauthenticated users to reuse cached credentials to hijack Kubernetes Helm operations. Update to v0.39.0!

A critical flaw (CVSS 9.1) in Red Hat OpenShift GitOps lets namespace admins gain root access to the cluster by manipulating ArgoCD CRs. This effectively breaks multi-tenancy. Patch immediately.

Google rapidly adopts the MCP protocol, launching managed servers for AI agents. This enables seamless, autonomous tool use across Google Maps, BigQuery, and GKE infrastructure.

OCI patched three critical runc flaws allowing container escape and host DoS/RCE. Attackers exploit mount race conditions in maskedPaths and /dev/console bind-mounts. Update to v1.2.8+.
SUSE patched a Critical RCE flaw (CVE-2025-54469, CVSS 10.0) in NeuVector Enforcer that allows attackers to inject commands via unsanitized environment variables, risking container root shell access.

Argo CD patches multiple High-severity DoS flaws. A single unauthenticated webhook request can crash the entire argocd-server process via improper JSON handling.

A critical flaw (CVE-2025-10725) in Red Hat OpenShift AI allows low-privileged users to escalate to full cluster admin privileges, risking complete platform compromise.

SUSE patches three flaws in Rancher Manager. A phishing vulnerability (CVSS 8.1) can steal admin tokens, while a DoS flaw can lock out administrators.
A medium-severity vulnerability (CVE-2025-9708) in the Kubernetes C# client allows MITM attacks and API impersonation. Update now to patch.

A high-severity flaw (CVE-2025-9566) in Podman allows malicious containers to overwrite host files via a symlink traversal attack. A patch is available in Podman v5.6.1.

A new high-severity vulnerability in SUSE Rancher's Fleet engine (CVE-2024-52284) exposes sensitive Helm chart credentials in plain text.

A critical flaw in NeuVector (CVE-2025-8077) allows attackers to bypass authentication with a hardcoded password, exposing Kubernetes clusters to full compromise.
A critical privilege escalation flaw in Capsule Kubernetes (CVE-2025-55205) allows tenant users to bypass security and launch cross-tenant attacks.

A critical flaw (CVE-2025-41240, CVSS 10.0) in Bitnami Helm charts exposes Kubernetes secrets via publicly accessible paths, allowing unauthenticated remote access. Update immediately!
Kubernetes warns of CVE-2025-7342 (CVSS 8.1) in Image Builder. Default credentials in Windows VM images (Nutanix/OVA) allow unauthenticated root access to clusters. Patch immediately!

NVIDIA patched critical vulnerabilities in its Container Toolkit and GPU Operator, allowing privilege escalation, data tampering, and DoS in containerized environments.