 Do Son
Calif released details and PoC code for an OpenBSD kernel vulnerability enabling local privilege escalation to root. Apply errata 018 and 026.
Local Privilege Escalation
Four Linux kernel privilege escalation flaws were disclosed with public PoC exploits granting local root. Details and patches are now out. Update now.
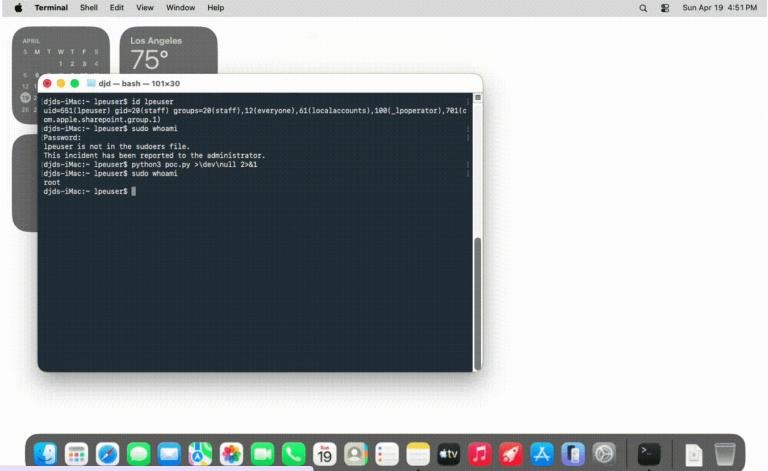
Details and PoC exploit code for CVE-2026-39875 are now public. This macOS privilege escalation flaw lets a malicious app gain root. Patch now.
CVE-2026-49176 is a Windows WalletService elevation of privilege flaw. Full details and a public PoC exploit are out, so patch Windows now.
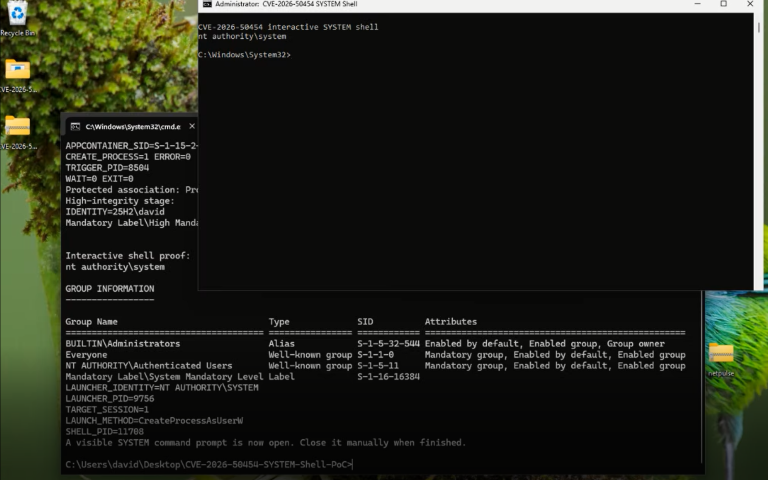
A public proof-of-concept details the Windows AppResolver LPE (CVE-2026-50454), a UAC bypass that chains an admin token to a SYSTEM shell.
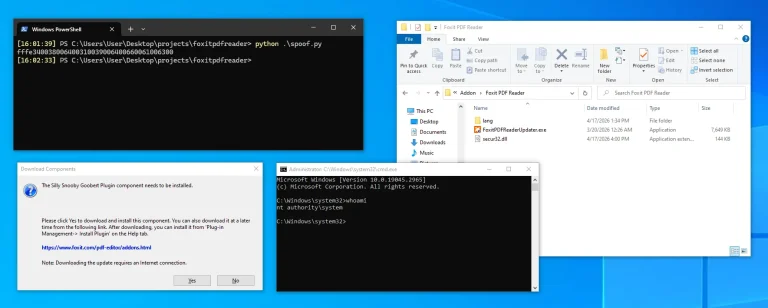
A public proof-of-concept for CVE-2026-57239 turns a Foxit PDF Reader vulnerability into full SYSTEM privileges via local privilege escalation.
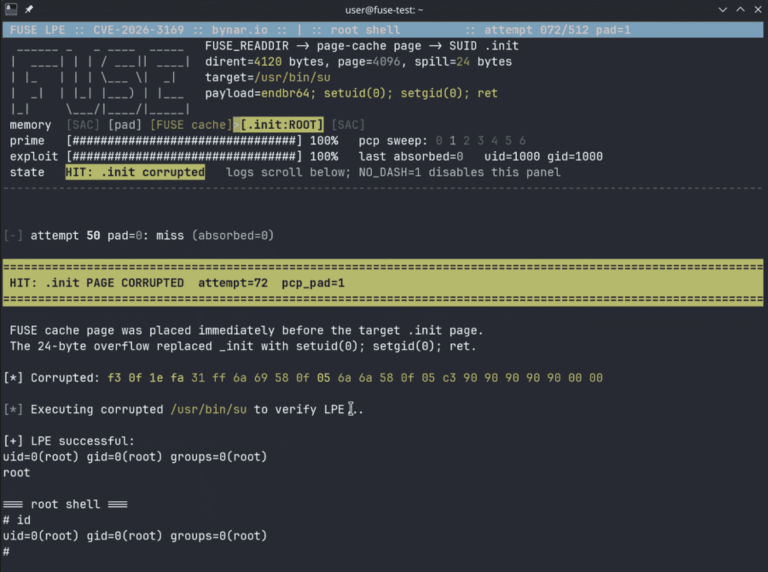
Public PoC and full details are out for CVE-2026-31694, a Linux kernel FUSE page cache overflow that gives local privilege escalation to root. Patch now.
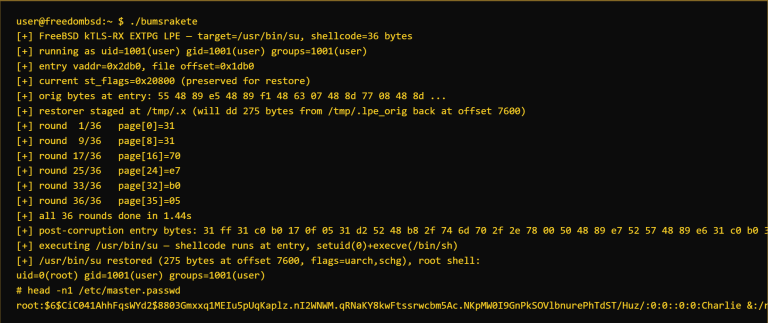
A public PoC exploit for the FreeBSD kTLS vulnerability (CVE-2026-45257) enables local privilege escalation to root. Patch your FreeBSD systems now.
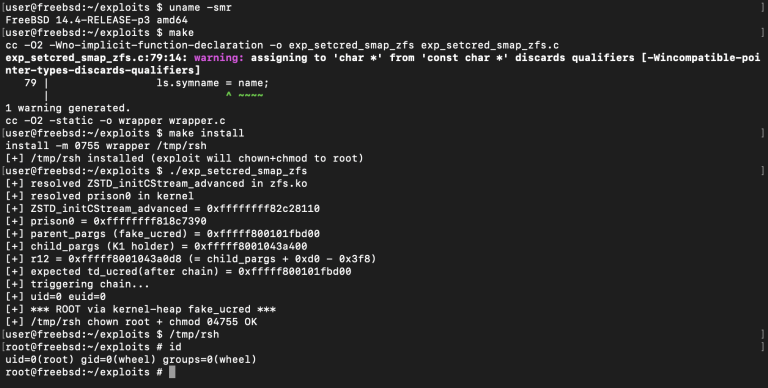
A critical FreeBSD kernel buffer overflow vulnerability is exposed. Learn more about this threat now that public exploit code released.

Security researcher Asim Manizada has released public details and a PoC for the CIFSwitch local root exploit impacting many Linux systems.
HP patches critical 9.3 CVSS flaw CVE-2026-8631 in HPLIP drivers. Unauthenticated attackers can bypass memory limits for Linux remote code execution.

Microsoft pivots on its "by design" stance, updating Edge to version 148.0 to stop caching your entire plaintext password vault in active volatile memory.
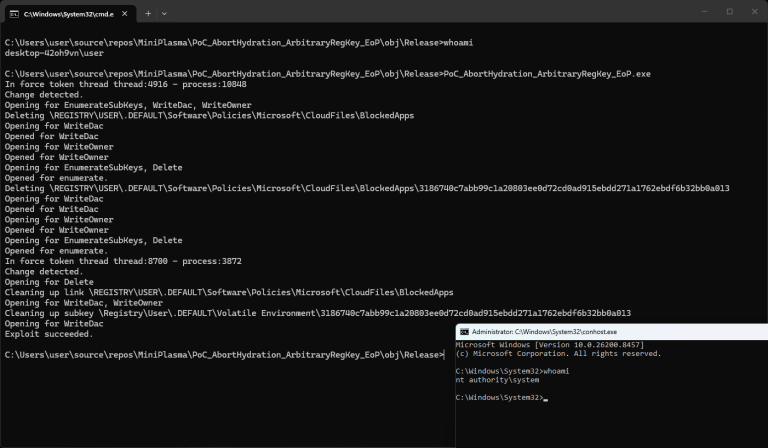
Details and PoC code for the "MiniPlasma" zero-day exploit are now public. See how a 6-year-old flaw grants SYSTEM access on fully patched Windows 11.
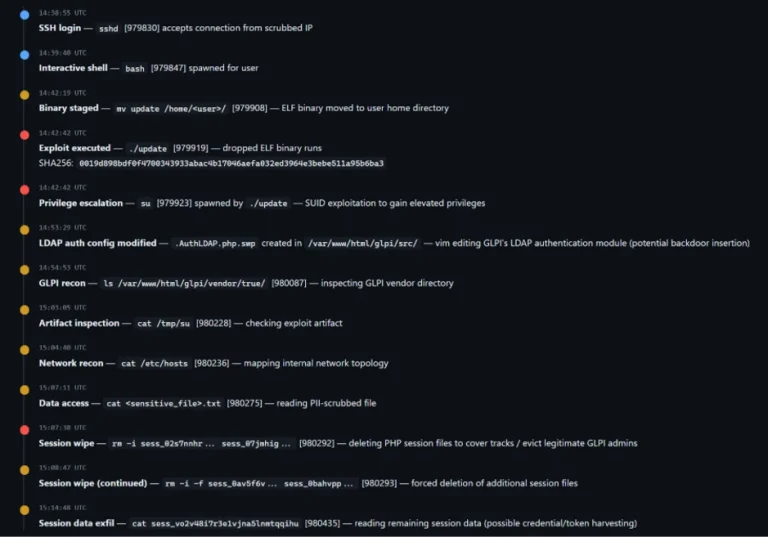
The Dirty Frag Linux vulnerability (CVE-2026-43284) is being actively exploited in the wild. Learn how to secure your servers from this root LPE exploit.
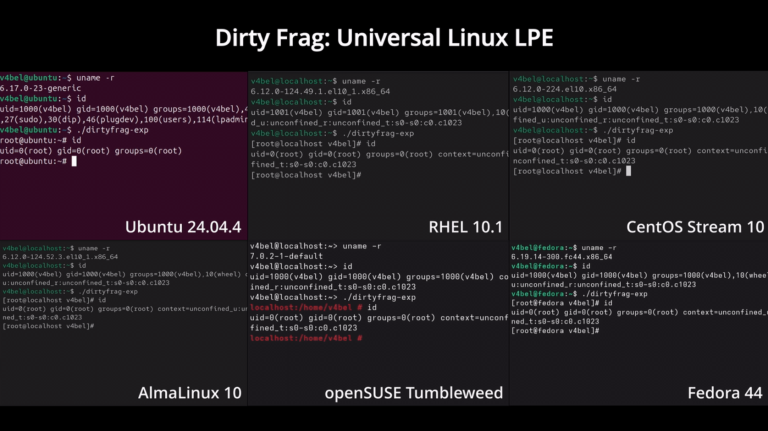
Dirty Frag PoC released! Researcher v4bel discloses a universal Linux root exploit targeting the page cache. No patches yet—apply module mitigations now!
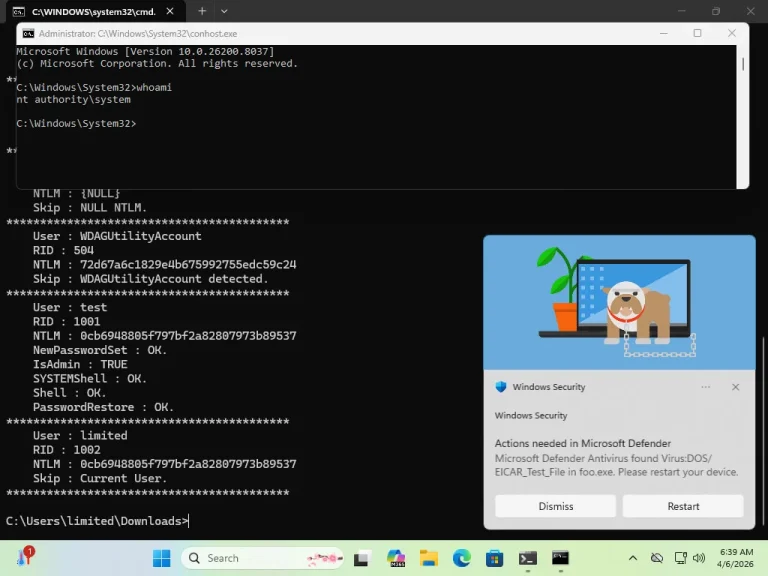
CISA adds BlueHammer (CVE-2026-33825) to the KEV catalog. This Microsoft Defender LPE exploit uses TOCTOU to hijack SAM databases. Patch by May 6, 2026.
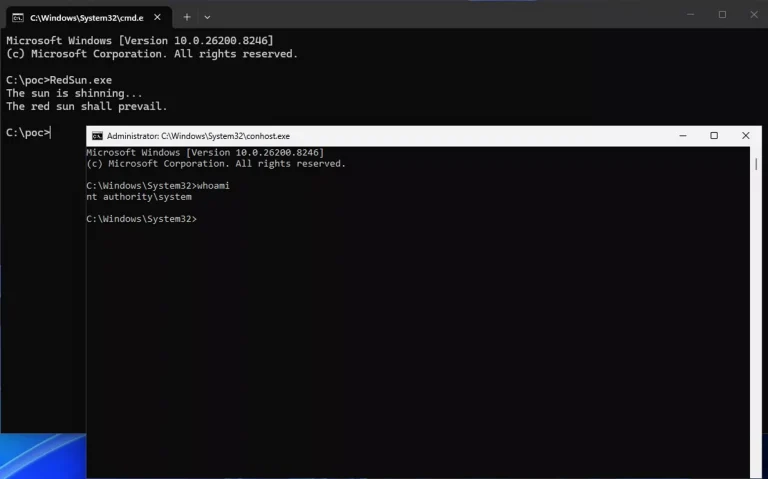
Microsoft Defender faces a critical "Red Sun" vulnerability. Learn how this zero-day exploit bypasses security to grant hackers full administrative control.
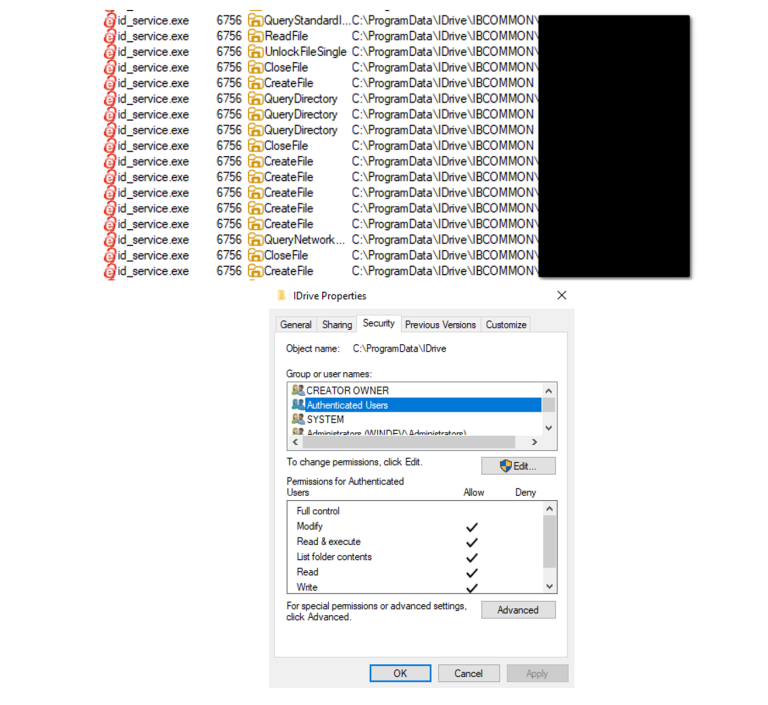
A critical flaw in IDrive for Windows (CVE-2026-1995) allows low-privilege users to seize SYSTEM control via weak folder permissions. Audit your PC today.
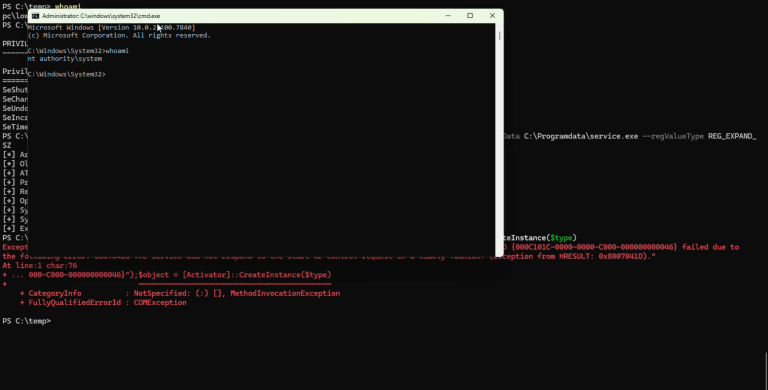
Exploit code and details for RegPwn (CVE-2026-24291) are publicly disclosed. The Windows local privilege escalation flaw grants attackers SYSTEM access.
Qualys discovers CVE-2026-3888, a critical Local Privilege Escalation (LPE) flaw in Ubuntu Desktop. Learn how a 30-day time window exposes root access.
A critical Sudo vulnerability in the exec_mailer function allows local attackers to bypass security restrictions and escalate privileges to root access.

Splunk Enterprise Windows flaws (CVSS 7.7) CVE-2026-20143 & CVE-2026-20140 allow system takeover via DLL and Python search path hijacking. Patch immediately.