 Do Son
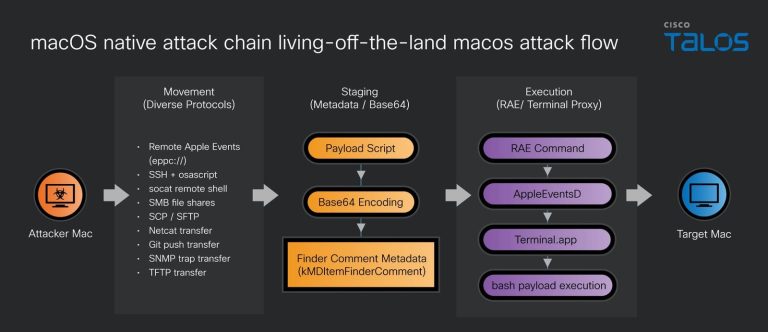
Cisco Talos reveals how attackers use native macOS features like Spotlight and SNMP to hijack enterprise workstations. Secure your DevOps environment today.
LotL
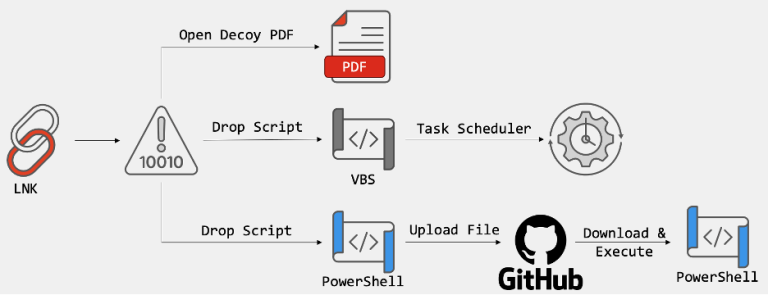
FortiGuard Labs unmasks a South Korean espionage wave abusing the GitHub API for C2 and using LNK files to stay invisible. Protect your network from LotL.
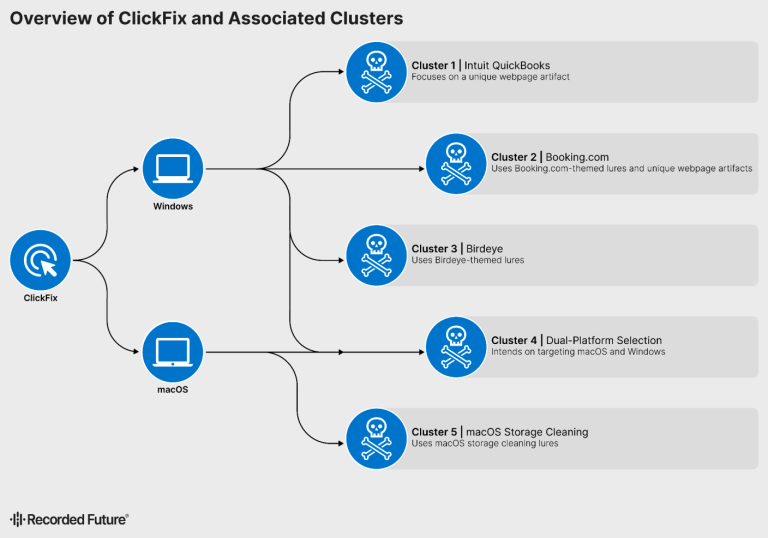
ClickFix has evolved into a high-ROI malware template used by APT28. Learn how this social engineering trick bypasses security by mimicking system errors.

Trend Micro exposes KongTuke's new "CrashFix" tactic, which tricks enterprise users via fake Chrome errors into deploying the fileless modeloRAT backdoor.

A movie torrent scam uses a DiCaprio film lure to infect PCs with Agent Tesla RAT. The attack chain uses LNK files and malicious code hidden in a subtitle file to achieve fileless execution via LotL tools.

Symantec exposed a Russian-aligned espionage campaign in Ukraine using LotL tactics. Attackers used a Sandworm-linked webshell (Localolive) and abused scheduled tasks to dump credentials and bypass Windows Defender.