 Do Son
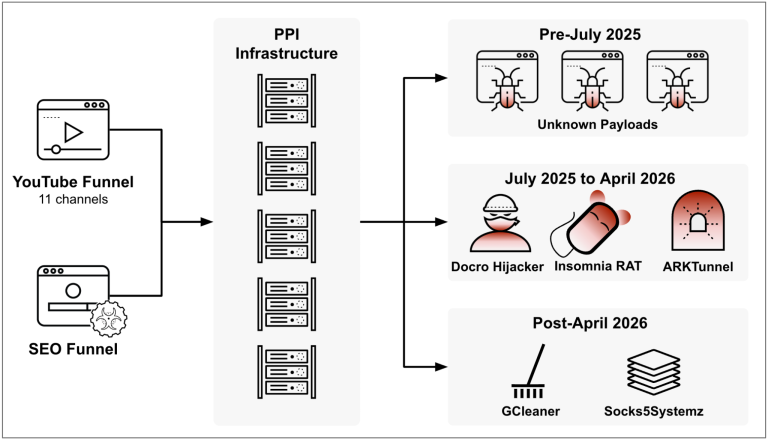
Unit 42 uncovered a large OfferLoader malware campaign distributing backdoors. Discover how OfferLoader malware abuses YouTube to compromise endpoints.
Malware Analysis
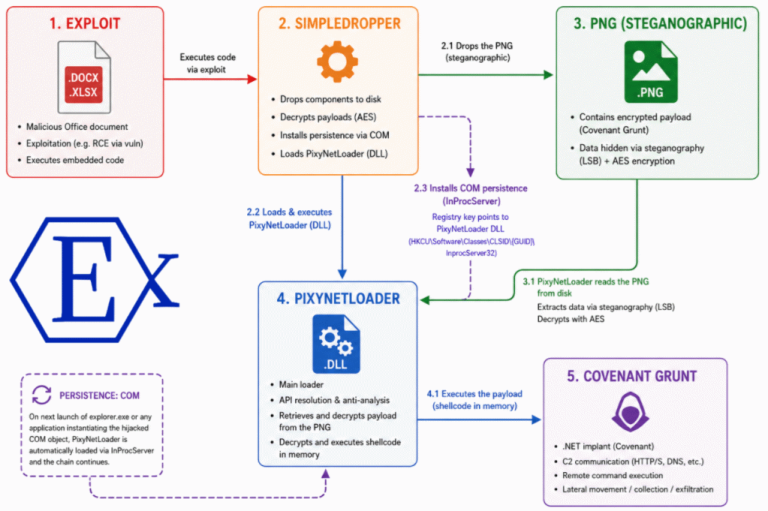
Researchers expose PixyNetLoader malware analysis revealing APT28's steganography APT28 attack, hiding Covenant Grunt payloads inside PNG pixels since 2024.
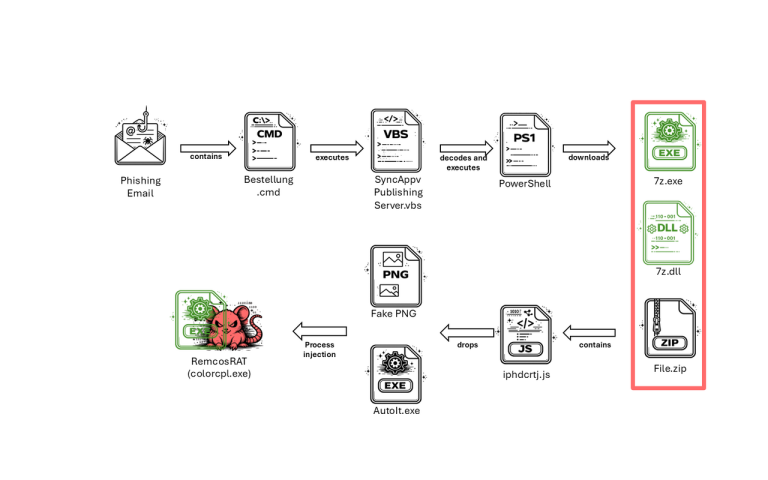
G Data uncovers a new Remcos RAT variant using DonutLoader shellcode and trusted LOLBins to bypass Windows security filters.
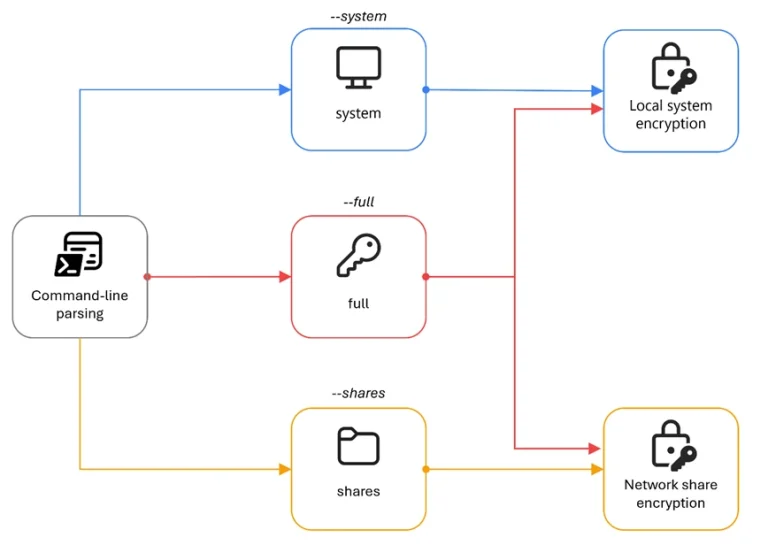
A deep Gentlemen ransomware threat analysis by Microsoft Threat Intelligence reveals an aggressive worm capability and double extortion tactics.
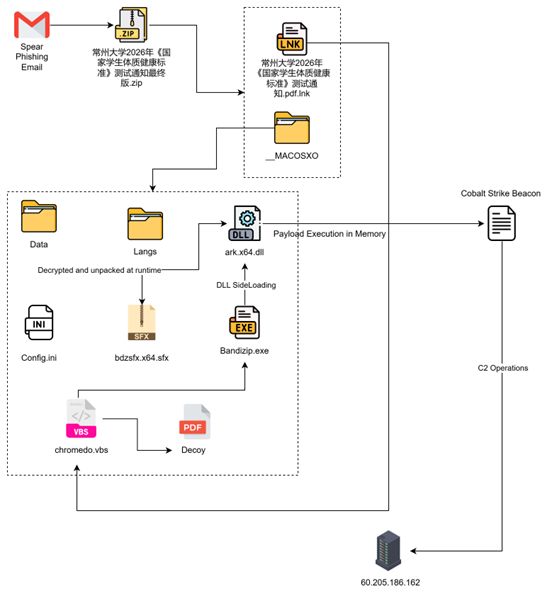
Discover how the Operation Dragon Whistle phishing campaign leverages student fitness lures to deploy stealthy memory-only malware.
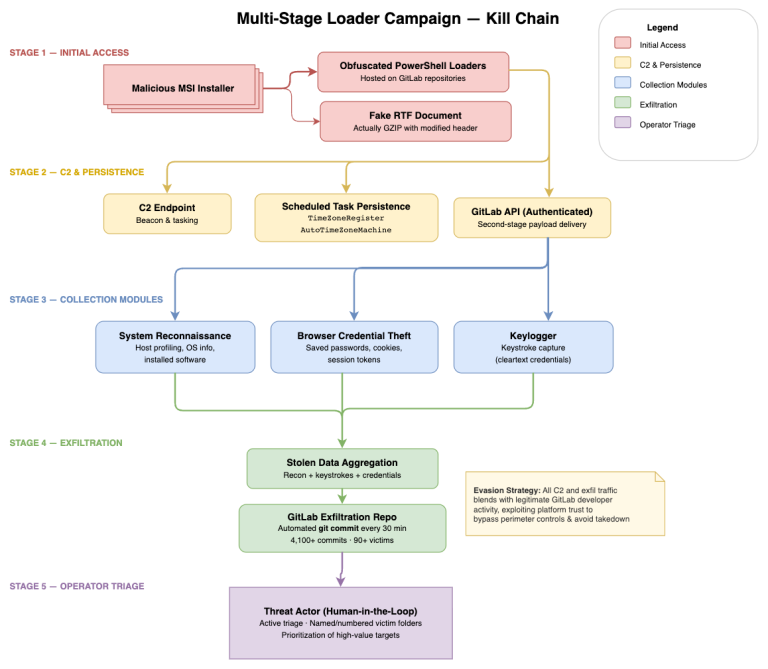
Velvet Chollima leaks its own backend infrastructure keys inside a malicious "Tralert FX" installer signed with a valid EV certificate.

Point Wild exposes a sophisticated PyInstaller loader using in-memory AMSI patching and SHA-512 decryption to drop XWorm V7.4. Patch now!

Cato CTRL intercepts "TencShell," a new stealth malware derived from open-source Rshell. Attackers use third-party access to breach networks!
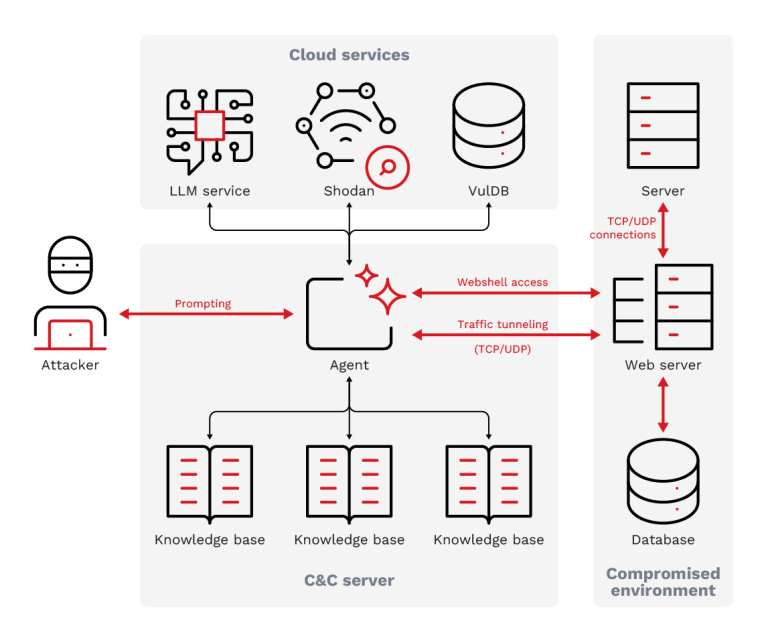
TrendAI exposes SHADOW-AETHER: threat groups using agentic AI to "vibe code" custom backdoors and automate intrusions across government and financial sectors.

Gen Digital exposes a JDownloader site breach (May 6-7, 2026). Attackers used WDAC policies to kill antivirus and r77 rootkits for total system invisibility.

GemStuffer exploits RubyGems as an illicit data transport to scrape UK council portals. Discover how this supply chain attack bypasses standard defenses.
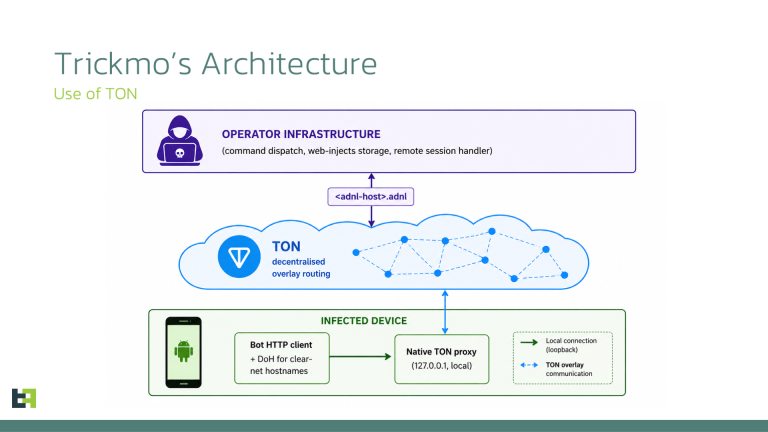
ThreatFabric uncovers TrickMo Variant C, a new Android banking trojan using the decentralized TON network to evade detection and turn phones into proxies.
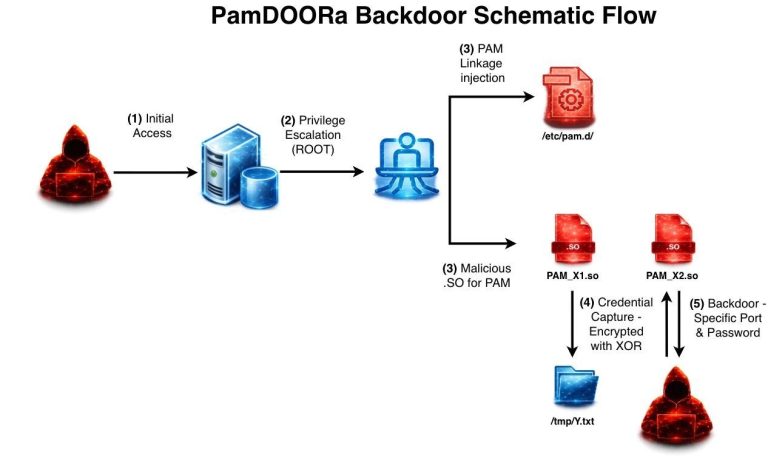
Flare unmasks PamDOORa: a $1,600 Linux backdoor that hijacks the PAM stack to harvest credentials and manipulate authentication logs to evade detection.
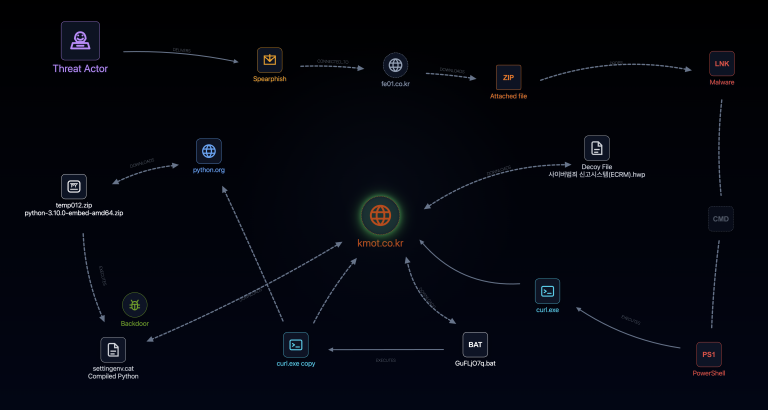
Genians unmasks an APT37 campaign using environment variable tricks and compiled Python malware to bypass EDR. Protect your network from these stealthy lures.
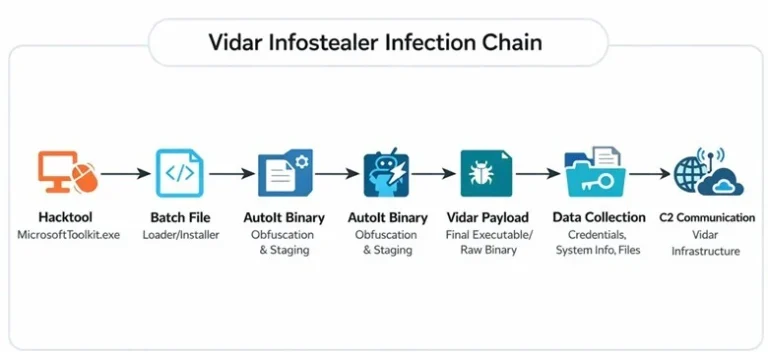
LevelBlue unmasks a stealthy Vidar Stealer campaign using AutoIt scripts and file renaming tricks to bypass EDR and harvest credentials. Is your system at risk?
Urgent: 84 TanStack npm packages hijacked to harvest GitHub Actions secrets. Over 12M weekly downloads impacted. Audit your CI/CD pipelines and rotate tokens.
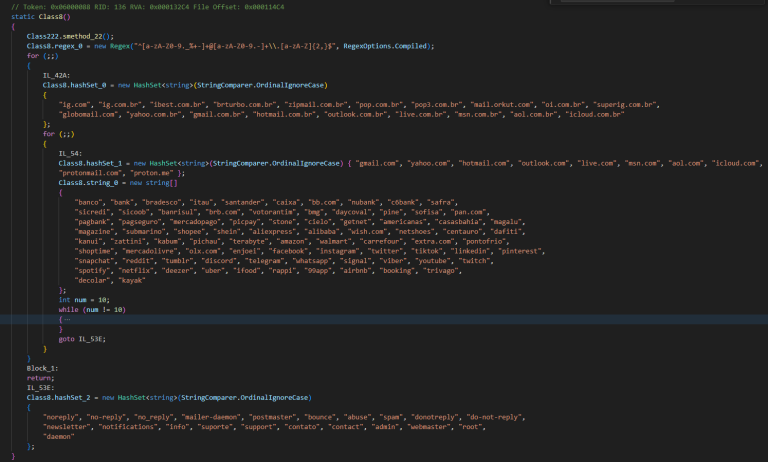
Elastic Security Labs exposes TCLBANKER, an advanced banking trojan that hijacks WhatsApp to spread while blinding defenders with invisible WPF overlays.
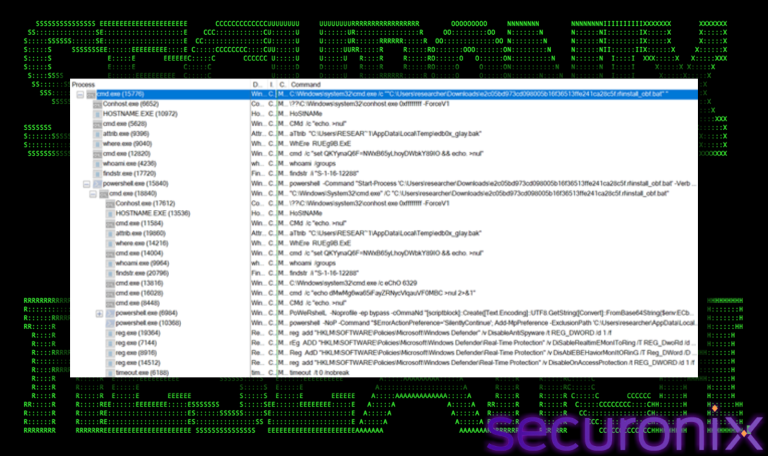
Meta Description (152 Characters)Securonix uncovers Deep#Door: a self-contained Python RAT that uses TCP tunneling and obfuscated scripts to bypass traditional defense. Secure your systems now.
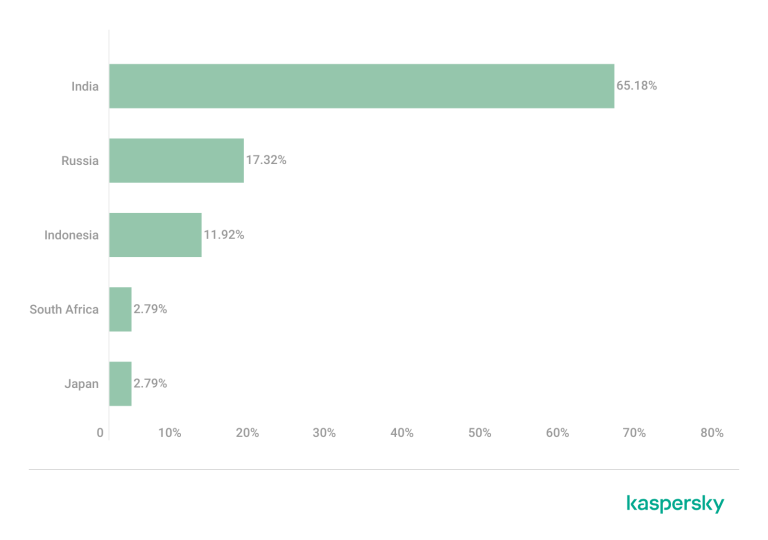
Silver Fox targets India and Russia with tax-themed phishing and the new ABCDoor backdoor. Learn how this Python-based threat hijacks screens and data.
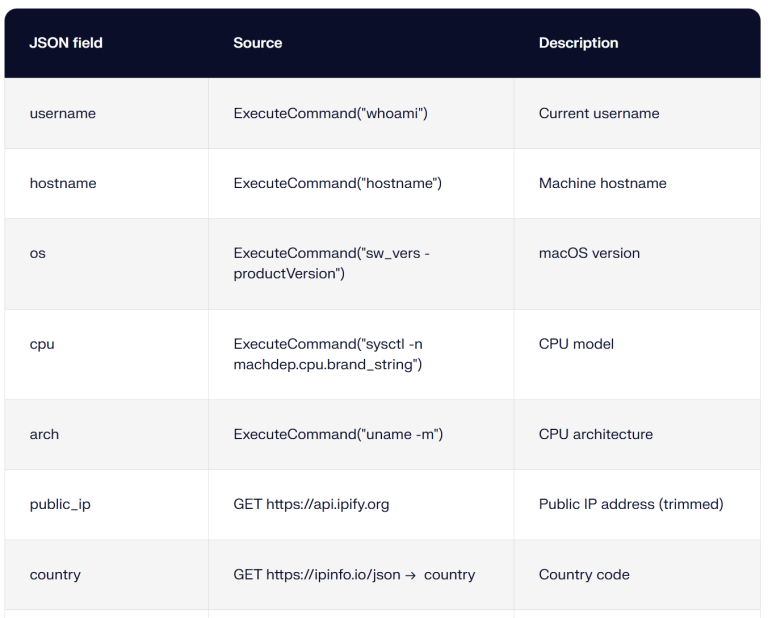
Minirat, a Go-based macOS RAT, exploits npm supply chains to bypass security. It features VM detection, AES encryption, and persistence. Secure your dev tools.
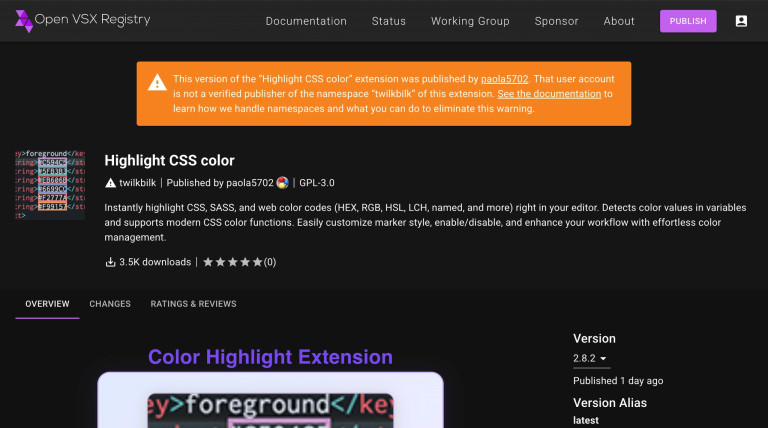
Socket uncovers GlassWorm: a 73-extension sleeper campaign on Open VSX targeting VS Code and Cursor. Stealthy .node binaries turn trusted tools into malware.
Check Point Research reveals VECT 2.0 ransomware is a broken wiper. A critical flaw makes file recovery impossible for files over 128KB. Read the analysis.