 Do Son
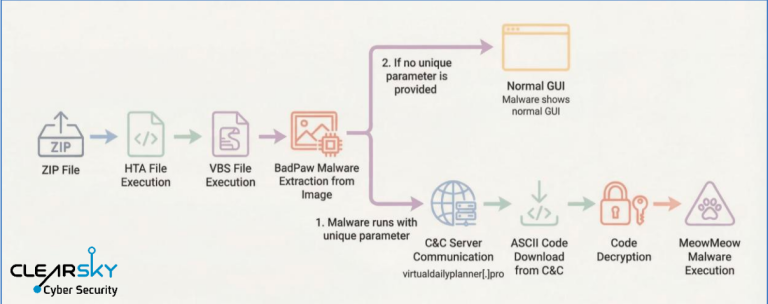
ClearSky uncovers a Russian campaign targeting Ukraine with BadPaw and MeowMeow malware, using steganography and feline decoys for stealthy espionage.
Malware Analysis

Check Point Research uncovers Silver Dragon, an APT41-linked group using the GearDoor backdoor and Google Drive for stealthy cyber espionage.
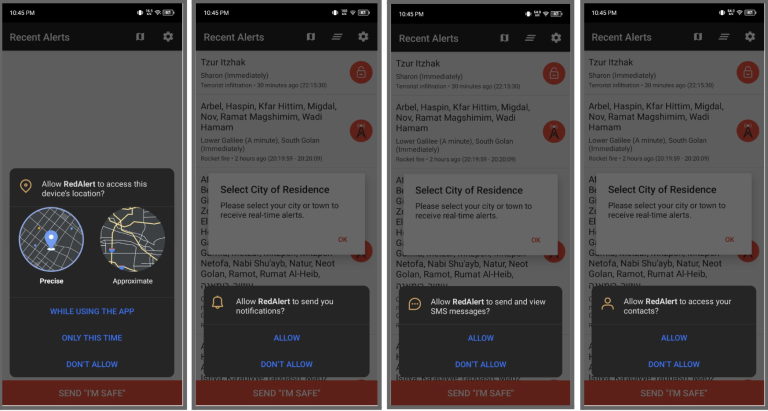
CloudSEK exposes a smishing campaign spreading a trojanized "Red Alert" app. The fake emergency tool tracks locations and steals data during air raids.

CYFIRMA reveals a new cyber espionage campaign by Transparent Tribe (APT36) targeting Indian defense with stealthy multi-stage malware and decoy PDFs.
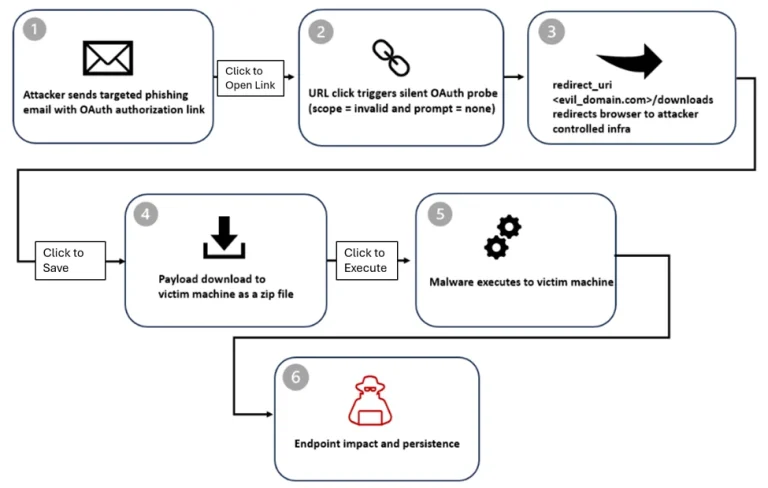
Microsoft Defender reveals a new phishing campaign abusing OAuth redirect URIs to bypass security and deliver stealthy malware to your system.
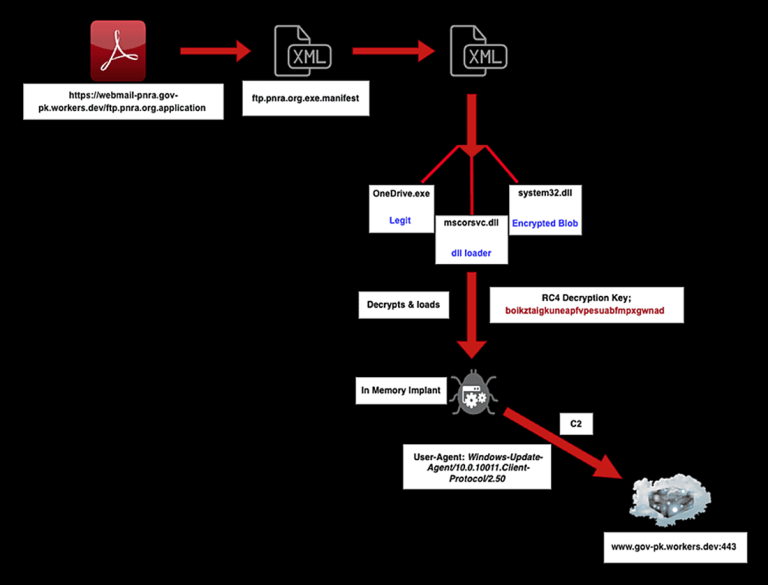
Arctic Wolf details a year-long cyber espionage campaign by Sloppy Lemming, deploying the custom BurrowShell malware against Pakistan and Bangladesh.
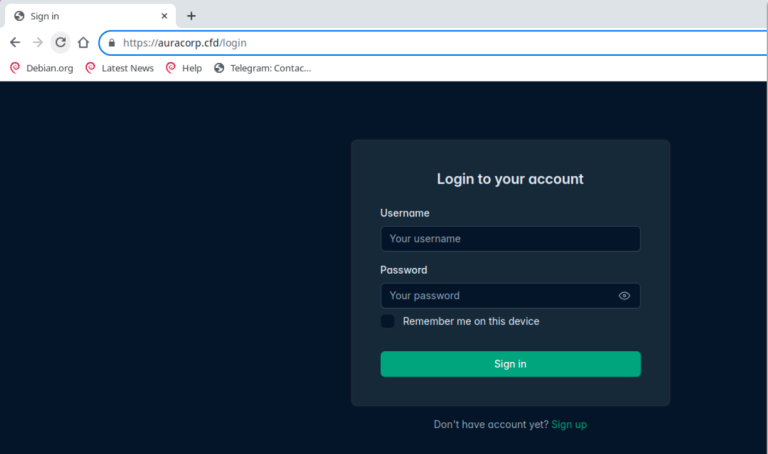
Following the Lumma takedown, the sophisticated AuraStealer malware is rapidly gaining ground, using TikTok scams and stealth to harvest data.

LAB52 exposes a new China-aligned espionage campaign using fake meeting invitations and G DATA antivirus components to stealthily deploy the PlugX RAT.

G DATA reveals how pirated gaming site PiviGames distributes ACRStealer via "spaghetti code" HijackLoader and DLL sideloading, causing total account takeovers.
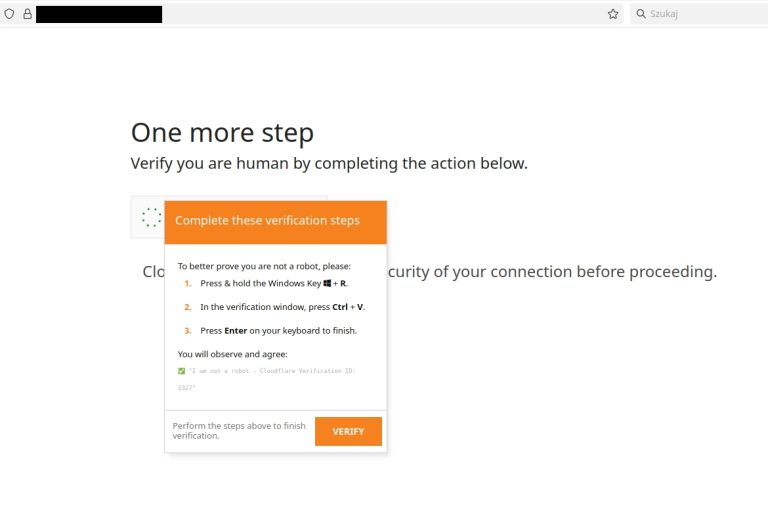
CERT Polska reveals how a fake "ClickFix" CAPTCHA campaign tricked users into deploying evasive Latrodectus and Supper malware. Protect your network now.
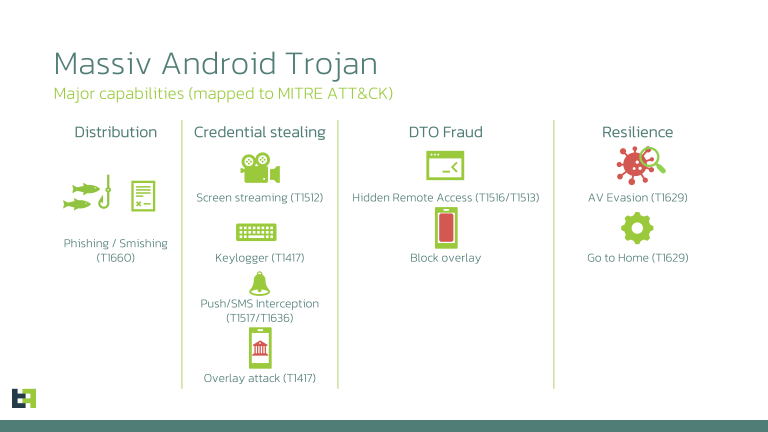
ThreatFabric exposes Massiv, a new Android banking Trojan hiding in fake IPTV apps. The malware uses accessibility permissions for full device takeover.

LockBit 5.0 launches with a unified codebase targeting Windows, Linux, and ESXi. Acronis reveals identical encryption and ties to SmokeLoader.

OysterLoader malware uses custom LZMA & steganography to evade tools. Linked to Rhysida ransomware, it hides in fake IT installers.

Cisco Talos reveals VoidLink, a modular Linux malware framework by UAT-9921. Features "compile-on-demand" tools to target IoT & cloud infrastructure.

New LTX Stealer malware abuses Node.js & Inno Setup to bypass antivirus. This $10 tool steals browser passwords & crypto wallets. Stay alert.

Zscaler analyzes GuLoader's evolution. The malware uses Google Drive, polymorphic code, and exception-based obfuscation to evade detection.
Black Basta ransomware now embeds a vulnerable NsecSoft driver (BYOVD) to silently kill antivirus processes like Sophos & CrowdStrike.

Zscaler reveals Marco Stealer, a new malware harvesting crypto & cloud files. It uses AES-256 encryption & kills analysis tools. Learn how to detect it.

Cisco Talos exposes DKnife, a router malware that inspects traffic and swaps legitimate downloads for ShadowPad backdoors. Active since 2019.

Microsoft warns of "CrashFix": malicious extensions crash browsers to trick users into running a "fix" that installs a RAT. Beware fake ad blockers.

Darktrace dissects SnappyBee (Deed RAT), a stealthy Salt Typhoon backdoor. Learn how it uses DLL side-loading & memory hooking to evade modern AV.

Silver Fox APT targets users with fake LINE installers delivering ValleyRat. New campaign uses rare "PoolParty" injection to evade detection.