
 Do Son
Amaranth-Dragon (APT-41 nexus) weaponized WinRAR flaw CVE-2025-8088 in just 10 days. Southeast Asian govts targeted with malicious RAR archives.
Malware Analysis

Lotus Blossom compromises Notepad++ infrastructure to deploy "Chrysalis" malware. Rapid7 reveals the group using Microsoft Warbird to evade detection.
New "PhantomVAI" malware recycles old Hackforums "RunPE" code to bypass modern EDR. Campaigns use task scheduler masquerading to deliver infostealers.

Interlock ransomware exploits a zero-day in gaming anti-cheat drivers to blind defenses. "Hotta Killer" tool targets education sector. Read the analysis.

Attackers use fake DHL invoices to sideload Phantom Stealer v3.5.0 via a signed Java utility. Malware hides in AddInProcess32.exe. Watch out.

INJ3CTOR3 hackers target FreePBX with EncystPHP web shell via CVE-2025-64328. Malware uses cron jobs for persistence. Patch immediately.

TA584 triples activity with new "Tsundere Bot" malware. Attackers use invisible Registry keys to hide persistence. Read the Proofpoint analysis.
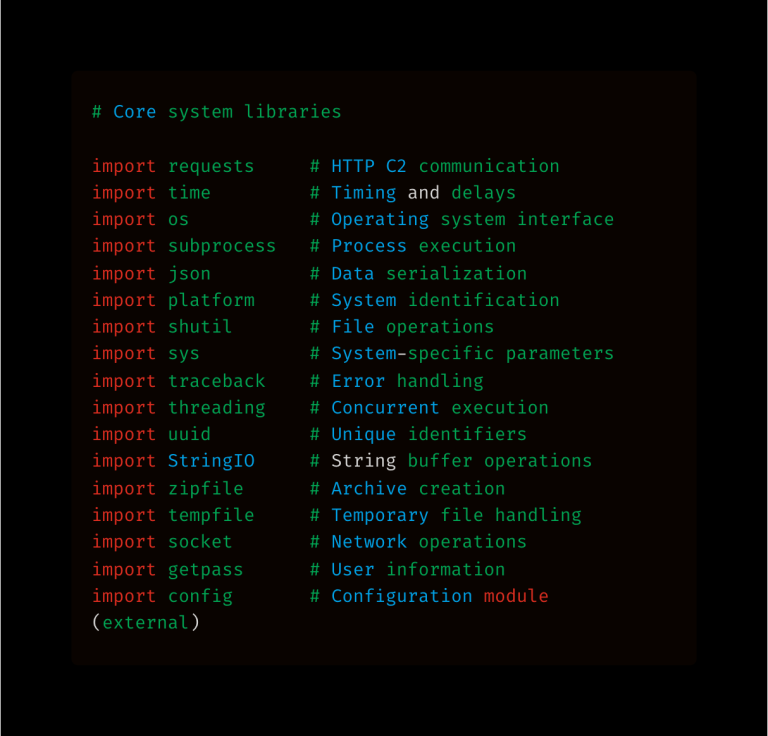
K7 Labs uncovers a stealthy Python-based RAT disguised as an ELF binary. Features adaptive beaconing and anti-forensics to stay hidden. Read the analysis.

New AI-generated malware campaign targets job seekers. Vietnamese actor "Huna" uses fake job offers to deliver PureRAT via Dropbox.

New Fake CAPTCHA campaign uses Google Calendar & steganography to drop Amatera Stealer. See how this attack exploits legitimate Windows tools to stay hidden.
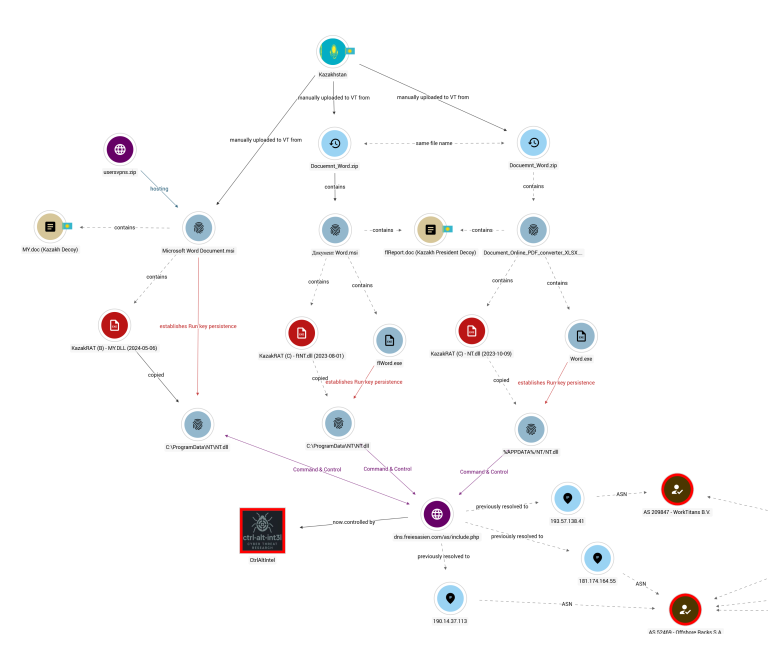
Researchers uncover "KazakRAT," a state-affiliated spyware targeting Kazakhstan & Afghanistan. A lapsed domain allowed experts to sinkhole the C2.

Seqrite exposes "Operation Covert Access": A Rust RAT targeting Argentina's legal system via fake court rulings. Includes anti-analysis & encryption tools.

Gootloader returns with malformed ZIPs to bypass detection. New alliance with Vanilla Tempest fuels Rhysida ransomware attacks. See the detection tips.

Resecurity finds PDFSIDER, a new APT malware using DLL side-loading and AES-256-GCM encryption to bypass EDR and open covert backdoors.

New malware campaign impersonates Malwarebytes installers. Hackers use DLL sideloading to deploy infostealers targeting crypto & MFA. Verify downloads now.

S2W reveals DragonForce is a "cartel" hacking rivals like BlackLock. Built on LockBit 3.0 code, they offer "Ransombay" services. A decryptor was found.

New fileless Remcos RAT campaign uses a "[virus detected]" shipping lure to inject malware into memory via process hollowing. See how to spot it.

Mustang Panda targets US gov with new LOTUSLITE backdoor. Campaign uses Venezuela lures and DLL sideloading to evade detection.

Attackers exploit legitimate ahost.exe via DLL sideloading to deploy RATs & stealers. Trusted dev utility bypasses security scanners. Watch out.
Check Point reveals Sicarii ransomware is a Russian false flag operation. Despite Israeli branding, the group relies on machine-translated Hebrew.

Securonix reveals SHADOW#REACTOR: A stealthy framework using "text-only" fragments to deploy Remcos RAT in memory via MSBuild. Avoids disk detection.

ASEC warns: Hackers abuse Syncro, SuperOps & NinjaOne RMM tools via fake PDF lures. Learn how this phishing campaign installs persistent backdoors.