
 Do Son
Researchers unmask ResokerRAT, a stealthy Trojan using Telegram to spy on systems and block security tools like Task Manager. Is your PC calling home?
Malware Analysis
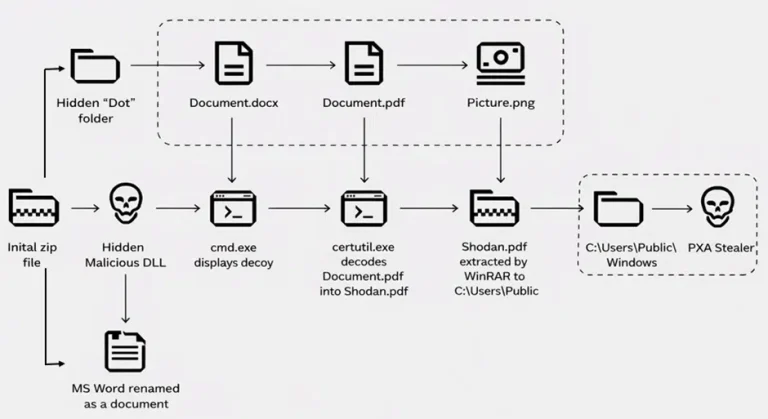
PXA Stealer activity surges in Q1 2026, targeting global finance. Learn how this Python-based malware uses Telegram and LOLBins to hijack crypto and banking data.
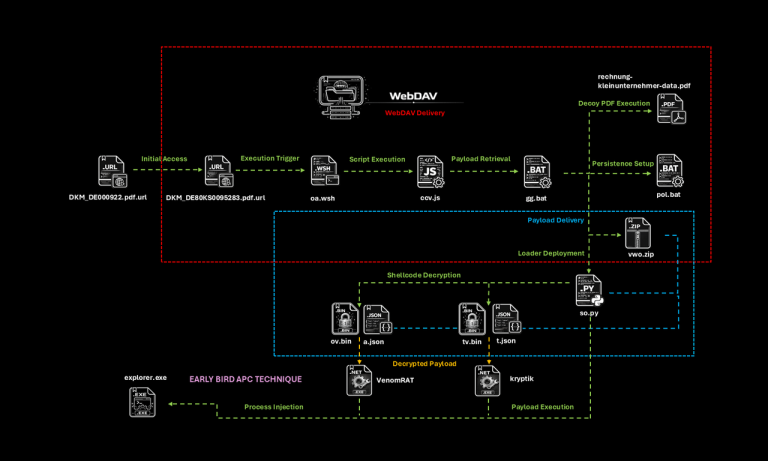
G DATA analysts chat with a malware author via Notepad while analyzing "Kiss Loader," a new threat using Early Bird APC injection and VenomRAT. Read more!
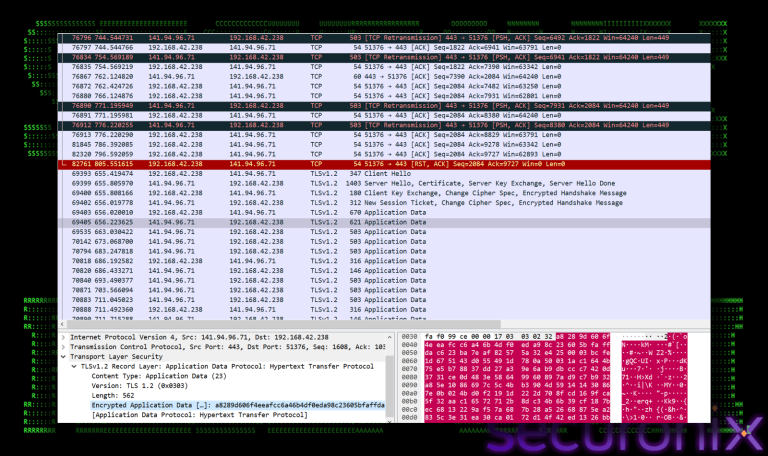
Securonix uncovers FAUX#ELEVATE, a 25-second attack using 10MB "inflated" VBScripts to steal credentials and mine crypto in French corporate environments.
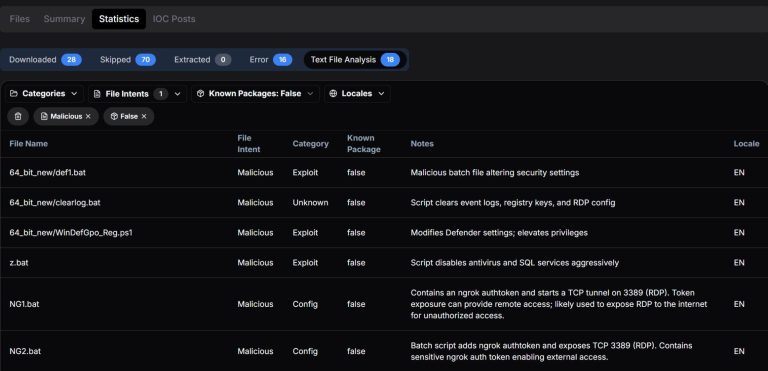
Hunt.io uncovers a Gentlemen ransomware toolkit on a bulletproof host. Learn how the z1.bat script destroys defenses and backups before encryption.
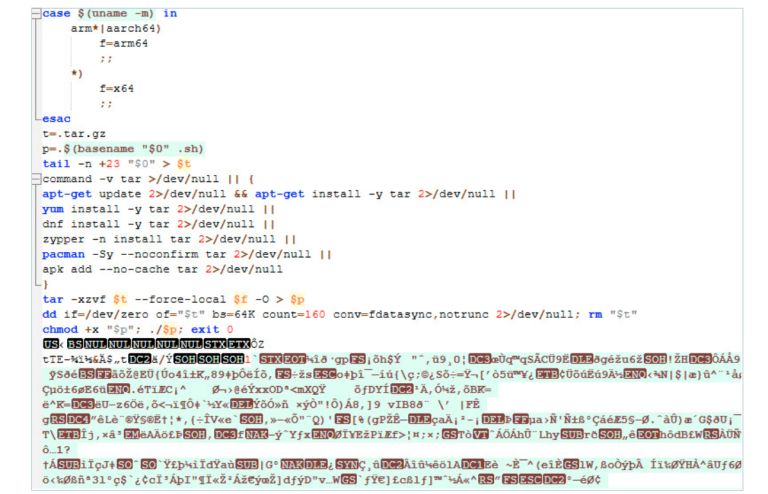
Morphisec uncovers Pay2Key’s Linux evolution. This dual-arch ransomware disables SELinux and AppArmor to encrypt x64/ARM64 servers. Secure your infra today!
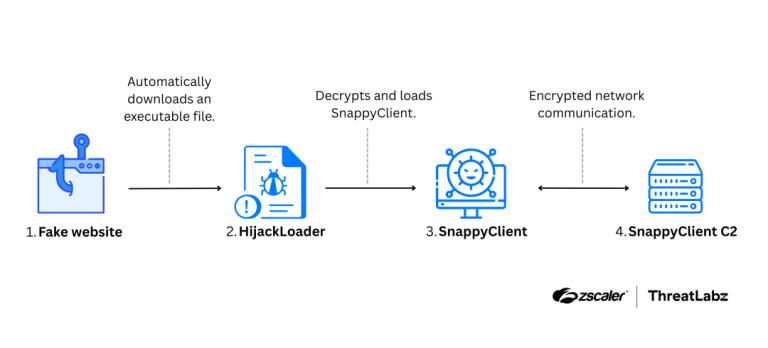
Zscaler ThreatLabz unmasks SnappyClient, a C++ C2 framework linked to HijackLoader. It uses AMSI bypass and Heaven’s Gate to steal crypto and gain remote access.
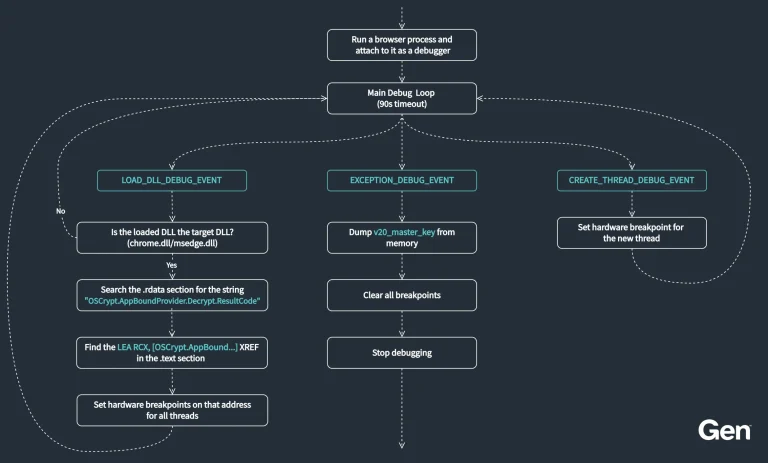
Gen Threat Labs uncovers VoidStealer, the first malware using a debugger-based bypass to extract Chrome and Edge encryption keys via hardware breakpoints.

Researchers reveal Infostealer.Speagle, a "parasitic" malware hijacking Cobra DocGuard infrastructure to mask the theft of sensitive ballistic missile data.
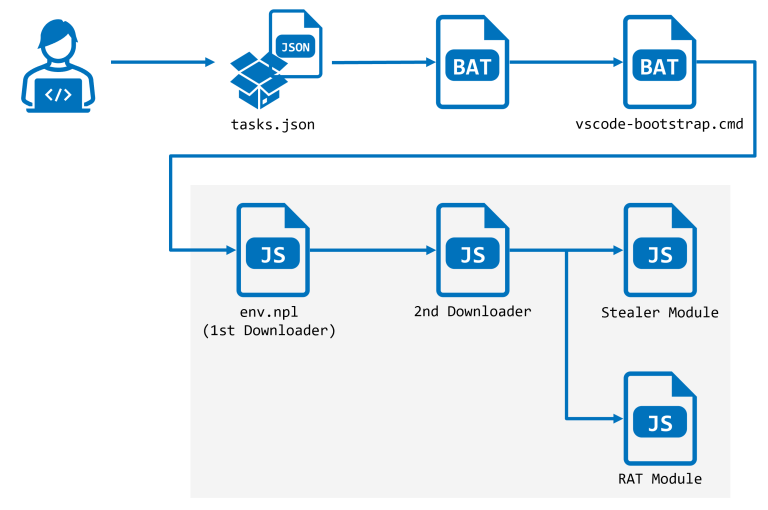
Researchers uncovered StoatWaffle, a new Node.js malware by North Korean hackers targeting developers via malicious VSCode repositories to steal data.
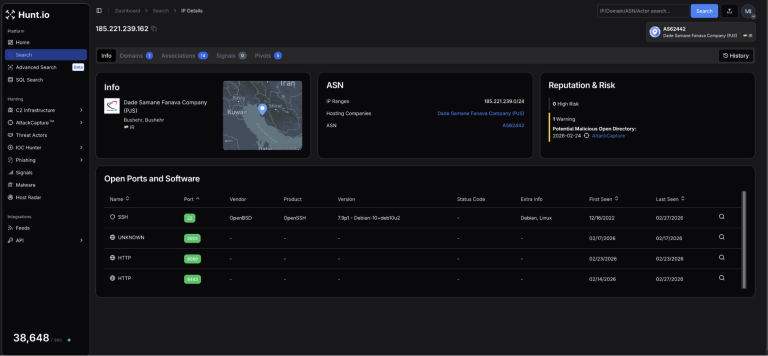
Hunt Intelligence uncovers the "Hex" botnet, a stealthy campaign using stolen SSH credentials and on-host compilation to evade traditional binary scanners.
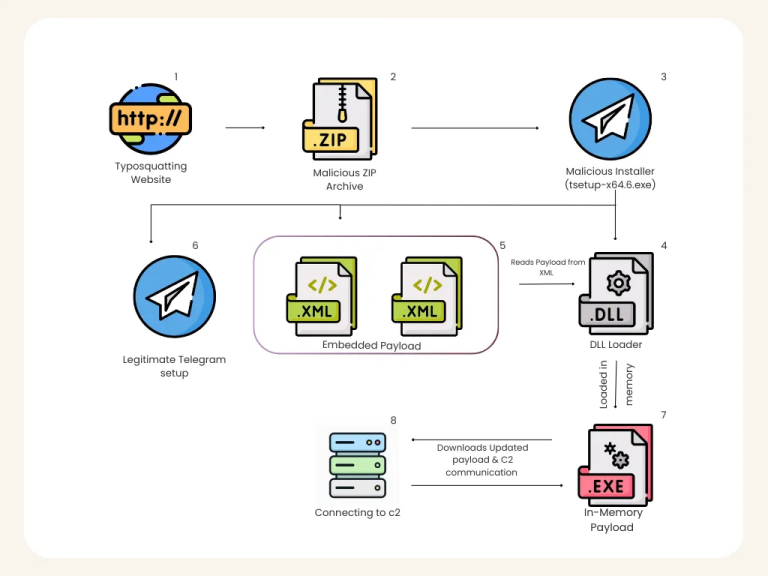
Researchers uncover a fake Telegram site distributing stealthy, memory-resident malware that bypasses Windows Defender. Always verify your download URLs.
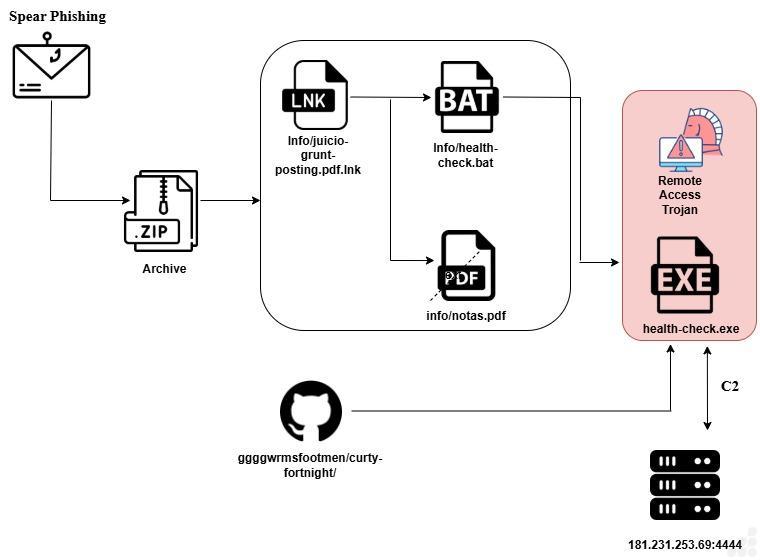
Lat61 Threat Intelligence uncovers a stealthy Rust RAT targeting Argentina's legal sector via weaponized judicial PDFs. Learn about its evasion tactics.
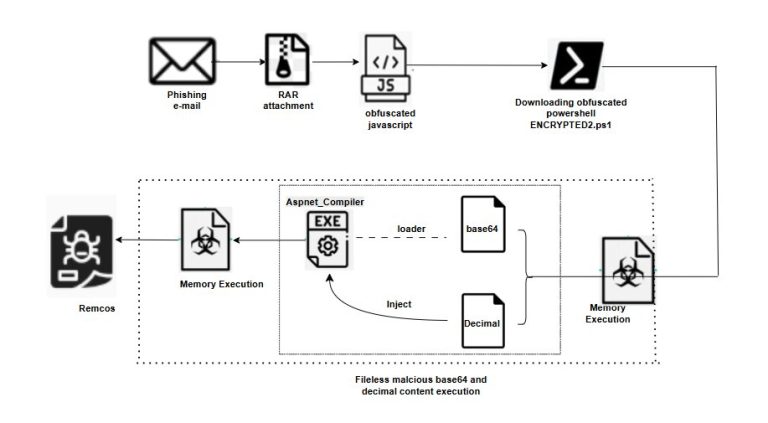
Trellix uncovers a stealthy, fileless Remcos RAT campaign utilizing process hollowing to execute entirely in memory and evade traditional security.
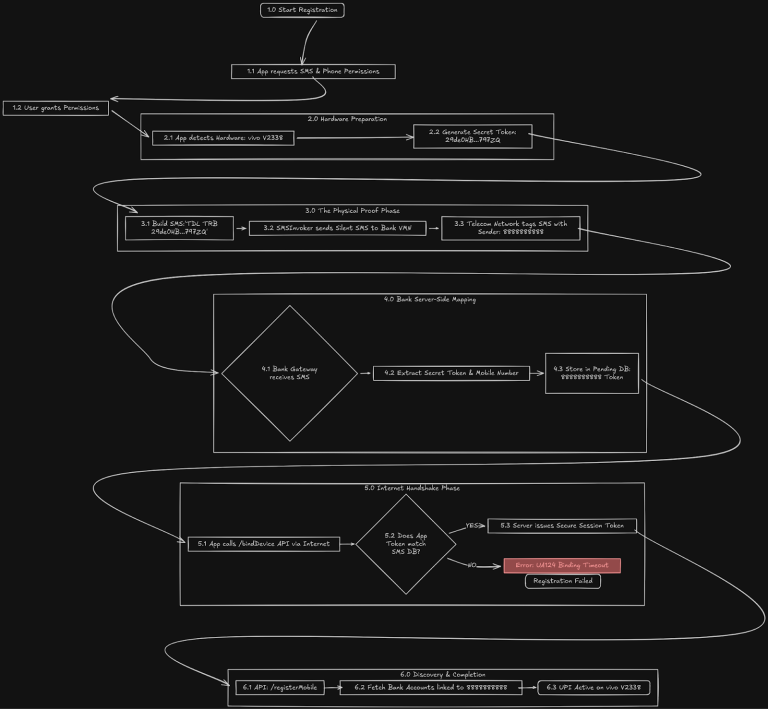
CloudSEK reveals how attackers use LSPosed and the "Digital Lutera" module to bypass Android UPI SIM-binding, gaslighting payment apps for remote fraud.
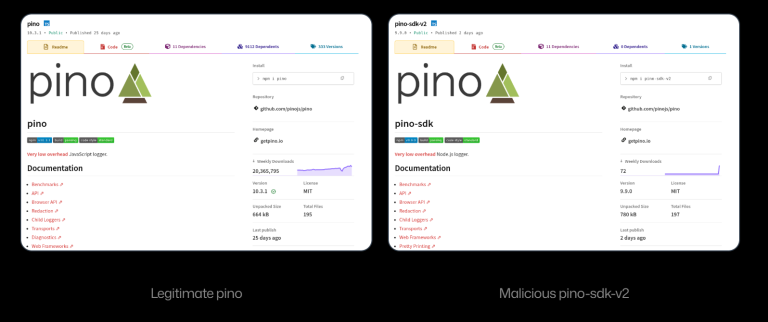
SafeDep uncovers pino-sdk-v2, a malicious npm package impersonating the pino logger to silently steal .env secrets and exfiltrate them via Discord.

Chinese APTs like Camaro Dragon are targeting Qatar with PlugX malware and Cobalt Strike, weaponizing Middle East tensions for cyberespionage.

Discover how attackers use shadow archives (CVE-2026-0866) to bypass AV and EDR by malforming ZIP metadata, keeping malware hidden but executable.
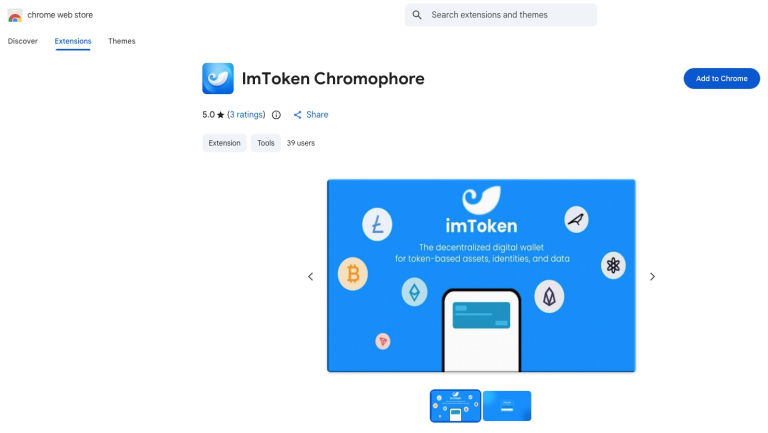
Socket researchers uncover "ImToken Chromophore," a malicious Chrome extension using fake branding and homoglyphs to steal crypto wallet seed phrases.
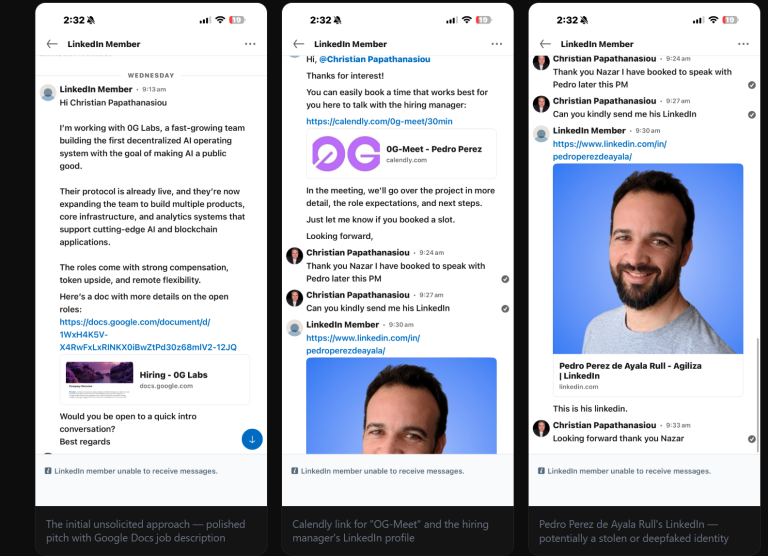
A fake LinkedIn recruiter and a poisoned GitHub repo: See how a CEO uncovered the North Korean "Contagious Interview" malware targeting Web3 developers.

Cisco Talos exposes UAT-9244, a China-linked APT targeting South American telecoms with stealthy malware like the BitTorrent-based PeerTime and TernDoor.

Researchers uncover a massive campaign by a Vietnamese operator using GitHub and Polygon blockchain smart contracts to distribute the StealC infostealer.