 Do Son
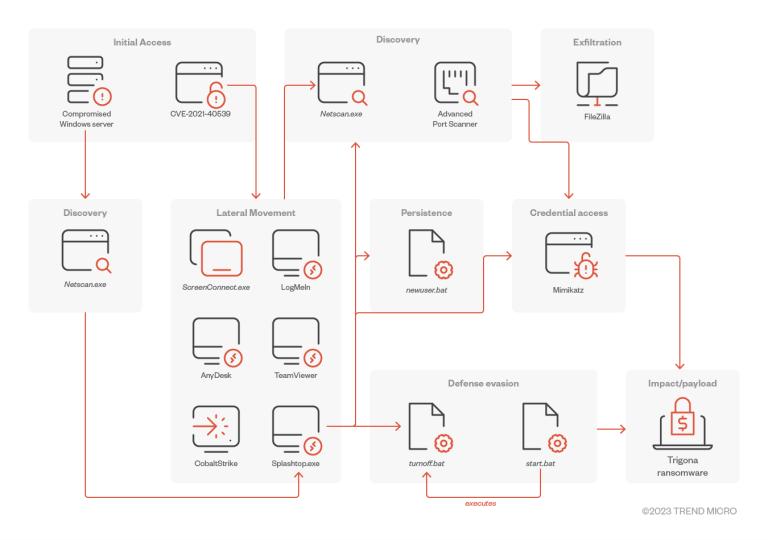
Trigona ransomware swaps Rclone for a custom tool that rotates connections to evade monitoring. Learn how uploader_client.exe powers their data theft.
Malware Analysis

Harvester APT expands to Linux using Microsoft Graph API for C2. Learn how the "GoGra" variant uses Outlook and "Zomato Pizza" lures to evade detection.
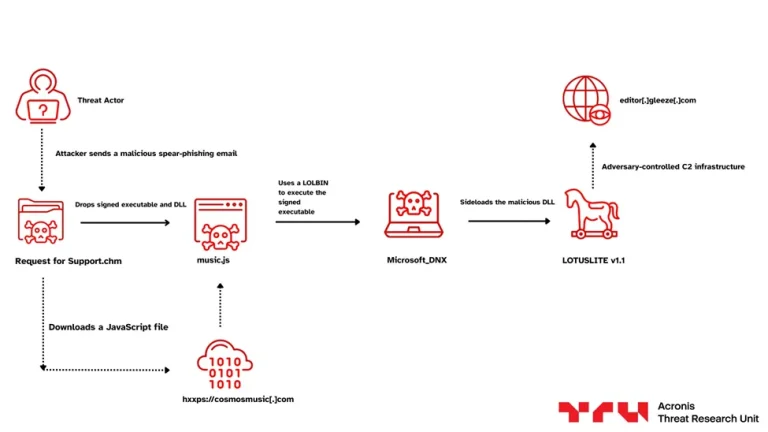
Mustang Panda targets India’s financial sector with the LOTUSLITE malware. Learn how this DLL sideloading campaign bypasses defenses for cyber-espionage.

Kaspersky uncovers Lotus Wiper, a destructive malware targeting Venezuela's energy sector. Designed for pure sabotage, it leaves systems unrecoverable.
Checkmarx Docker images and VS Code extensions hijacked by TeamPCP to siphon cloud secrets and spread via npm. Audit your "Dune" repositories today.
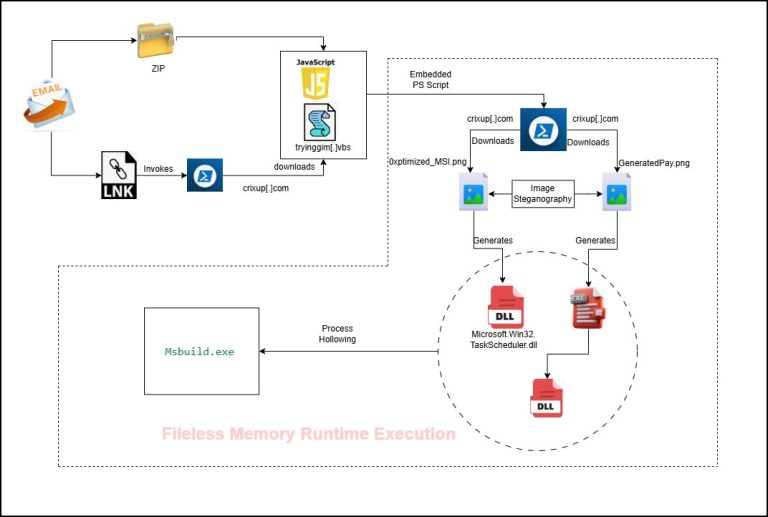
Trellix uncovers PureRAT, a modular Trojan hiding malware in PNG images. Learn how it uses steganography and fileless delivery to bypass Windows security.

BitSight unmasks RondoDox: a modular botnet using "nanomites" to dodge debuggers while hijacking 18 architectures for Monero mining and gaming DoS attacks.
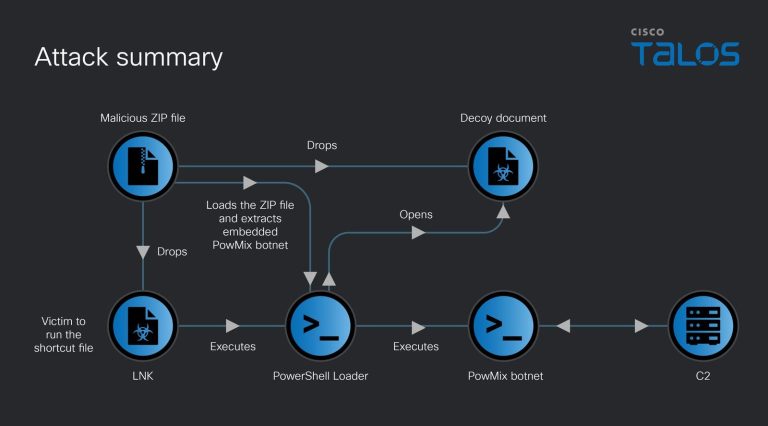
Cisco Talos uncovers PowMix, a stealthy botnet targeting Czech HR via AMSI bypass and Heroku-hosted C2. Learn how this malware evades modern EDR systems.
OpenAI unveils GPT-5.4-Cyber to counter Anthropic’s Claude Mythos. Explore the "cyber-permissive" model that reverse-engineers malware for verified defenders.
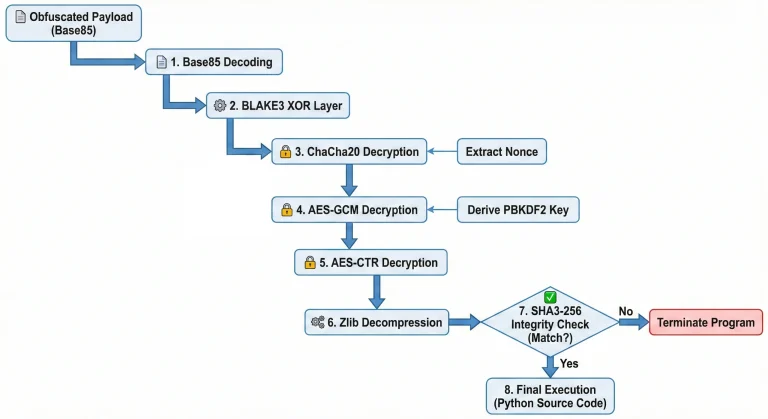
InfoGuard unmasks VIPERTUNNEL, a Python backdoor using sitecustomize.py for stealthy persistence in DragonForce ransomware attacks. Learn how to detect it.
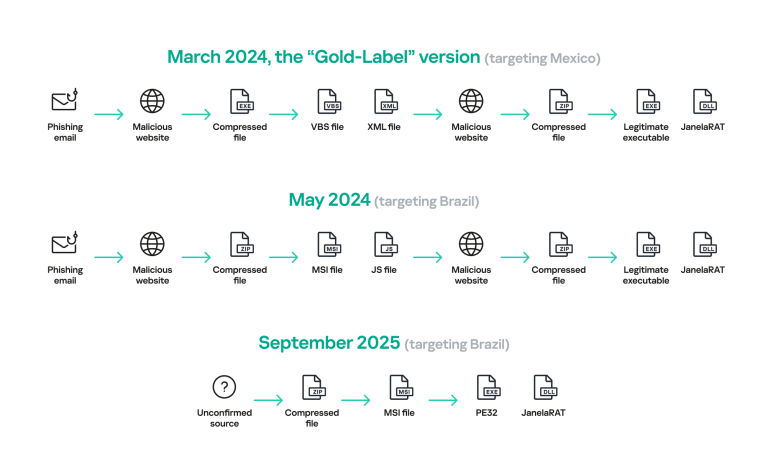
JanelaRAT targets banking users in Brazil and Mexico using window monitoring and fake updates. Learn how this 2026 threat bypasses MFA to hijack sessions.
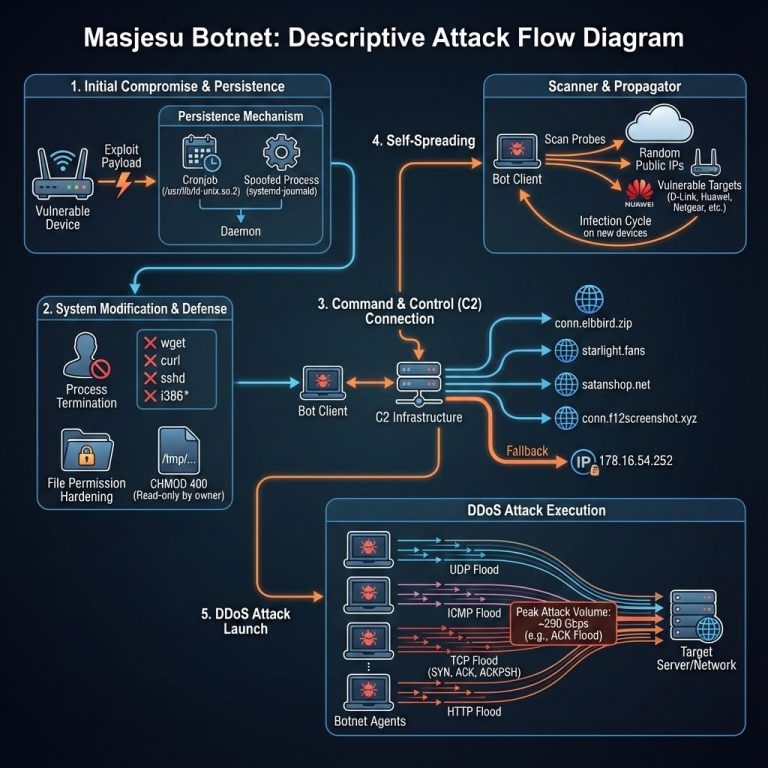
Trellix ARC reveals Masjesu, a stealthy, professional IoT botnet operational since 2023. Targeted DDoS-for-hire with a low-profile strategy. Patch now!
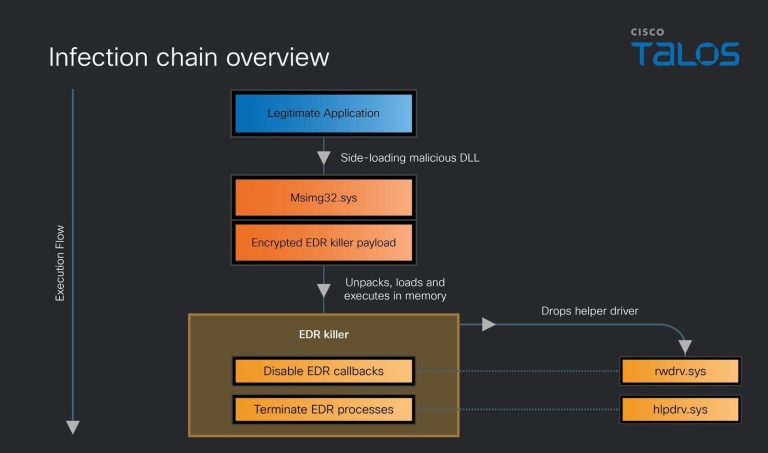
Cisco Talos unmasks a Qilin ransomware payload that terminates 300+ EDR drivers and manipulates the Windows kernel. See how this "EDR Killer" stays invisible.
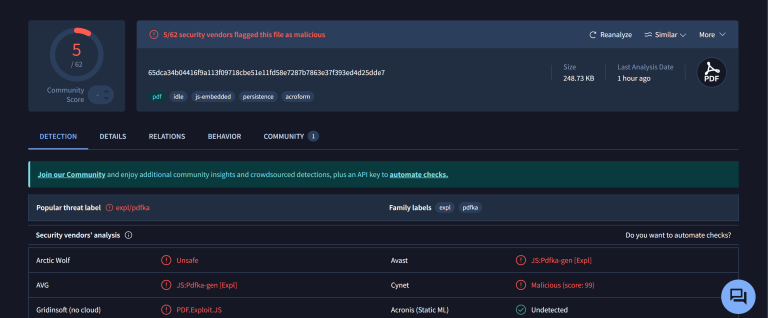
A critical Adobe Reader zero-day allows attackers to steal local files and achieve system control via malicious PDFs. Learn how the unpatched exploit works.

ASEC uncovers Kimsuky’s evolved LNK-to-Python chain abusing Dropbox for stealthy persistence. Learn how to detect this complex multi-stage backdoor.
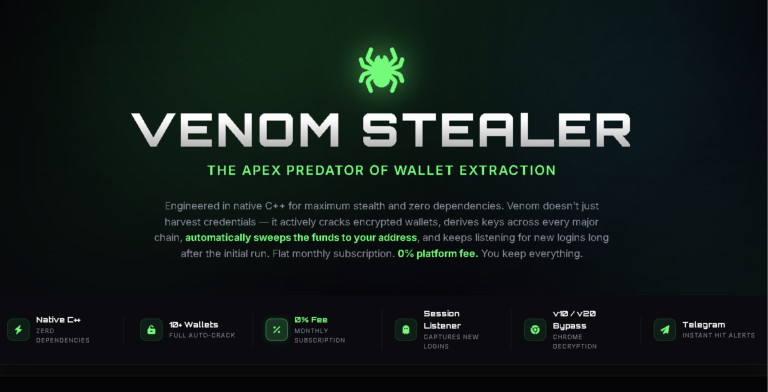
Venom Stealer is a new C++ MaaS targeting crypto wallets like Tonkeeper. It features silent UAC elevation and Chrome encryption bypass. Learn how to defend.
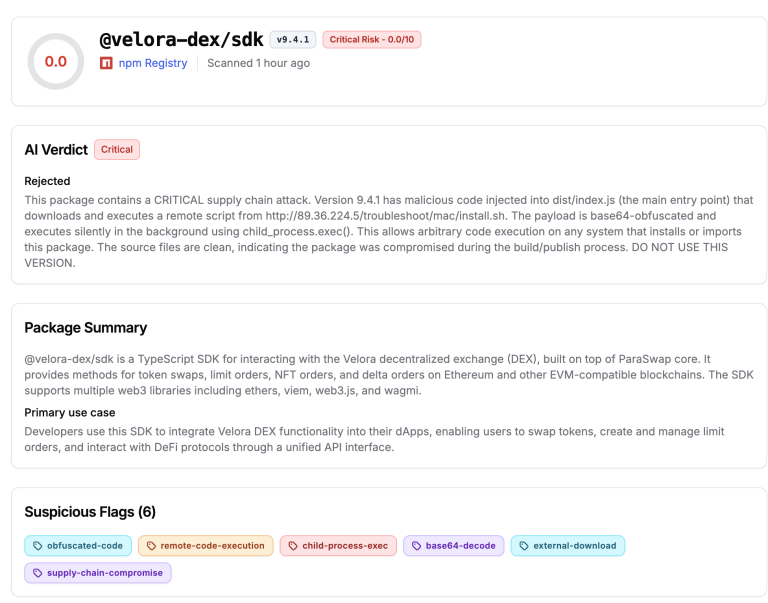
A malicious update to @velora-dex/sdk (v9.4.1) drops a stealthy macOS backdoor on import. Learn how to detect the zsh.profiler infection and rotate secrets.
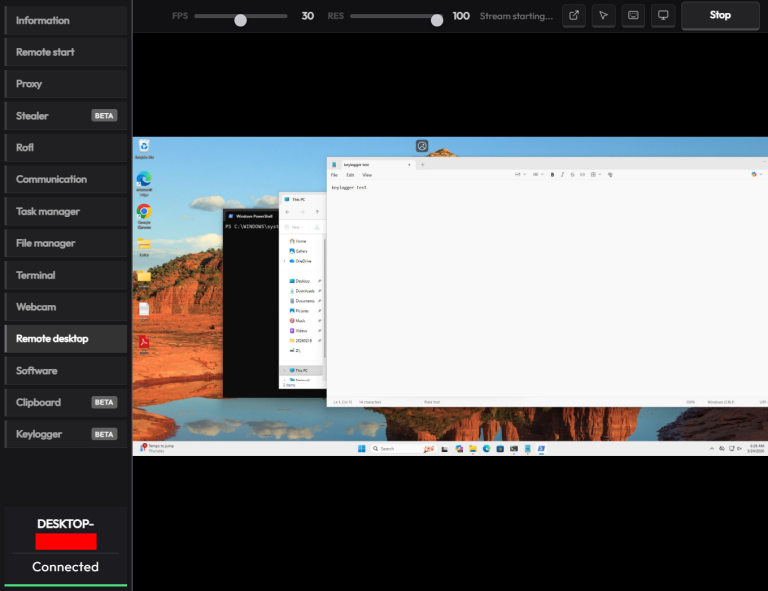
Kaspersky uncovers CrystalX RAT, a malicious MaaS on Telegram that pairs data theft with "prankware" to troll victims and lock systems. Patch now!

ThreatLabz unmasks Xloader 8.7, the evolved successor to Formbook. Learn how its advanced obfuscation and decoy C2s bypass modern security defenses.
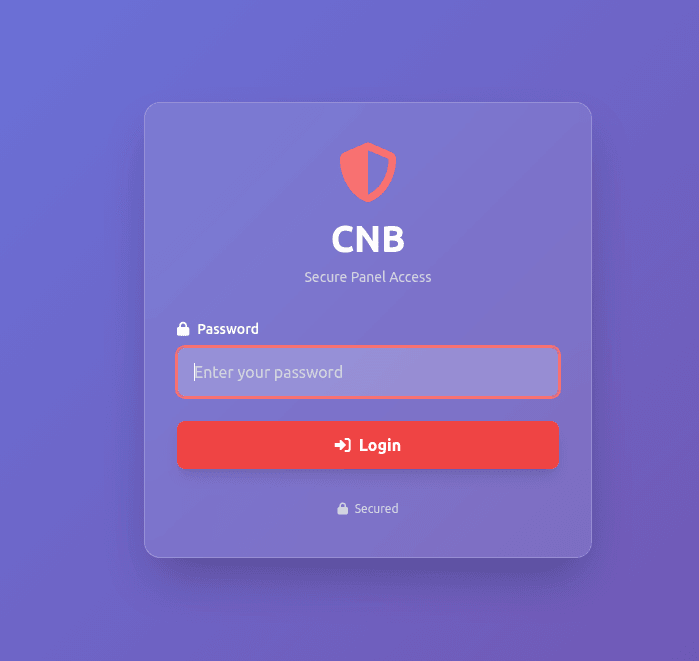
Elastic Security Labs unmasks REF1695, a threat actor using the CNB Bot and custom XMRig loaders for Monero mining and CPA fraud. Is your server a silent miner?
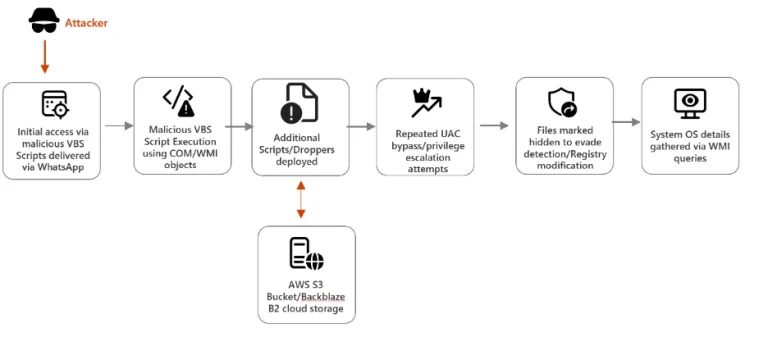
Microsoft Defender warns of a 2026 WhatsApp malware campaign using VBS and renamed system tools to hijack PCs via AWS and Tencent Cloud. Stay alert!
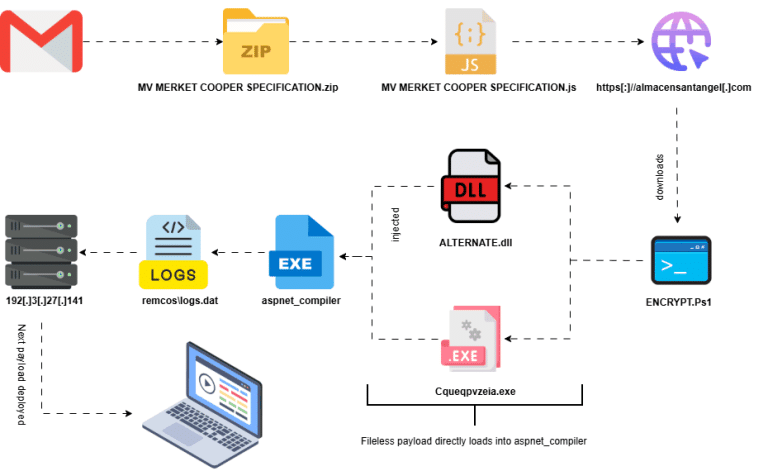
Researchers unmask a fileless Remcos RAT campaign using obfuscated JS and LOLBins to hijack systems in-memory. See the technical breakdown from Lat61.