 Do Son
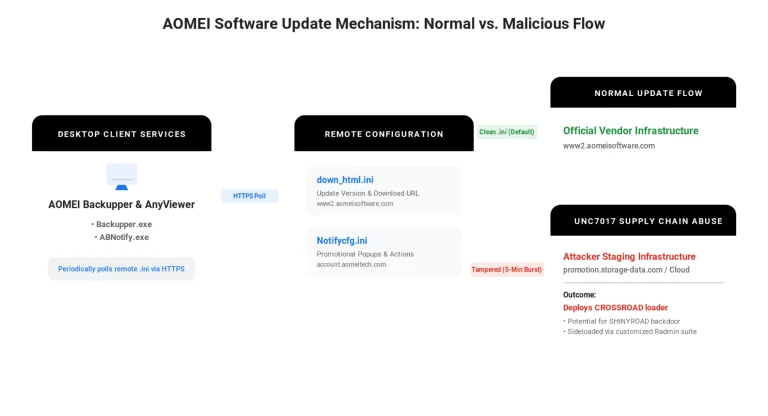
Google and Mandiant uncovered the AOMEI supply chain attack UNC7017 campaign using 5-minute server tampering to drop CROSSROAD and SHINYROAD malware.
Mandiant
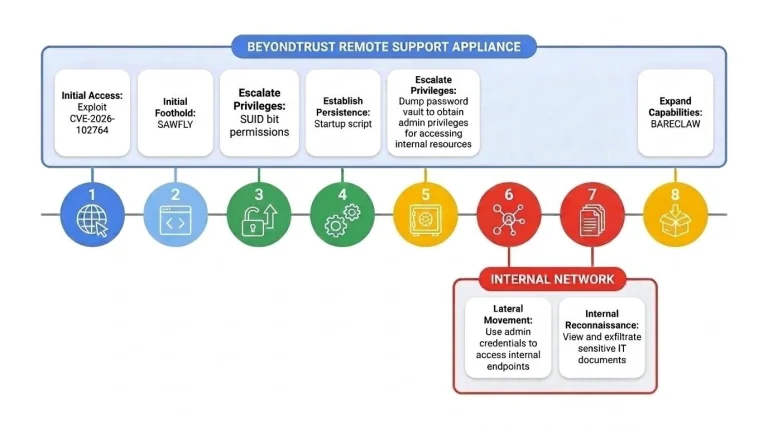
Patch CVE-2026-102764 now. This critical BeyondTrust Remote Support vulnerability is exploited in the wild as an ARMORY CASTLE zero-day.
Attackers exploit Citrix NetScaler zero-day CVE-2026-88772 for root access, then hide WHIPSHOT web shells and a SLAPSHOT tunneler. Patch now.

ShinyHunters PeopleSoft attacks are back. A one-letter WAF bypass lets the group exploit CVE-2026-35273 and plant web shells on unpatched servers.
Discover how a Google undercover analyst successfully infiltrated the TeamPCP hacking gang to prevent massive supply chain attacks and secure corporate data.
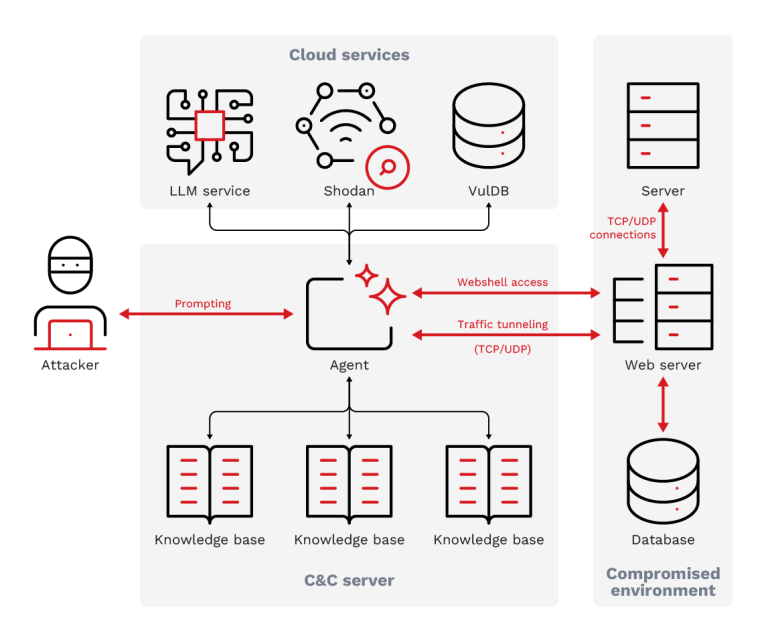
Google warns the BREEZE COMET threat actor attacks Brazilian banks to execute mass financial fraud. Learn how to protect your payment systems.

Mandiant details the UNC3753 vishing campaign targeting US law firms with fake IT calls, RMM abuse, and rapid data theft extortion.

Learn how Mandiant uncovered the critical Knowledge Deliver RCE vulnerability (CVE-2026-5426) and how to protect your systems today.
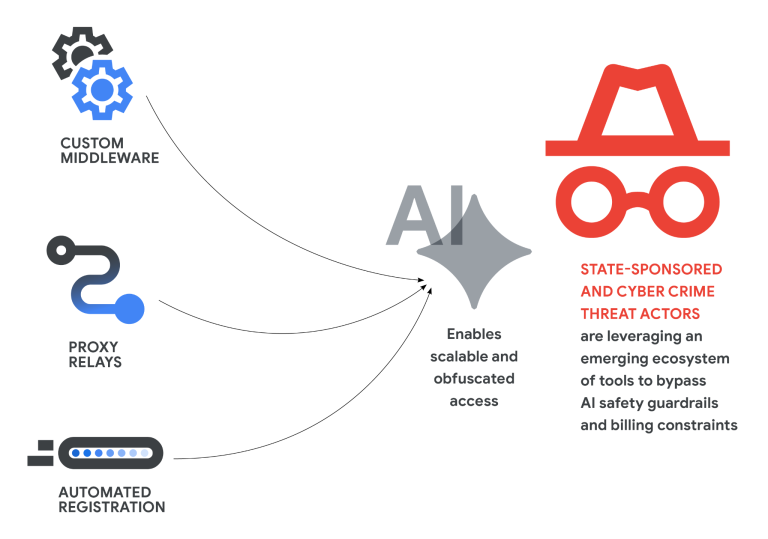
Google GTIG confirms the first AI-built zero-day exploit used in the wild. Discover how AI is industrializing cyber warfare and how Big Sleep is fighting back.

Mandiant uncovers BRICKSTORM, a threat actor hiding in VMware vSphere for 393 days. Learn how to close the visibility gap and harden your ESXi infrastructure.
Google has finalized its $32B acquisition of Wiz, the largest in its history. Discover how this "code-to-cloud" platform secures AI in a multi-cloud world.
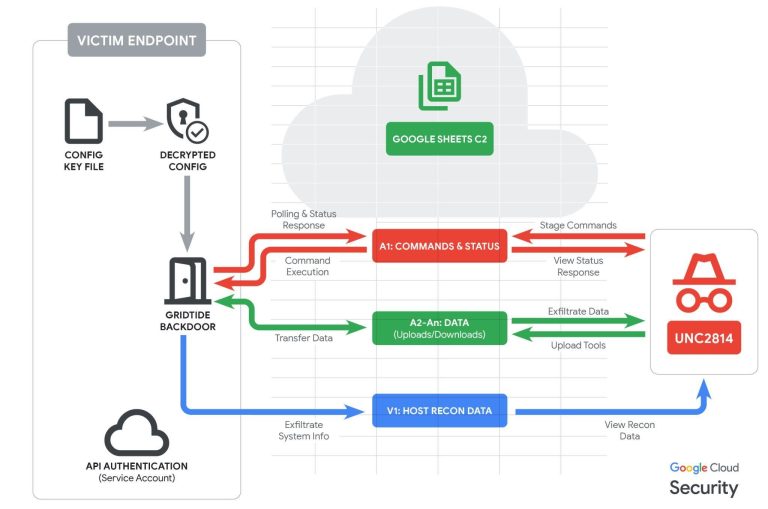
Google and Mandiant disrupt UNC2814, a China-nexus group using the GRIDTIDE backdoor to hide command-and-control traffic inside Google Sheets across 42 nations.

Mandiant reveals UNC6201 exploiting Dell RecoverPoint zero-day CVE-2026-22769. Attackers use "Ghost NICs" & GRIMBOLT malware. Patch now.
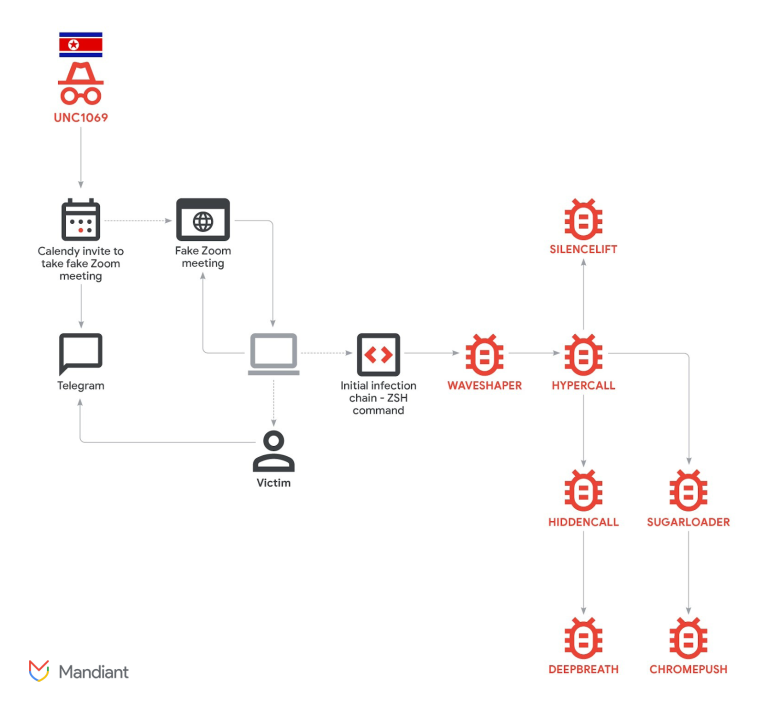
North Korean hackers (UNC1069) use AI deepfakes & "ClickFix" tactics to deploy SILENCELIFT malware. Learn how they target crypto firms via Zoom.
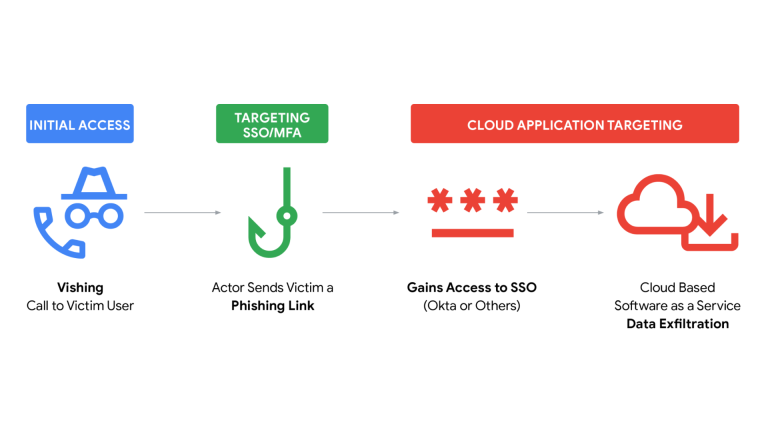
Mandiant warns of vishing rings like ShinyHunters impersonating IT support to bypass MFA and steal corporate cloud data. Verify your callers.

Mandiant exposed UNC6485 exploiting a Triofox zero-day (CVE-2025-12480). The critical flaw allows unauthenticated admin takeover by spoofing the HTTP Host header to bypass authentication checks.

Google/Mandiant linked CL0P extortion to a Zero-Day RCE flaw (CVE-2025-61882) in Oracle E-Business Suite. Attackers exploited the bug since July to steal corporate data and deploy GOLDVEIN Java shells.

A coordinated disclosure by Mandiant and Sitecore has revealed the active exploitation of a critical configuration vulnerability...

A new Mandiant report reveals a multi-stage USB malware campaign that uses DLL side-loading and stealthy loaders to deploy backdoors and coinminers.

A sophisticated spear-phishing campaign using Signal targeted Armenian civil society and government in March 2025, linked to threat actor UNC5792.

UNC3944 resurfaces as Scattered Spider, linked to DragonForce and RansomHub in new retail attacks. Mandiant warns of social engineering escalation.

Google introduces Unified Security, powered by Gemini AI, to streamline enterprise cybersecurity. Discover new AI security agents, enhanced threat detection, and data protection tools for comprehensive security management.