
 Do Son
Kaspersky uncovered the new HoneyMyte CoolClient rootkit. The HoneyMyte CoolClient rootkit deploys a kernel driver to hide malware on Windows.
Mustang Panda

Mustang Panda targets India's government and hydropower sectors, abusing Zoho WorkDrive for C2. Acronis found new ZOHOMURK and MINIRECON implants.
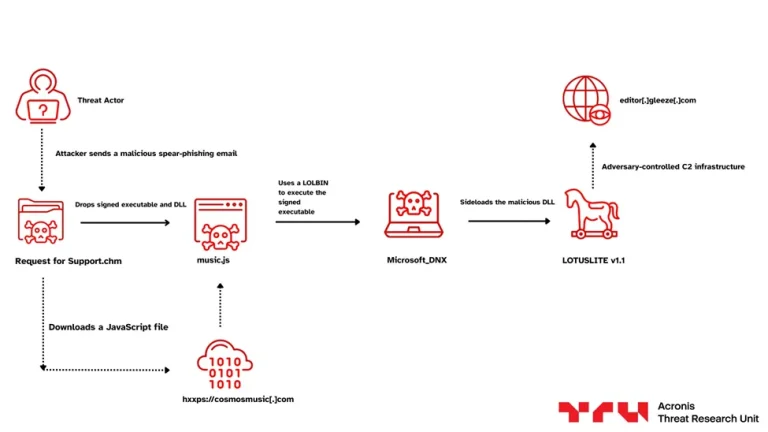
Mustang Panda targets India’s financial sector with the LOTUSLITE malware. Learn how this DLL sideloading campaign bypasses defenses for cyber-espionage.
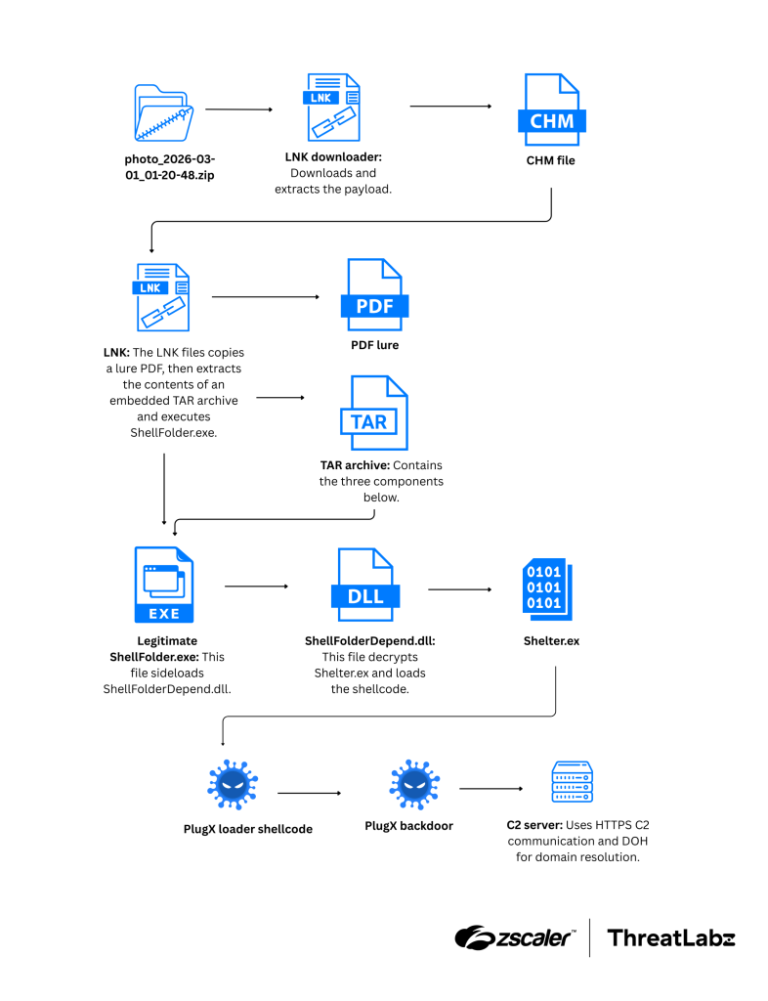
ThreatLabz reveals how China-nexus actor Mustang Panda weaponized Middle East conflict lures to deploy a stealthy PlugX backdoor within 24 hours.

Zscaler ThreatLabz reveals a surge in Middle East conflict-themed cyberattacks, uncovering 8,000+ malicious domains, LOTUSLITE backdoors, and scams.

Researcher @goyaramen reveals how PRC threat actors like Mustang Panda use expired domains and Cloudflare to mask their PlugX C2 infrastructure.

LAB52 exposes a new China-aligned espionage campaign using fake meeting invitations and G DATA antivirus components to stealthily deploy the PlugX RAT.
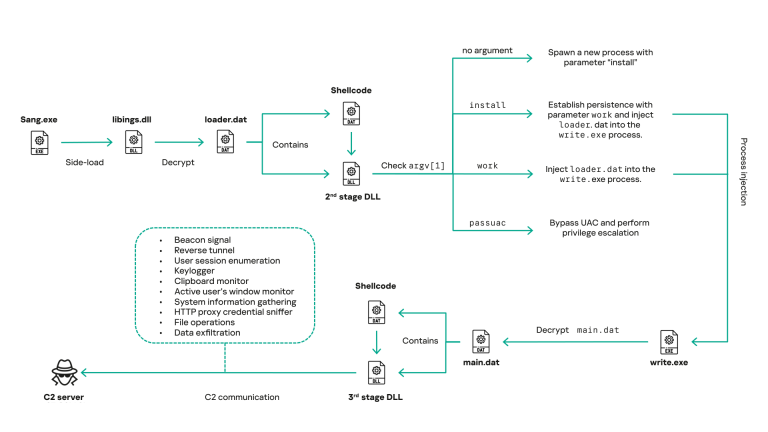
HoneyMyte (Mustang Panda) shifts to real-time surveillance using updated CoolClient. New 2025 campaign uses Pixeldrain for stealthy exfiltration.

Resecurity finds PDFSIDER, a new APT malware using DLL side-loading and AES-256-GCM encryption to bypass EDR and open covert backdoors.

Mustang Panda targets US gov with new LOTUSLITE backdoor. Campaign uses Venezuela lures and DLL sideloading to evade detection.

Taiwan's NSB reports 2.63M daily cyberattacks from China in 2025. Energy sector strikes spiked 1,000% as hybrid warfare intensifies.

Kaspersky unmasks HoneyMyte's 2025 campaign, using the ProjectConfiguration.sys kernel rootkit to deploy ToneShell backdoors with elite stealth.

A China-nexus APT, Mustang Panda, is targeting the Tibetan community using DLL sideloading and the EnumFontsW API to launch the stealthy Publoader backdoor and achieve persistence.

A new report reveals a ToneShell backdoor from Mustang Panda. The malware targets Myanmar and uses anti-analysis tricks to evade detection.
Mustang Panda, a China-aligned APT, is using the ToneShell backdoor to target government and military sectors with phishing and DLL sideloading, masquerading as a legitimate Chrome component.

Explore the Yokai backdoor malware campaign targeting the Royal Thai Police in a detailed report by Cado Security Labs.

Understand the malicious strategies employed by the Earth Preta APT Group, including the use of the TONESHELL backdoor for attacks.

U.S. authorities successfully neutralize Chinese state-sponsored cyber espionage threat by deleting PlugX malware.

Learn about the Sekoia team's groundbreaking effort to combat the PlugX worm, a notorious threat to global cybersecurity.
Uncover the operations of CeranaKeeper, a newly discovered APT group targeting governmental institutions in Thailand and other Asian countries.

Uncover the cyber espionage tactics of the Mustang Panda group and their use of the ToneShell backdoor. Explore their latest operation targeting attendees of a major defense and security summit.

Mustang Panda has been conducting a series of targeted attacks since April 2024, focusing on entities with interests in tax compliance and education