
 Do Son
APT28 used the Hookedge backdoor, SSH tunnels, and a new loader to spy on a naval shipbuilder and defense firms in two NATO countries.
NATO
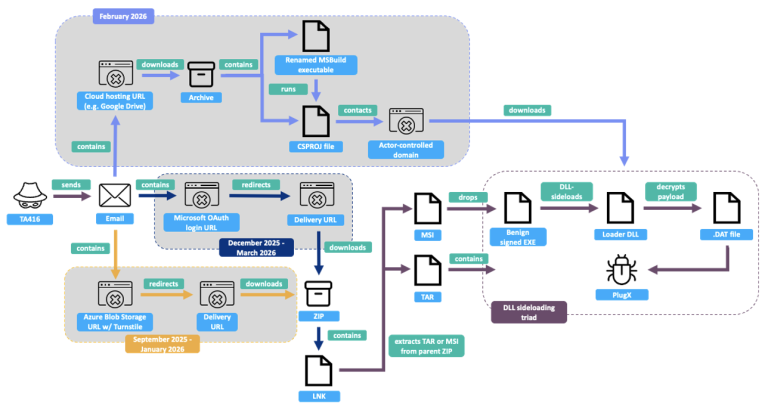
Proofpoint uncovers TA416's pivot to EU, NATO, and Middle East diplomacy. Learn how this state-linked actor uses updated PlugX and Cloudflare lures in 2026.

Pawn Storm (APT28) debuts the PRISMEX suite, weaponizing Office zero-days against NATO logistics. Discover the stealth tactics behind this 2026 offensive.

Recorded Future’s Insikt Group warns of a two-year escalation in Russian hybrid warfare. From cyber sabotage to airspace incursions, NATO faces a new doctrine.

A Russian APT is targeting Transnistria and NATO entities using blurred HTML attachments to harvest credentials. The 2025 campaign mimics official presidential decrees.

Google exposed pro-Russia IO campaigns (Portal Kombat, Doppelganger) exploiting a Polish drone incursion to deflect blame from Russia, undermine NATO, and discredit the Polish government.

Microsoft identified Void Blizzard, a new Russia-affiliated cyberespionage group, targeting critical sectors in NATO countries and Ukraine.

A joint advisory warns that Russia's APT28 (Fancy Bear) is actively targeting logistics and tech companies supporting Ukraine with espionage and data exfiltration.
The Ukrainian Ukrainian Security Service (SBU) stated in a statement on June 5, 2018, that the Ukrainian...