 Do Son
A critical Nginx UI RCE vulnerability (CVE-2026-107806) is publicly disclosed with PoC exploit code. Admins must patch now to prevent system takeover.
Nginx UI

Critical 9.0 CVSS RCE in Nginx UI (CVE-2026-42238) exploits a 10-minute unauthenticated window. Attackers can seize root control. Patch to the latest version now.
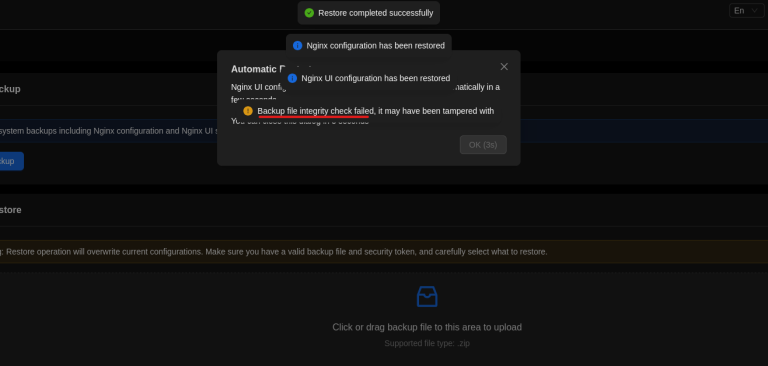
Public PoC exploit and details are out for Nginx UI’s 9.4 CVSS backup flaw (CVE-2026-33026). Attackers can hijack servers via tampered backups. Update now!
Public PoC code and full details are out for a 9.8 CVSS flaw in Nginx UI (CVE-2026-33032). With no official patch, servers are at risk. Secure yours now!

A critical 9.8 CVSS flaw (CVE-2026-27944) in Nginx UI lets hackers download and decrypt full system backups via an open API. Update and rotate secrets!