 Do Son
Cisco Talos exposed a UAT-12643 Overlord RAT campaign using Solana blockchain memos and UAT-12643 Overlord RAT malware to steal crypto and credentials.
North Korea
Genians uncovered a Kimsuky NodeLinkRAT malware campaign using reply-based spearphishing, aNotepad C2 notes, and XenoRAT to spy on South Korean targets.
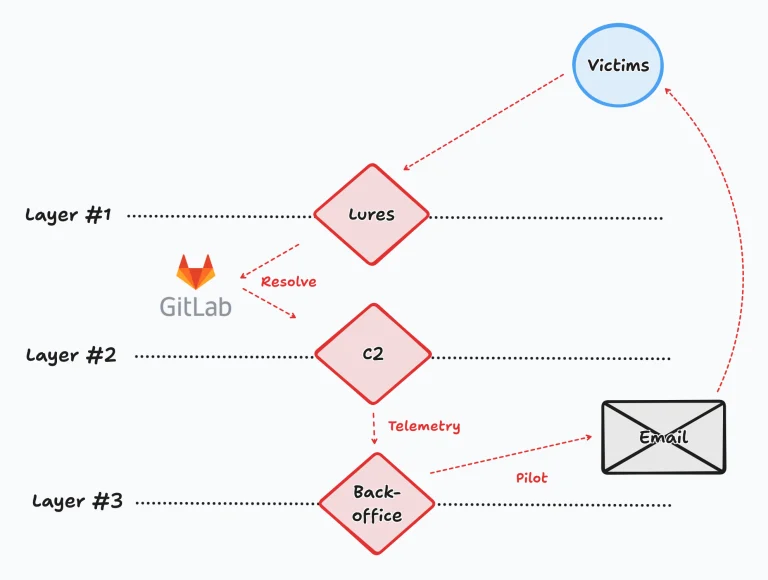
Stormshield exposed the North Korean Trigram campaign spoofing 50 Web3 and AI brands with ClickFix lures and GitLab relays to infect developers.
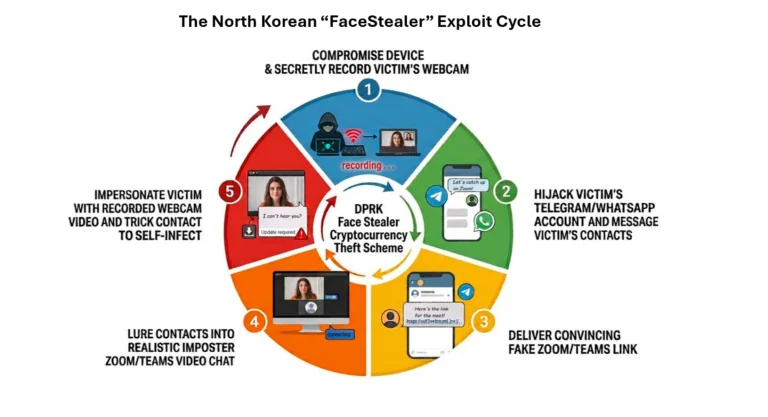
The DOJ and FBI disrupted the North Korea FaceStealer scheme after $400M in crypto thefts and seized $1.2B stolen in a $6B Binance exchange hack.
The Binance hack hit USD 6.34B via a fake job interview, an abused AI tool and EIP-7702 delegation. The FBI points to North Korea.
The FBI attributed the $6.3 billion Binance crypto heist to North Korean state hackers, sparking denials from Pyongyang amid ongoing asset recovery efforts.
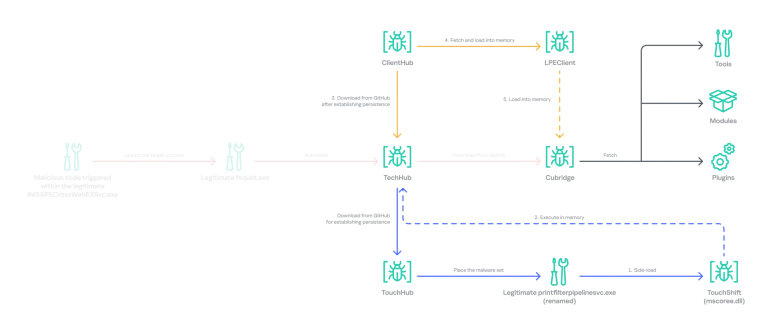
In Operation FlashHole, the Lazarus Group used AI-made lure sites, CrossWeb EX, and GitHub C2 to spy on South Korean firms. Here is how.
The DOJ and FBI raided DPRK IT worker laptop farms in Texas, seizing 187 devices and charging 14 suspects in a $3M fraud scheme hitting 70+ US firms.
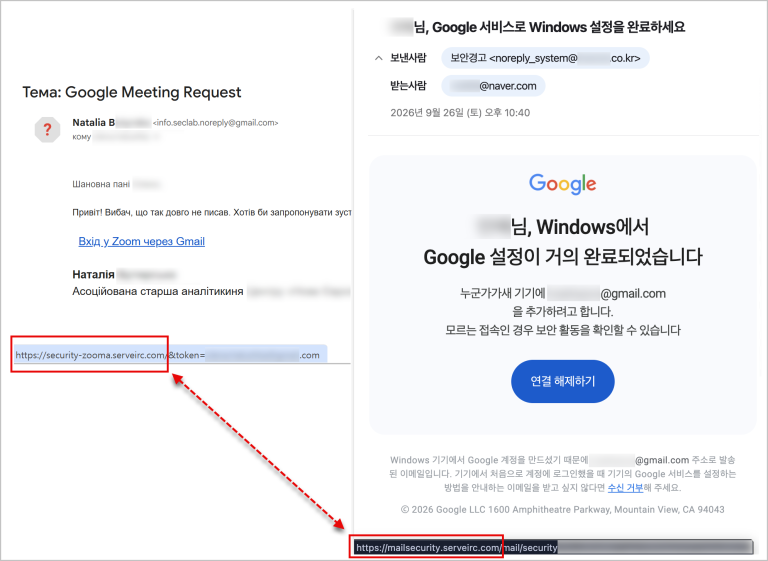
Kimsuky spear phishing lures target Ukrainian security experts with fake invitations, as Operation GitPower abuses GitHub and GitLab.
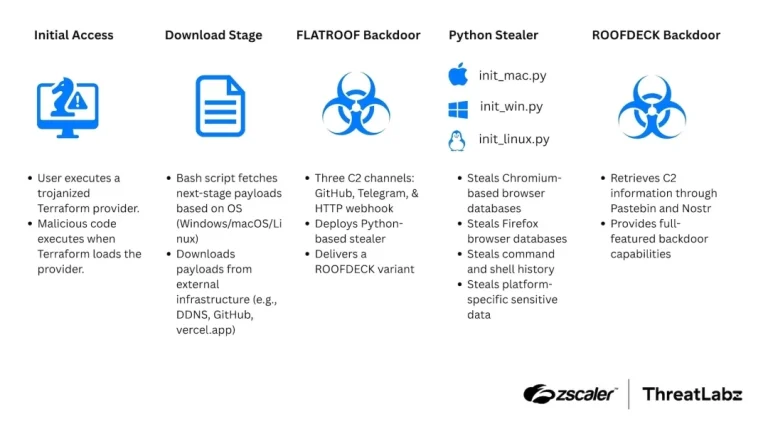
Suspected TraderTraitor hackers used a trojanized Terraform provider to drop FLATROOF and ROOFDECK malware on macOS, Linux, and Windows.
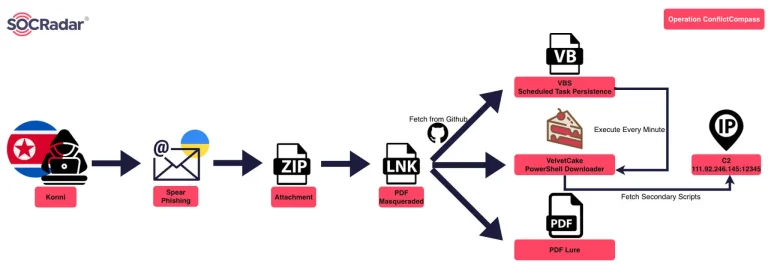
SOCRadar uncovered the Konni Operation Conflict Compass campaign targeting Ukraine. Learn how Operation Conflict Compass uses fake PDFs and VelvetCake.
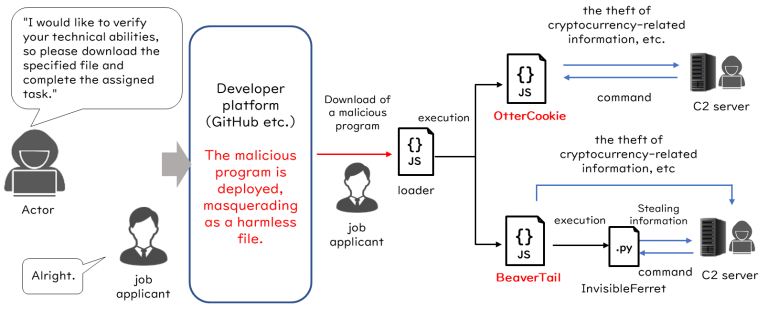
Discover how the North Korean WaterPlum cyber actor group uses fake job interviews to steal crypto and infiltrate networks globally.
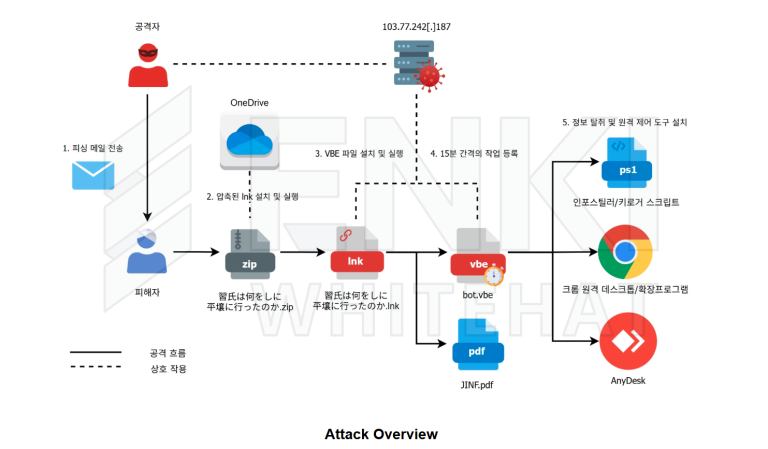
Recent Kimsuky spear phishing campaigns abuse remote control tools and AI extensions to target victims in Japan and South Korea. Read the full analysis.
Amazon ties North Korean hackers to open-source supply chain attacks on the axios, debug, and chalk NPM packages. Here's how the campaign worked.

North Korea's ClickFake Interview campaign targets crypto pros with fake skill tests, dropping the PylangGhost RAT on Windows and GolangGhost on macOS.

ENKI WhiteHat traced a Kimsuky Gomir variant into South Korean groupware vendors, plus a new DriveTroy backdoor that hides its C2 in Google Drive.

Elastic found a Contagious Interview campaign using fake coding interviews and SVG steganography to steal developer credentials and crypto wallets.
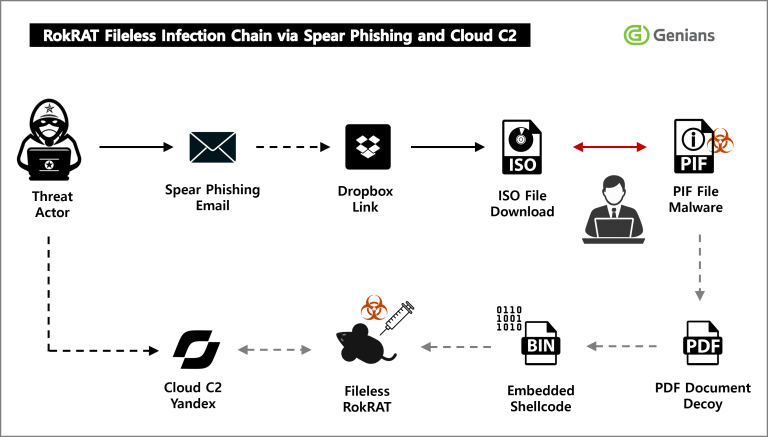
Genians exposed Operation Capsule Vault, an APT37 campaign. The RokRAT malware hides inside a fake PDF to spy on academics and researchers.

New Lazarus npm malware masquerades as Rollup polyfills, hiding remote-access and wallet-theft payloads. JFrog uncovered six malicious packages.

UNK_DeadDrop phishing campaigns are targeting developers with fake jobs to deliver Overlord malware. Learn how to defend against this North Korean threat.

DOJ sentences U.S. enablers for running North Korean "laptop farms." Learn how the DPRK breached 70 companies and funded weapons via stolen identities.
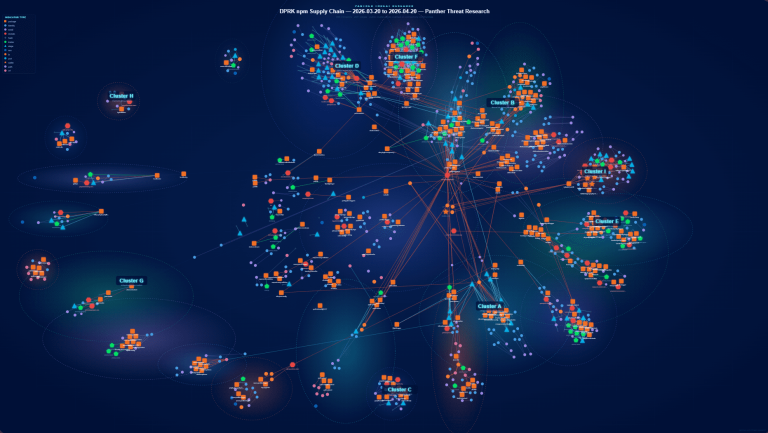
Panther Research exposes a massive 2026 DPRK npm campaign using blockchain dead-drops to steal crypto keys and AI secrets. Secure your CI/CD pipelines now.