
 Do Son
A new report reveals a malware campaign using SEO poisoning to target Chinese-speaking users. Attackers use fake software sites to deliver Hiddengh0st and Winos.
phishing

The FBI has issued a FLASH Alert warning about UNC6040 and UNC6395, two groups actively compromising Salesforce via vishing and malicious OAuth apps to steal data.

A new report reveals a major surge in phishing attacks targeting U.S. energy companies like Chevron, using cloned websites to steal credentials and financial data.

Okta Threat Intelligence uncovers VoidProxy, a dangerous new Phishing-as-a-Service (PhaaS) platform that uses Adversary-in-the-Middle attacks to bypass MFA.

A new report reveals a massive, unencrypted database with 1.6 million gym phone calls and voicemails was exposed, raising serious risks of AI-powered fraud.

A key npm maintainer's account was compromised, leading to a supply chain attack. Malicious code in popular packages is stealing crypto during transactions.

A new phishing campaign is spreading MostereRAT, a sophisticated RAT that uses a Chinese scripting language and advanced evasion to bypass antivirus and EDR solutions.

A new report reveals a sophisticated XWorm backdoor campaign that uses .lnk files and a multi-stage infection chain to gain stealthy and persistent control of Windows systems.
A new report reveals that Stealerium, an open-source infostealer, is being used in phishing campaigns to steal credentials, crypto wallets, and sensitive data.

A new report reveals a phishing campaign using fake ads and login pages to steal credentials from employees in the hospitality and vacation rental industry.

A new report from Huntress reveals a hybrid ClickFix attack that abuses the Windows search protocol and malicious LNK files to deliver MetaStealer malware.

A new report reveals a rise in phishing campaigns that abuse email marketing platforms and cloud services to evade detection and steal credentials from victims.

A new report reveals the TAOTH cyber-espionage campaign, which hijacks software updates and uses spear-phishing to deliver malware to high-value targets in Asia.

SikkahBot, a new Android malware, is impersonating scholarship apps to steal financial data and automate transactions from students in Bangladesh.
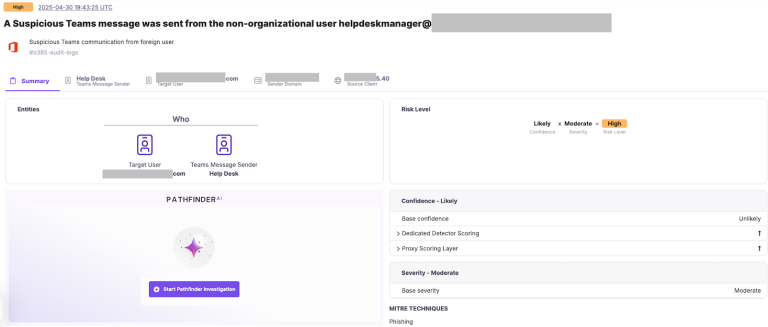
A new report reveals that attackers are abusing Microsoft Teams' collaboration features to launch phishing, vishing, and malware attacks, bypassing security warnings.

A new report reveals how scammers are exploiting the Ganesh Chaturthi festival in India with fake websites, lottery fraud, and phishing to steal money and data.
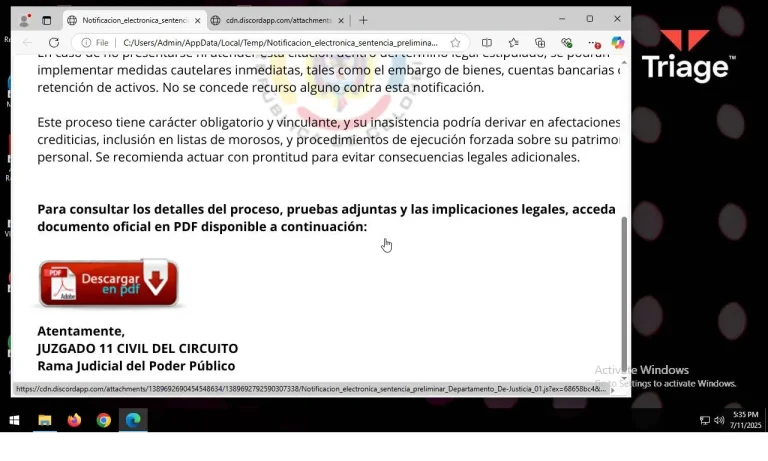
A new report reveals the Blind Eagle hacking group is using spearphishing and commodity RATs to conduct cyber espionage against Colombian government and private sector targets.

A new report reveals a mobile malware campaign in Indonesia impersonating the state pension fund TASPEN to steal financial and personal data from civil servants.

A new report reveals a persistent phishing campaign targeting ScreenConnect super admins. The stolen credentials are being sold to ransomware affiliates for future attacks.

A new phishing campaign called ZipLine reverses the attack by tricking victims into initiating contact. It targets supply chains and deploys a custom in-memory implant.

A new report reveals a rapidly growing global phishing campaign using fake voicemails and purchase orders to distribute UpCrypter, a sophisticated malware loader.
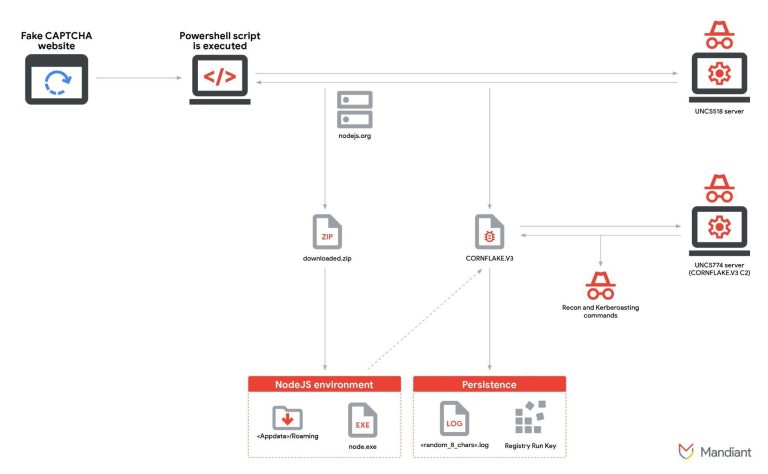
UNC5518 is using "ClickFix," a new technique that weaponizes fake CAPTCHAs to trick users into launching malware and providing access to other criminal groups.