
 Do Son
Librarian Ghouls APT launches a new cyber-espionage and cryptojacking campaign targeting Russia and CIS, using legitimate tools for stealth.
phishing

Beware 'imad213,' a fake Instagram booster stealing credentials via social engineering and bot services. Learn how to protect your account.

A new info-stealer, SoraAI.lnk, is leveraging OpenAI's Sora popularity to infect users. Learn how this sophisticated malware works and how to protect your data.

An old Microsoft Office vulnerability (CVE-2017-0199) is being exploited in a new phishing campaign to deploy the FormBook infostealer malware. Update now!

Proofpoint reveals TA397 (Bitter APT) is an India-aligned state-backed group conducting long-term espionage campaigns globally, targeting rivals and partners.

A sophisticated spear-phishing campaign using Signal targeted Armenian civil society and government in March 2025, linked to threat actor UNC5792.

A sophisticated "ClickFix" phishing campaign uses fake Booking.com CAPTCHAs to deliver RATs and info stealers to the hotel and travel industry.
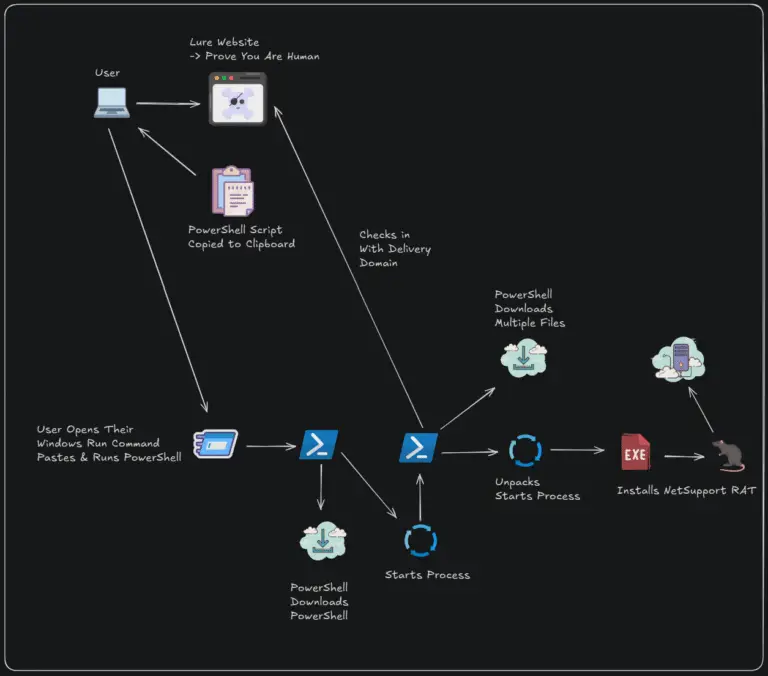
A new campaign uses fake DocuSign & Gitcodes pages to trick users into manually installing NetSupport RAT, gaining remote control.

IBM X-Force warns of a new phishing campaign by Hive0131 targeting Colombian users with DCRat malware via fake legal notices.

BitMEX security team infiltrates Lazarus Group's infrastructure after a phishing attempt, exposing their tactics and even a hacker's real location.

Haozi, a Chinese Phishing-as-a-Service platform, is back, offering no-code phishing kits and full support. Learn how this service enables easy cybercrime.

Netskope reveals a surge in phishing on Glitch, abusing the platform to bypass MFA and steal credentials, mainly targeting Navy Federal Credit Union members.

Learn how interactive sandboxes like ANY.RUN can detect and analyze Microsoft 365 phishing attacks in real-time, preventing silent breaches and data exfiltration.

A stealthy spear-phishing campaign uses fake Rothschild job offers to trick finance execs into installing NetBird RAT, gaining remote access.

A new global malware campaign delivers PureHVNC RAT via fake job offers and complex, multi-stage obfuscation, making detection extremely difficult.

A malware campaign is hijacking WordPress sites with fake Java update pop-ups, tricking visitors into downloading malicious executables.

New campaigns by Silent Werewolf leverage custom C# loaders and advanced delivery to target entities in Russia and Moldova for cyber-espionage.

Microsoft identified Void Blizzard, a new Russia-affiliated cyberespionage group, targeting critical sectors in NATO countries and Ukraine.

A fake Google Meet page on compromised WordPress sites tricks users into manually running PowerShell commands, delivering remote access malware.

Russian-aligned TAG-110 (APT28) is launching a cyber-espionage campaign using macro-enabled Word docs to target Tajikistan's public sector for intelligence.

Over 40 malicious Chrome extensions, disguised as legitimate tools, are stealing cookies, logins, and impersonating users, many still live on the Web Store.

The Rhadamanthys stealer is back with targeted phishing attacks across Central and Eastern Europe, using fake copyright infringement lures.