
 Do Son
CoinMarketCap suffered a client-side attack on June 20, 2025, using a fake "doodle" graphic to deliver Inferno Drainer, stealing over $43,000 from user wallets.
phishing

Shadow Vector campaign uses malicious SVGs in phishing emails to deliver AsyncRAT & RemcosRAT in Colombia, leveraging advanced DLL sideloading and in-memory execution.

Scammers hijack Google ads & brand websites to show fake support numbers. Malwarebytes exposes this new "search hijacking" scam tactic.

A new campaign uses encrypted VBScript (.VBE) to deploy a fileless Masslogger infostealer, which hides in the Windows Registry to steal credentials and evade antivirus.

The SERPENTINE#CLOUD campaign exploits Cloudflare Tunnel subdomains and LNK files to deliver in-memory RATs like AsyncRAT and Remcos, evading detection.

AntiDot, an Android trojan from LARVA-398, is infecting thousands of devices via MaaS, using MediaProjection API and Accessibility Services to steal financial and personal data.

A Russian state-sponsored APT, UNC6293 (likely APT29), is exploiting Google Application-Specific Passwords in a sophisticated phishing campaign targeting critics of Russia

North Korean APT Famous Chollima (Wagemole) is using a new Python-based RAT, PylangGhost, in fake job interviews to target crypto professionals and steal credentials.
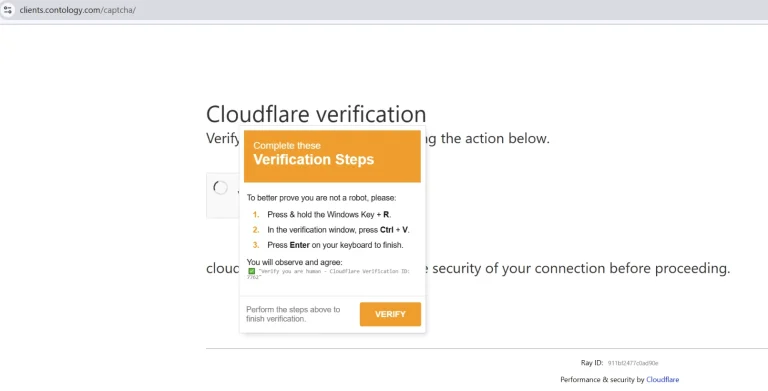
Elastic uncovers a sophisticated ClickFix campaign deploying the GHOSTPULSE loader to deliver ARECHCLIENT2 malware, leveraging social engineering for credential theft and remote access.

A new wave of invoice-themed phishing emails is distributing the Sorillus RAT across Europe, leveraging legitimate platforms like OneDrive and Ngrok for stealthy delivery.
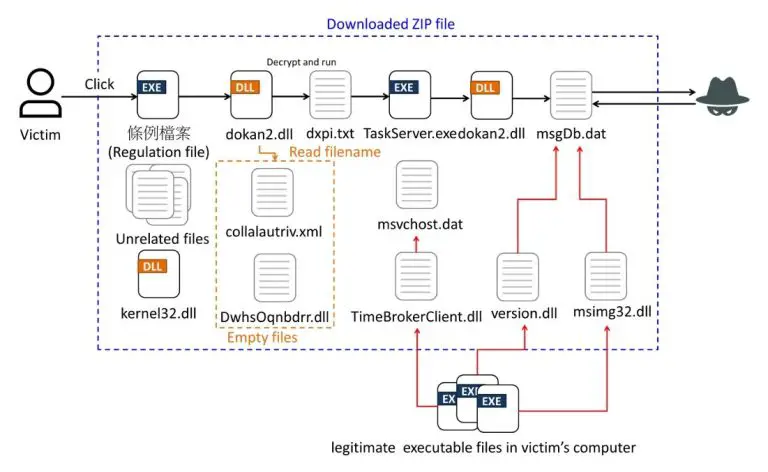
A sophisticated malware campaign is targeting Taiwan, impersonating the National Taxation Bureau to distribute Winos 4.0, HoldingHands RAT, and Gh0stCringe.

Kimsuky APT is using HWP documents and stealthy AnyDesk backdoors in a new phishing campaign to infiltrate systems under the guise of academic collaboration.

Team46 (TaxOff) is exploiting a Google Chrome sandbox escape zero-day (CVE-2025-2783) to deploy the multi-layered Trinper malware via phishing campaigns

Malicious phishing apps are bypassing Google Play Store security, tricking users into revealing crypto wallet seed phrases and draining funds. Beware and never share your seed

Katz Stealer, a new stealthy MaaS, is actively stealing data from browsers, crypto wallets, and apps, using advanced evasion tactics like steganography and Discord hijacking.

HijackLoader and DeerStealer are surging, using ClickFix social engineering and sophisticated evasion to bypass defenses and exfiltrate sensitive data.
Attackers are hijacking expired Discord invite links, redirecting users to malicious servers that deploy AsyncRAT and crypto-stealing Skuld Stealer via clever social engineering.

HelloTDS is a sophisticated traffic direction system delivering millions to FakeCaptcha and other malware via advanced fingerprinting and evasive tactics.

Clicking unsubscribe links can be risky, confirming your email is active or leading to phishing. Use email client features or block senders to stay safe.

A new Sekoia report reveals a surge in AitM phishing, leveraging industrialized PhaaS kits to bypass MFA and compromise Microsoft 365 and Google accounts.

Rapid7 reveals BlackSuit ransomware affiliates are adopting Black Basta tactics, using email bombing, fake Quick Assist scams, and evolving Java RATs.

Silent Push uncovers "GhostVendors," a massive online fraud operation using 4,000+ fake domains and Facebook ads to impersonate brands and scam consumers.