
 Do Son
The notorious Genesis Market is back! A new campaign deploys a malicious browser extension via Lumma Stealer to covertly harvest user data.
phishing
Attackers exploit JSONP flaws in Google APIs to inject malicious scripts into e-commerce sites, silently redirecting users to fake payment pages.

A reflected XSS flaw in GlobalProtect (CVE-2025-0133) allows malicious JavaScript execution. PoC exploit code is available. Update your PAN-OS.

Phishing campaign uses deceptive domains to target Kuwaiti sectors. Details on how attackers impersonate brands and steal credentials.

North Korean threat actor TA406 intensifies cyber espionage against Ukraine, using phishing and malware to gather political intelligence.

Horabot malware targets Latin America with fake invoices, hijacking Outlook to spread phishing emails and steal data via stealthy scripting.

Europol-backed operation busts €3M investment fraud network deceiving 100+ victims via fake trading platform. Arrests made in Cyprus, Israel, Albania.

New email campaign uses tricky tactics and legitimate services to deliver the RATty Trojan in Spain, Italy, and Portugal. Stay alert for invoice scams!

Watch out! Sophisticated Facebook ads lure crypto users to download malware via fake platforms and celebrity endorsements. Bitdefender warns of data theft.

Cisco Talos warns of a Brazil-focused spam campaign abusing legitimate remote access tools (N-able, PDQ) to gain full system control. Stay vigilant!

Silent Push uncovers crypto scam using Twitter ad loophole to spoof CNN and Apple, luring users into buying fake iTokens via misleading redirects.

Cofense Intelligence reports a new phishing tactic using blob URIs to bypass Secure Email Gateways. Attackers use these local URIs to hide phishing pages.

A sophisticated phishing campaign, Oriental Gudgeon, has been targeting Japanese companies since October 2024. It uses advanced cloaking to steal user data.

Inferno Drainer returns stronger than ever, using Discord phishing and blockchain obfuscation to steal millions in crypto.
A sophisticated phishing campaign, possibly by APT36, spoofs Indian government sites and uses ClickFix tactics to target Windows and Linux users.
Seqrite Labs uncovers APT36 phishing campaign using Pahalgam terror attack-themed lures to deploy Crimson RAT against Indian government targets.
Cisco Talos reports on AiTM attacks that bypass MFA by using reverse proxies to steal credentials and session cookies, leading to account takeover.

Silent Push uncovers Lazarus Group's campaign using fake crypto job offers to spread malware (BeaverTail, InvisibleFerret, OtterCookie), targeting job seekers.

Discover SessionShark, a sophisticated phishing toolkit designed to bypass Microsoft Office 365 multi-factor authentication by stealing session tokens.
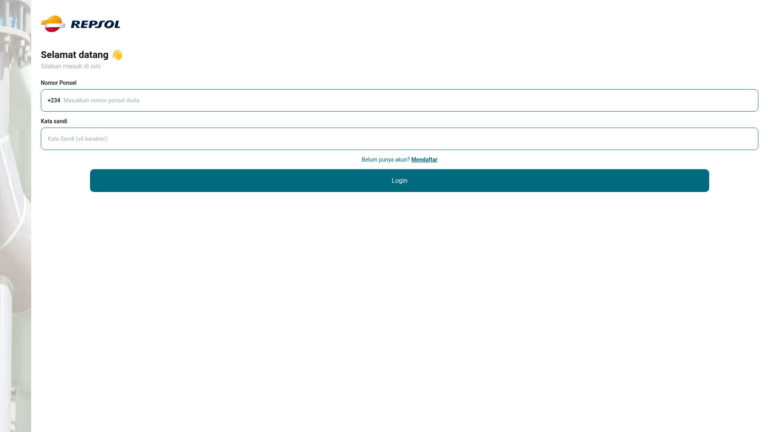
Power Parasites targets users with job and investment scams using fake domains mimicking Siemens, Repsol, Netflix, and more, Silent Push reports.

A new phishing campaign targets WooCommerce users with fake security alerts. Learn how attackers use IDN homographs and malicious plugins to compromise stores.

Volexity uncovers Russian threat actors abusing Microsoft 365 OAuth flows via phishing, impersonation, and device registration to access email accounts.