
 Do Son
Kaspersky GReAT uncovered OctLurk and SilkLurk, two new memory-resident backdoors targeting Central Asian governments since January 2025.
PlugX
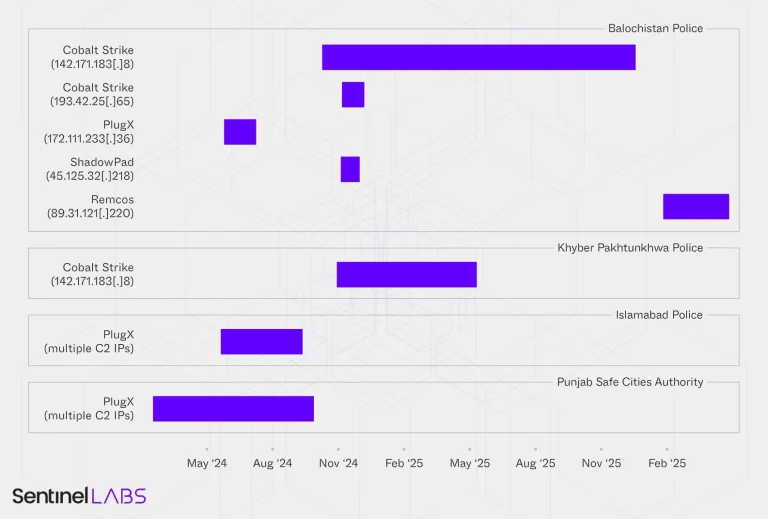
SentinelLABS found Chinese cyberespionage and India-nexus actors converging on Pakistani law enforcement, hitting Balochistan Police records and citizens.
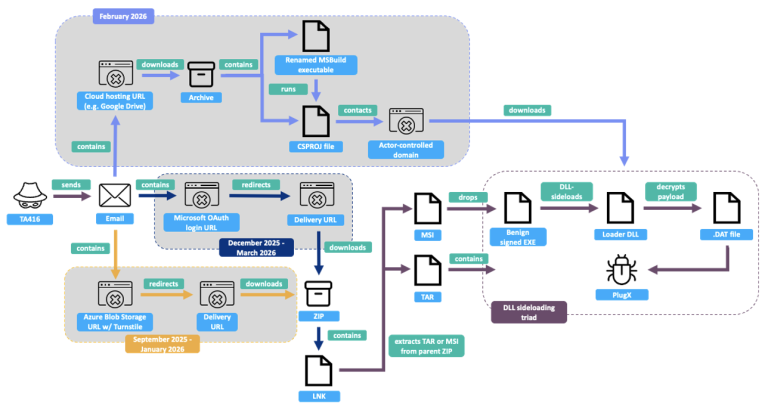
Proofpoint uncovers TA416's pivot to EU, NATO, and Middle East diplomacy. Learn how this state-linked actor uses updated PlugX and Cloudflare lures in 2026.

Chinese APTs like Camaro Dragon are targeting Qatar with PlugX malware and Cobalt Strike, weaponizing Middle East tensions for cyberespionage.

Researcher @goyaramen reveals how PRC threat actors like Mustang Panda use expired domains and Cloudflare to mask their PlugX C2 infrastructure.

Arctic Wolf exposed Chinese APT UNC6384 exploiting the ZDI-CAN-25373 Windows LNK flaw to target European diplomats. The multi-stage attack uses DLL sideloading via a Canon binary to deploy the PlugX RAT.

A Chinese APT used fake Cloudflare verification pages and malicious LNK files to inject PlugX via DLL sideloading into a Serbian aviation agency, aiming for long-term espionage.

Cisco Talos uncovers a long-running espionage campaign using a new PlugX backdoor. The malware shows strong links to Chinese APT groups Naikon and BackdoorDiplomacy.
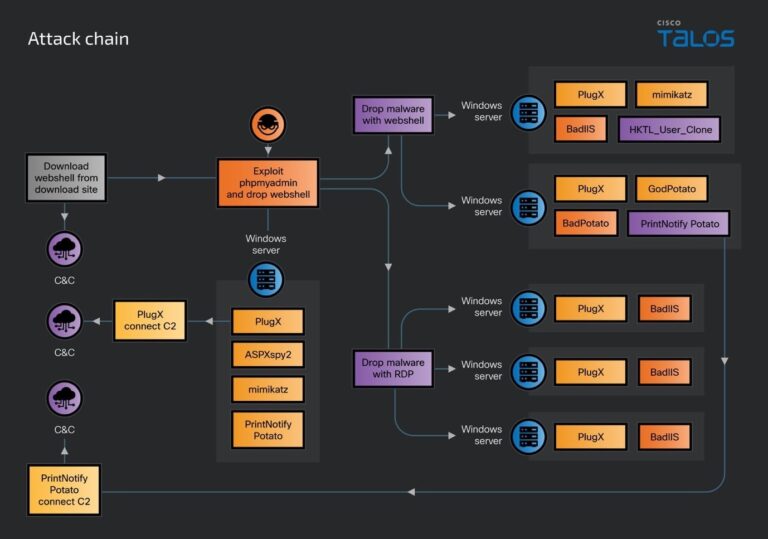
Learn about DragonRank, a Chinese threat actor specializing in SEO manipulation and cyberattacks. Find out how this group compromises websites and manipulates search engine rankings.

Discover the evolving tactics of Earth Preta, a notorious cyber espionage group, and their heightened threat to government entities in the APAC region.

Learn about the large-scale operation to remove the PlugX trojan from infected devices. Discover how the French police and cybersecurity company Sekoia are combating this threat.
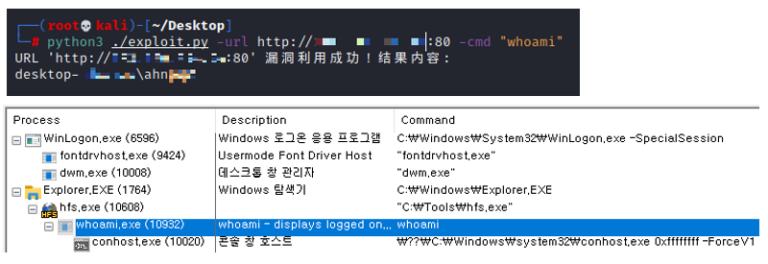
ASEC has observed a variety of attacks targeting HFS servers, including: Cryptomining, RATs and Backdoors, and Infiltration of GoThief malware

Mustang Panda has been conducting a series of targeted attacks since April 2024, focusing on entities with interests in tax compliance and education
In the shadowy world of cyber threats, PlugX stands out as a sophisticated and insidious malware, leaving...

warnings about a fresh wave of attacks targeting Chinese internet users, orchestrated by the hacker collective known as Higaisa