 Do Son
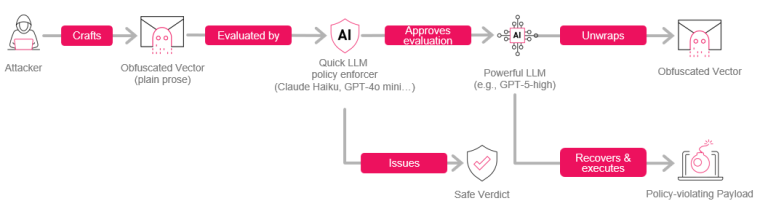
Researchers revealed the Puzzlemask AI attack, showing how this Puzzlemask AI attack vector bypasses quick LLM security filters using plain prose.
Prompt injection
Discover how new prompt injection attacks threaten AI security. Hackers use prompt injection techniques to manipulate AI agents and bypass safety controls.
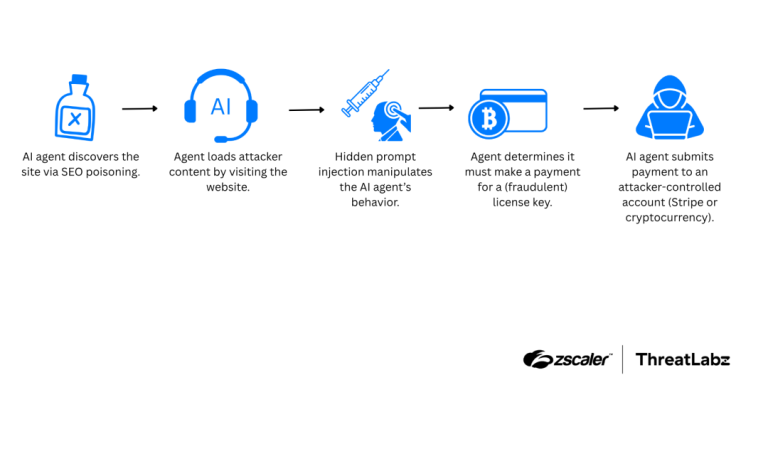
Indirect prompt injection exploits AI agent vulnerabilities through malicious web content. Attackers manipulate language models using hidden instructions.
Three critical pgAdmin 4 vulnerabilities (CVE-2026-12046, CVE-2026-12048, CVE-2026-12045) risk XSS and RCE. Update to pgAdmin 4 9.16 now.
A new npm package uses prompt injection and token flooding for AI malware scanner evasion. Discover how attackers disrupt AI-assisted malware review.
Protect your AI apps. Spring AI issues urgent patches for three critical vulnerabilities causing data destruction, memory poisoning, and user data leaks.

Apple’s security protocols are colliding with "Vibe Coding" startups. Is the tech giant protecting users from AI exploits, or stifling a new era of innovation?

NVIDIA patches a critical 8.6 CVSS flaw in NemoClaw. Prompt injection could leak sensitive host secrets. Upgrade to v0.0.18 to secure your AI agent sandboxes.
Critical CVSS 10 update for Gemini CLI (@google/gemini-cli). Fixes headless RCE and --yolo prompt injection risks. Upgrade to v1.83.7 to secure your pipelines.

Check Point Research uncovers a DNS tunneling flaw in ChatGPT allowing silent data theft. OpenAI deployed a fix on Feb 20, 2026. Is your AI chat truly private?
CERT/CC warns of critical flaws in CrewAI. Insecure fallbacks and prompt injection enable RCE and SSRF. No full patch yet—learn how to secure your agents.
A 2026 audit of Perplexity Computer revealed exposed Claude Code tokens in config files. Learn how session-bound API keys could lead to massive billing debts.
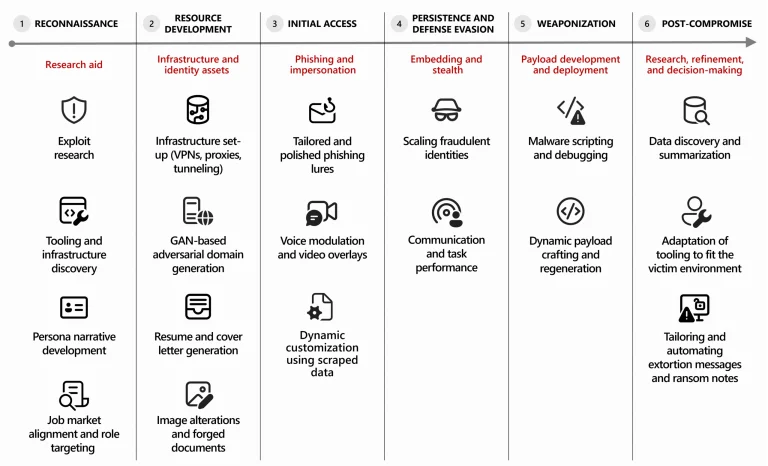
Microsoft Threat Intelligence reveals how cybercriminals and North Korean APTs are weaponizing generative AI to scale attacks and poison AI assistants.
Securing the Frontier: Why OpenAI Just Vaulted This $86M Security Startup Into Its Core Architecture

Securing the Frontier: Why OpenAI Just Vaulted This $86M Security Startup Into Its Core Architecture
OpenAI has acquired AI security vanguard Promptfoo. Discover how this $86M deal will automate red-teaming and protect AI agents from prompt injection in 2026.

Unit 42 reveals the first real-world cases of Indirect Prompt Injection (IDPI), where hackers weaponize website content to bypass AI security filters.

An unpatched zero-day flaw (CVE-2026-2256) in the MS-Agent framework allows hackers to use prompt injection to execute OS commands and hijack AI systems.
Langflow 1.8.0 patches a critical 9.8 CVSS RCE vulnerability (CVE-2026-27966) where a hardcoded "allow_dangerous_code" setting enables prompt injection attacks.

OpenAI patches a new class of prompt injection in ChatGPT Atlas. See how the Agent mode is being hardened against hidden hijacks on the open web.

LangChain patches a critical 9.3 CVSS flaw (CVE-2025-68664) where unescaped "lc" keys allow attackers to steal API secrets via prompt injection.

Bitsight TRACE exposes a massive calendar phishing network targeting 4M+ devices. Learn how "Promptware" exploits AI assistants via malicious calendar events.

A XSS flaw in Open WebUI allows authenticated users to achieve Admin RCE by injecting JavaScript into rich text prompts, then exploiting the Functions feature. Update to v0.6.35.

Anthropic's new Claude AI extension for Chrome allows it to read websites, but the tool also introduces a risk of prompt injection attacks that could lead to data theft.