 Do Son
Kerio Connect vulnerability CVE-2026-112353, a stored XSS flaw via SVG attachments, is exploited in the wild to steal mailboxes. Update to 10.0.8p2.
Proofpoint
Microsoft and Proofpoint executed a CoGUI phishing kit takedown, seizing domains from YAM Store and Iron Man after 1B scam messages hit 75,000 firms.
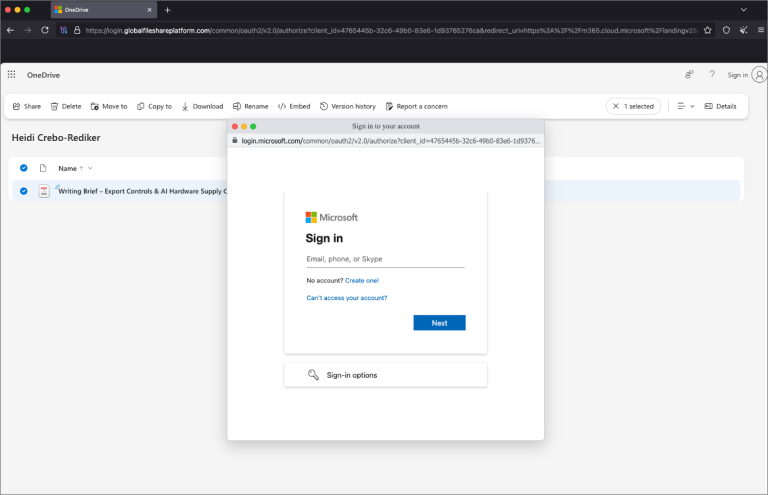
Proofpoint exposed China-aligned TA419 credential phishing targeting AI experts. This TA419 credential phishing campaign uses AitM lures to steal logins.
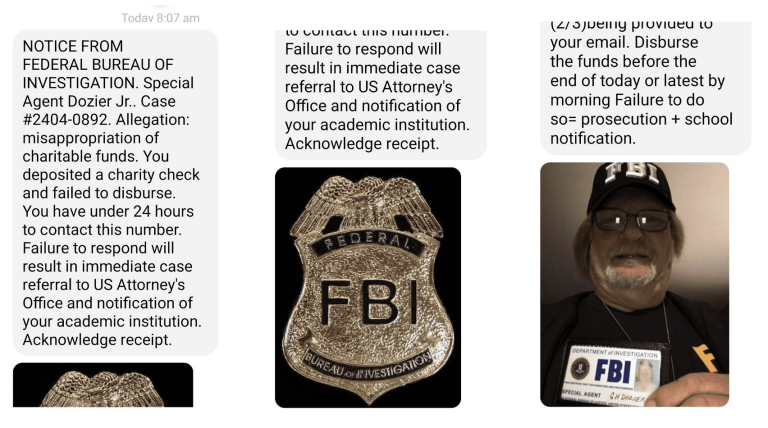
University job scams are spreading through .edu account takeover. Proofpoint shows how fraudsters phish logins, then send fake jobs and bogus checks.

A new TeamFiltration password spray campaign targeted Chilean firms. Learn how this TeamFiltration password spray compromised dormant cloud accounts.
Proofpoint found the PackClient RAT sold on Telegram and used by Chinese-speaking TA4922 malware operators in tax-themed phishing attacks.

Proofpoint details the Cruciferra crypter service that cloaks RATs and infostealers using BYOVD EDR tampering and 90+ custom encryption routines.

Proofpoint ties TA488 and TA458 to half-click exploits and webmail zero-days that steal email from Ukrainian, NATO and US government mailservers.

Proofpoint details OAuth client ID spoofing, a stealthy account enumeration technique probing Microsoft Entra ID without a successful sign-in event.
Read this Proofpoint cybercrime analysis on the surge of TA4922 malware campaigns targeting organizations globally with advanced evasion tactics.

AI "vibe coding" and the EvilTokens PhaaS platform are supercharging device code phishing to bypass Microsoft 365 MFA. Secure your network today!

Proofpoint monitors a 30-day supply chain attack using "signing-as-a-service" to bypass Windows security. Protect your load boards and fleet payments now.
Proofpoint warns that 10% of M365 account takeovers use malicious mailbox rules to steal data and hide alerts. Secure your cloud identity—check your rules!
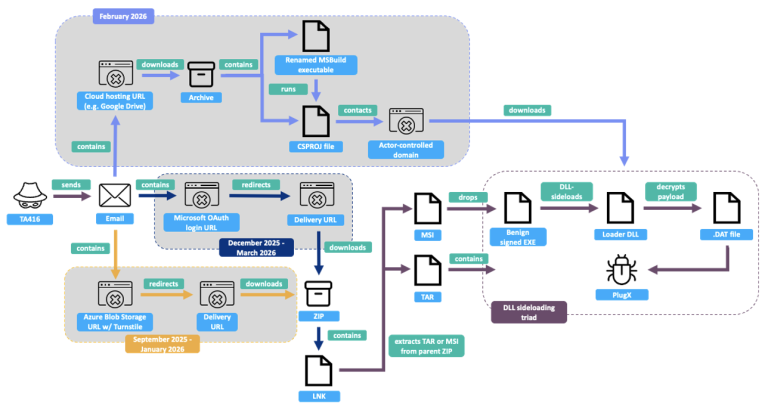
Proofpoint uncovers TA416's pivot to EU, NATO, and Middle East diplomacy. Learn how this state-linked actor uses updated PlugX and Cloudflare lures in 2026.

Proofpoint identifies a surge in 2026 tax scams using RMM tools (39%) to bypass security. Learn how TA4922 and TA2730 target your data this filing season.

Proofpoint details 'CursorJack', a novel exploit using malicious MCP deeplinks in the Cursor AI editor to execute arbitrary code on developer machines.
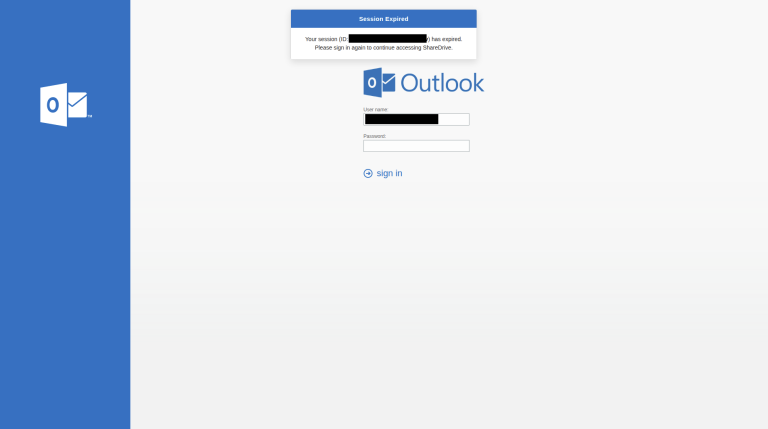
Proofpoint reveals Iran-aligned TA453 is exploiting Operation Epic Fury to launch targeted credential phishing campaigns against U.S. think tanks.
Proofpoint exposes TrustConnect, a new Malware-as-a-Service masquerading as an IT tool. The AI-assisted fake RMM software replaces dismantled threats.

TA584 triples activity with new "Tsundere Bot" malware. Attackers use invisible Registry keys to hide persistence. Read the Proofpoint analysis.

Proofpoint warns of a surge in device code phishing where attackers abuse Microsoft 365 OAuth flows to hijack accounts and bypass MFA.

Proofpoint exposed TA585, a self-reliant group that uses ClickFix phishing and private C2 infrastructure (CoreSecThree) to deploy MonsterV2 RAT (available for up to $2,000/month) with Hidden VNC capabilities.

A new report reveals Chinese threat actor TA415 is targeting U.S. policy organizations with sophisticated spearphishing campaigns to gather intelligence.