
 Do Son
OneUptime 10.0.7 patches a critical 10.0 CVSS vulnerability (CVE-2026-27728). Attackers can use traceroute probes to execute root commands and steal data.
rce

Node.js library basic-ftp patches a critical 9.1 CVSS path traversal flaw (CVE-2026-27699). Malicious FTP servers can overwrite any file on the client machine.

Centreon issues urgent patches for a 9.9 CVSS path traversal and a 9.1 RCE vulnerability in CLAPI. Secure your monitoring infrastructure—update now!

n8n patches three critical 9.4 CVSS vulnerabilities (CVE-2026-27497, 27577, 27495) allowing remote code execution via Merge nodes and sandboxes. Update now!

ServiceNow patches a critical 9.2 CVSS RCE vulnerability (CVE-2026-0542) in its AI sandbox. Unauthenticated users could execute code remotely. Patch now!
Trend Micro issues a critical patch for Apex One to fix 9.8 severity vulnerabilities (CVE-2025-71210) that allow remote code execution. Update your console now!

Juniper Networks warns of a critical 9.8 CVSS root vulnerability (CVE-2026-21902) in PTX Series routers. Unauthenticated attackers can gain complete control.
Researcher Justin Swartz uncovers a regression of the 1999 telnetd flaw. Remote attackers can bypass authentication and seize root control via environment variables.

The DFIR Report reveals how a persistent attacker exploited CVE-2023-46604 twice in 18 days to deploy LockBit ransomware. Patch your ActiveMQ servers now!

Zyxel issues urgent patches for a critical 9.8 severity flaw (CVE-2025-13942) in UPnP functions that allows remote attackers to execute OS commands. Patch now!

SolarWinds patches four critical 9.1 CVSS RCE vulnerabilities in Serv-U. Attackers can create admin users and execute code as root. Update to 15.5.4 now!

Broadcom warns of a high-severity RCE flaw (CVE-2026-22719) in VMware Aria Operations. Attackers can execute commands during system migrations. Patch now!

Unit 42 warns of active attacks on critical BeyondTrust flaw CVE-2026-1731. Hackers bypass auth for RCE and data theft. Patch self-hosted instances now.

Critical path traversal flaws (CVE-2026-26065, CVE-2026-26064) in the Calibre e-book manager allow RCE via malicious PDB and ODT files. Update to 9.3.0.

Critical flaws in Live Server, Code Runner, and more expose 128M+ developers to file theft and remote code execution. Is your VS Code workspace secure?

Urgent: PostgreSQL patches 5 flaws, including 3 critical RCEs (CVSS 8.8). Attackers can execute code as OS user via text manipulation. Update v14-18.
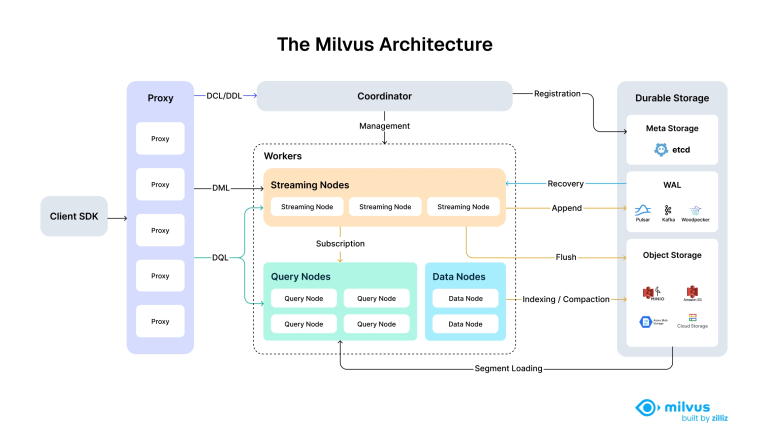
Critical Milvus flaw (CVSS 9.8) exposes port 9091. Unauthenticated attackers can steal secrets & delete data. Update to v2.5.27 or v2.6.10 immediately.

Microsoft patches critical Windows Notepad flaw CVE-2026-20841 (CVSS 8.8). Malicious Markdown links allow Remote Code Execution. Update now.

Critical Unstructured library flaw CVE-2025-64712 (CVSS 9.8) allows RCE via malicious .msg files. 4M+ downloads affected. Update to v0.18.18 now.

Samsung MagicInfo9 has critical flaws (CVSS 9.8) including hardcoded passwords and RCE. Update to v21.1090.1 immediately to secure your digital signage.

Critical Ingress-Nginx flaws (CVE-2026-1580) allow RCE and secret theft via config injection. Upgrade to v1.13.7 or v1.14.3 immediately to secure K8s.
Hikvision patches high-severity command injection (CVE-2026-0709) in DS-3WAP access points. Authenticated attackers can execute code. Update now.